Third-Party Risk Management & Vendor Due Diligence System
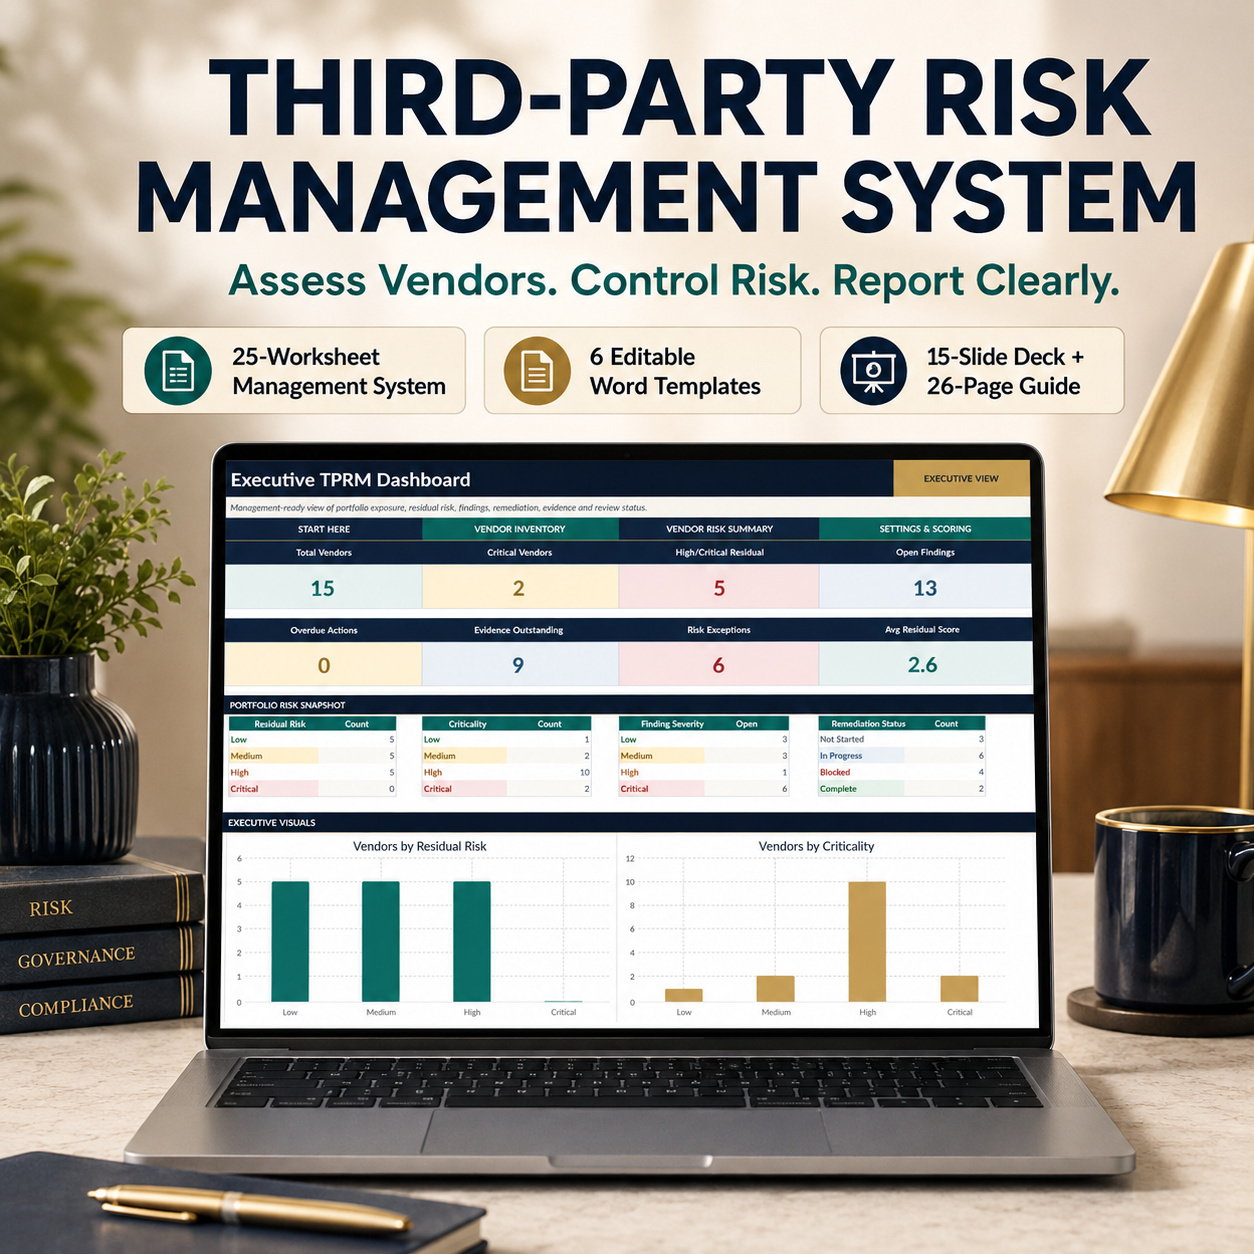
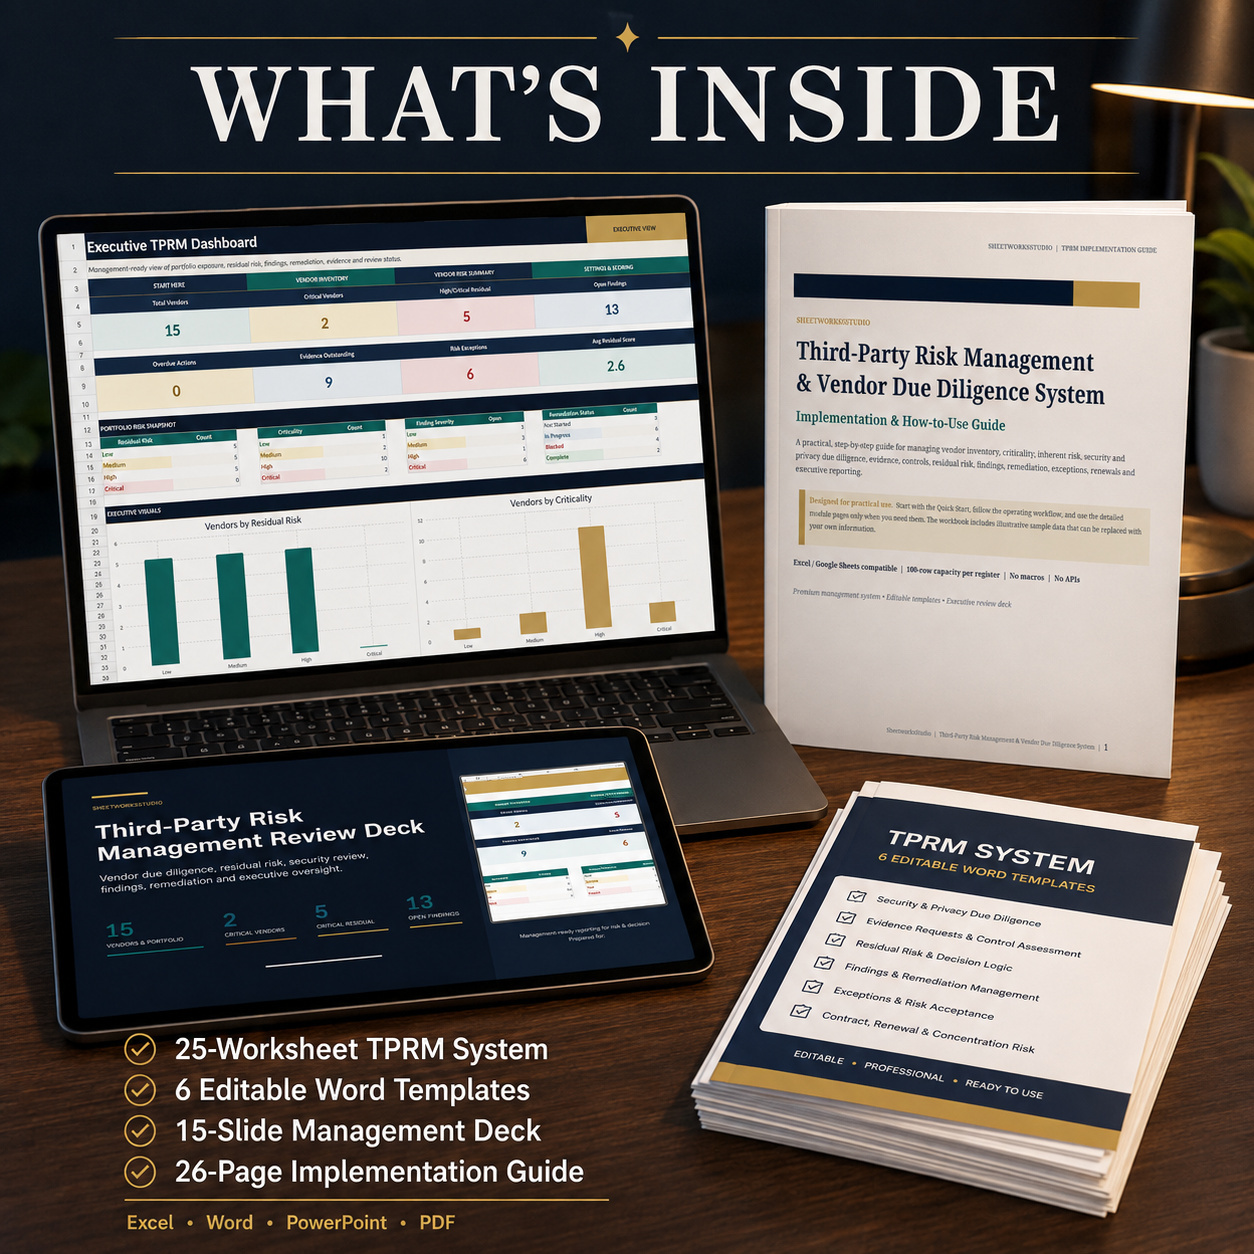
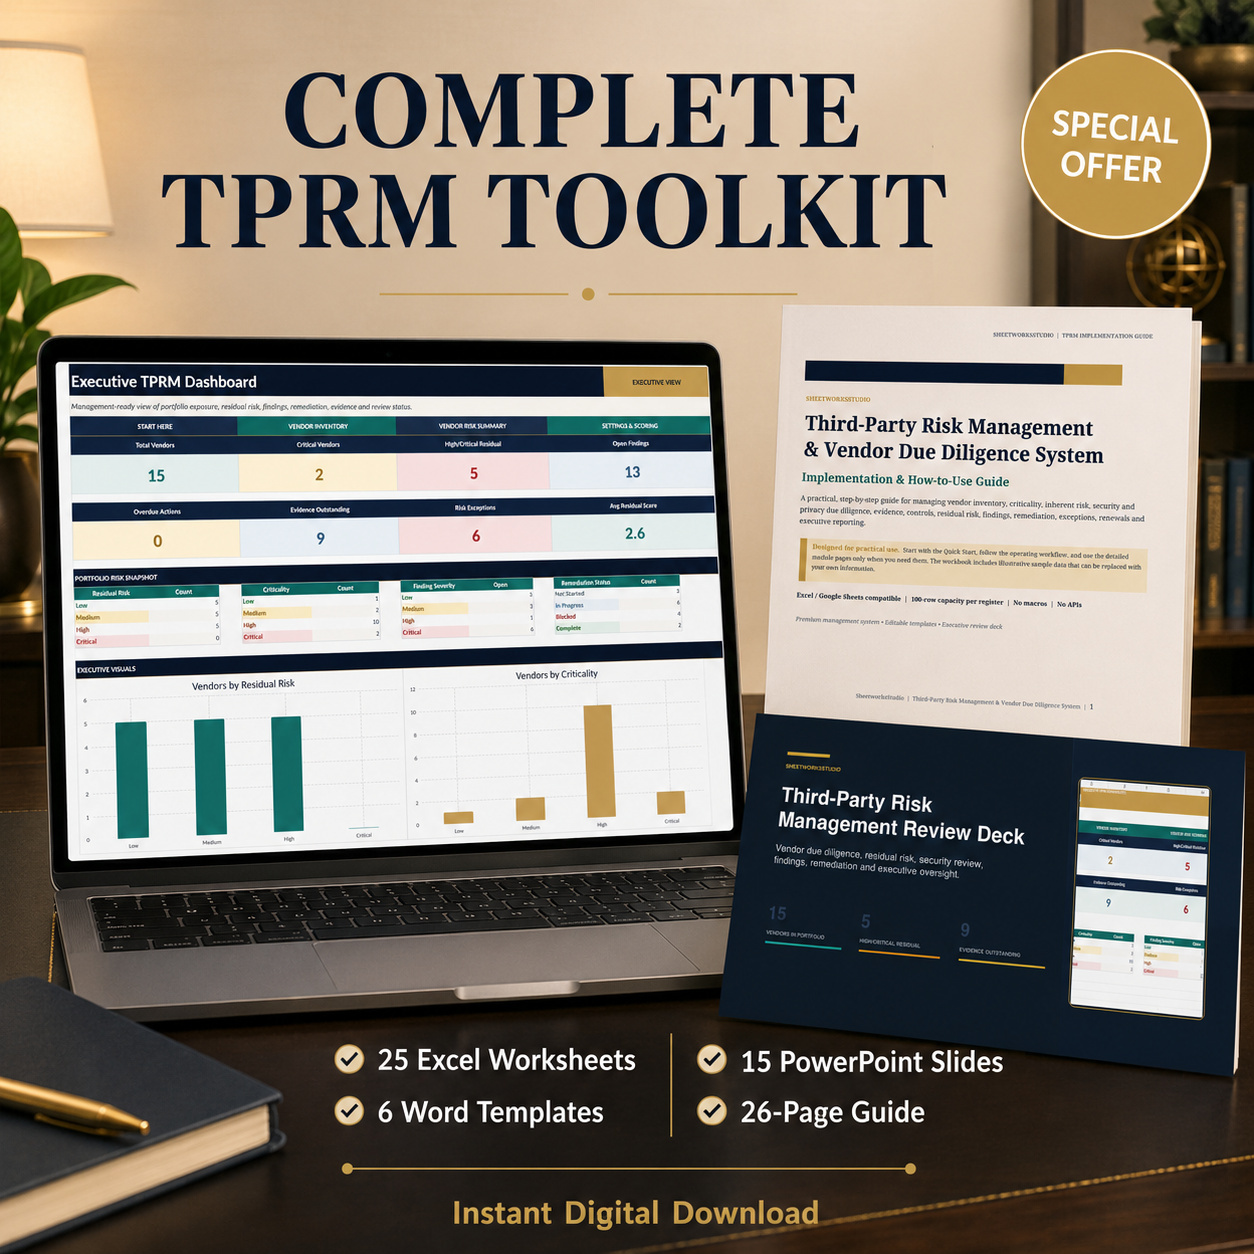
Complete TPRM toolkit with 25-sheet Excel system, 6 Word templates, 15-slide management deck and 26-page implementation guide.
Further information
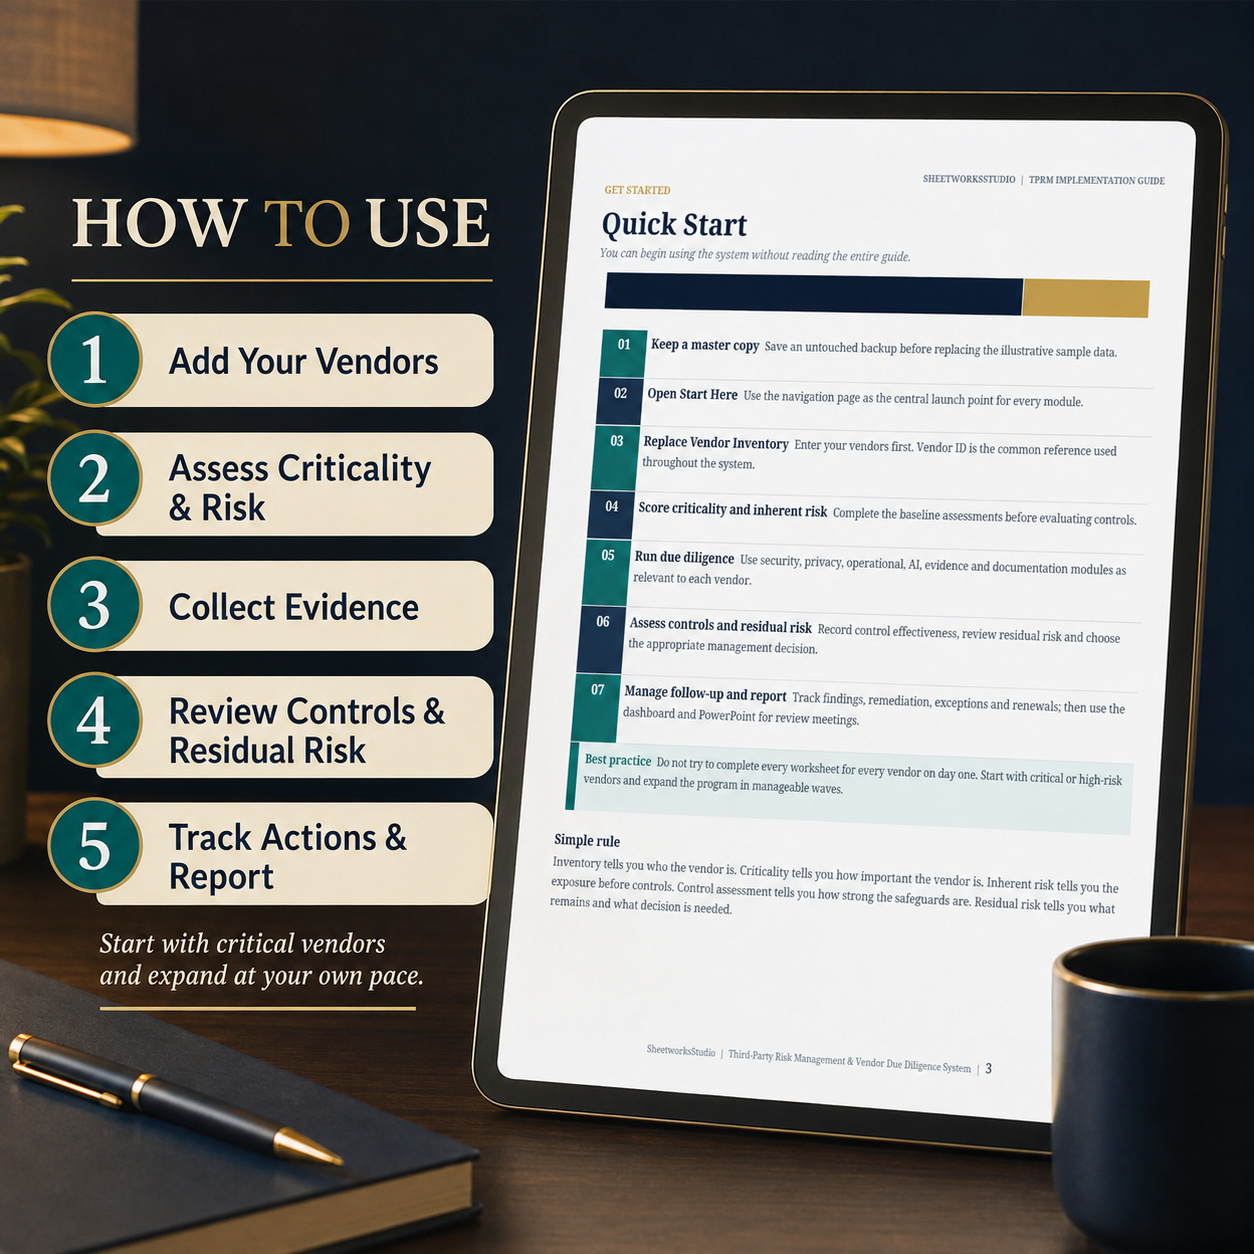
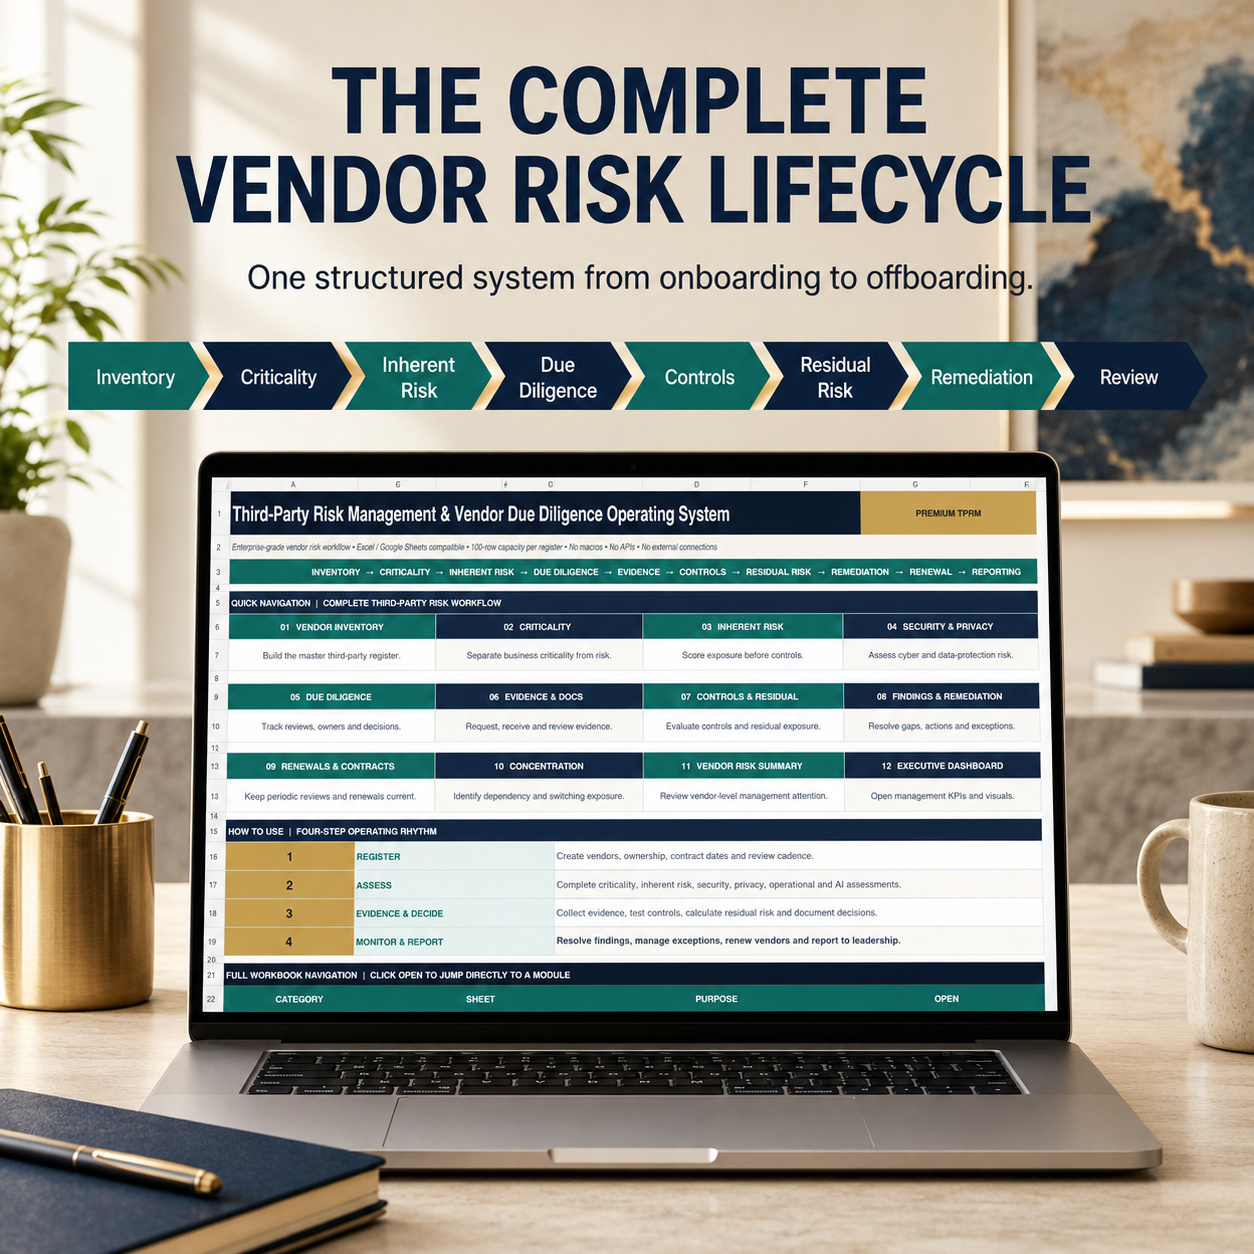
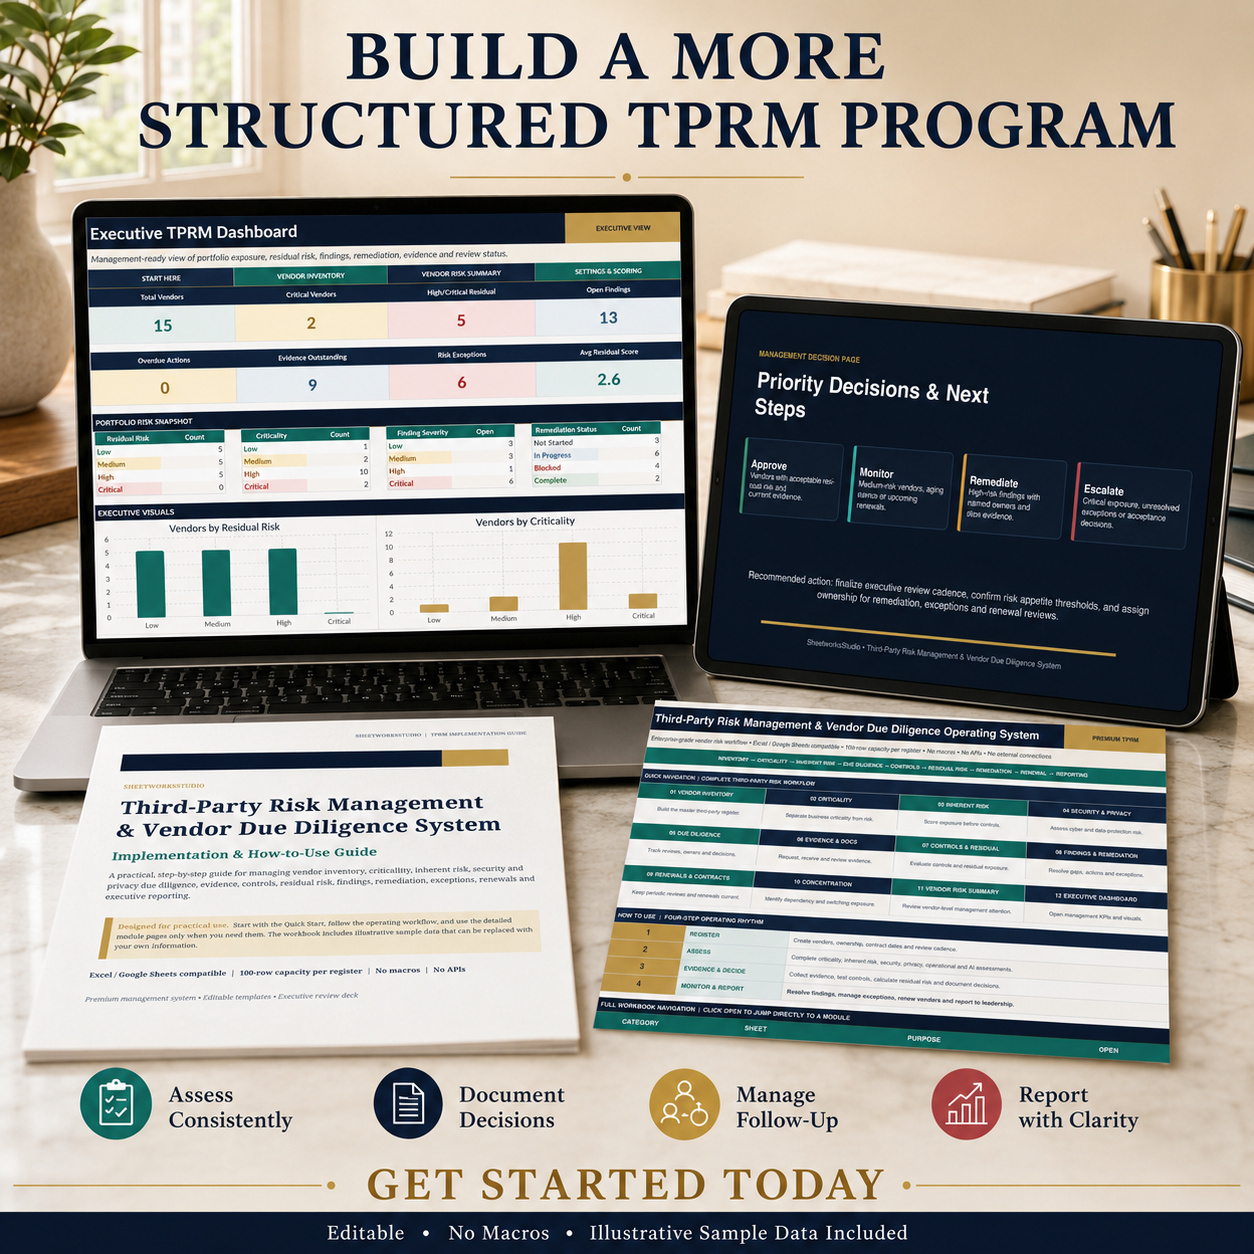
• Establish a structured end-to-end Third-Party Risk Management process
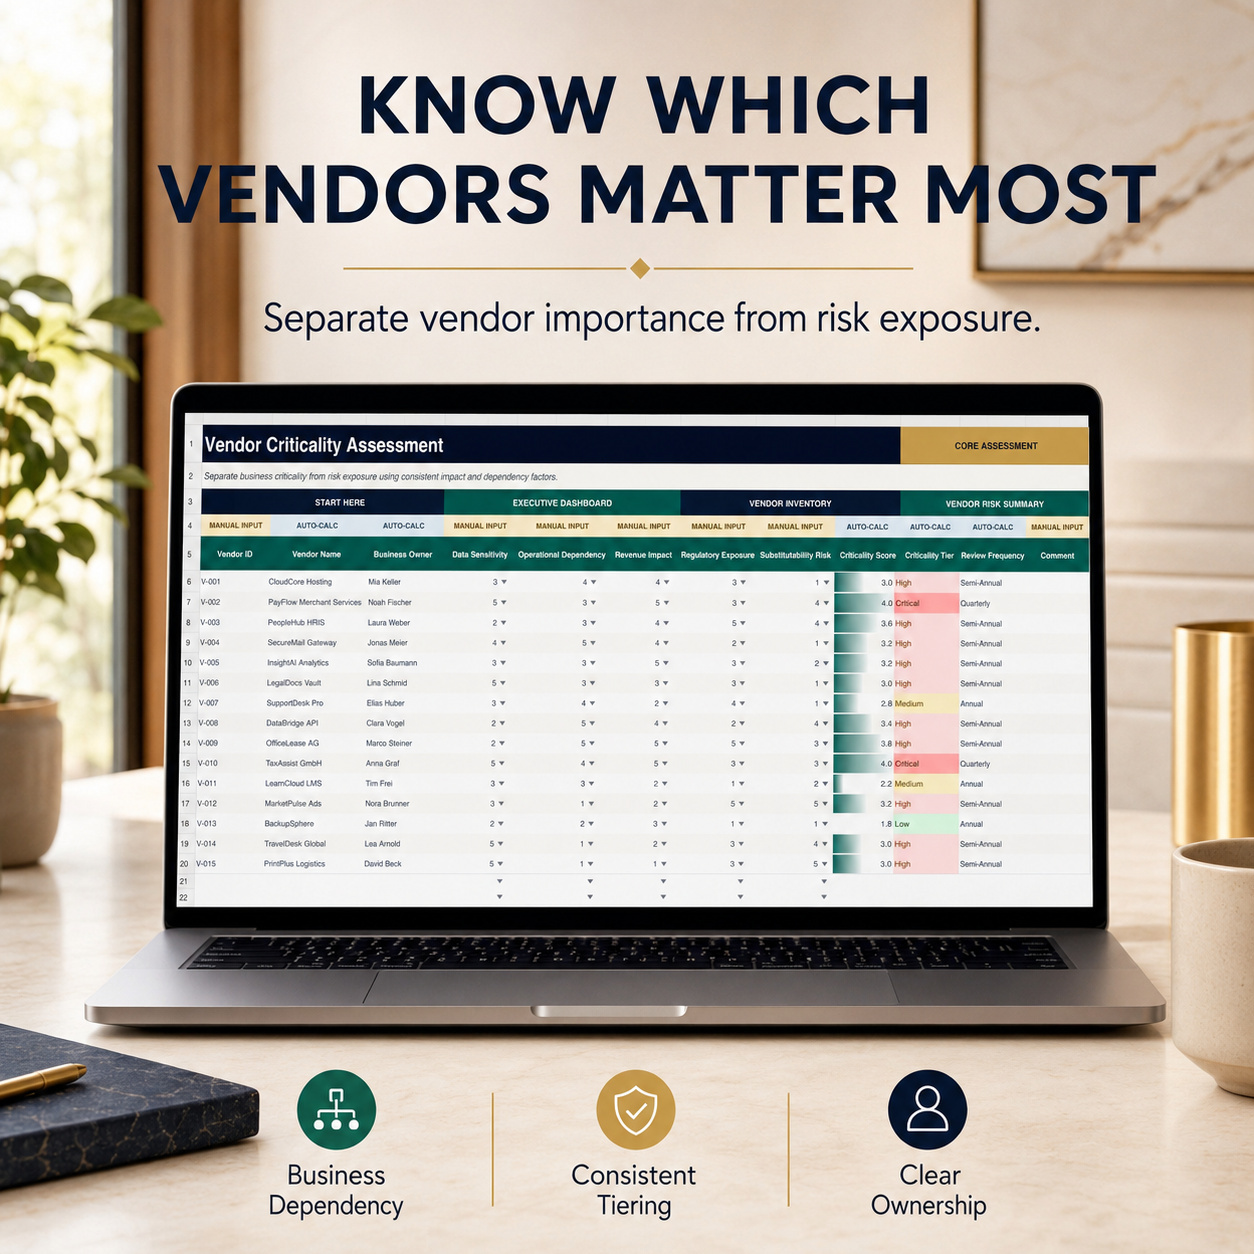
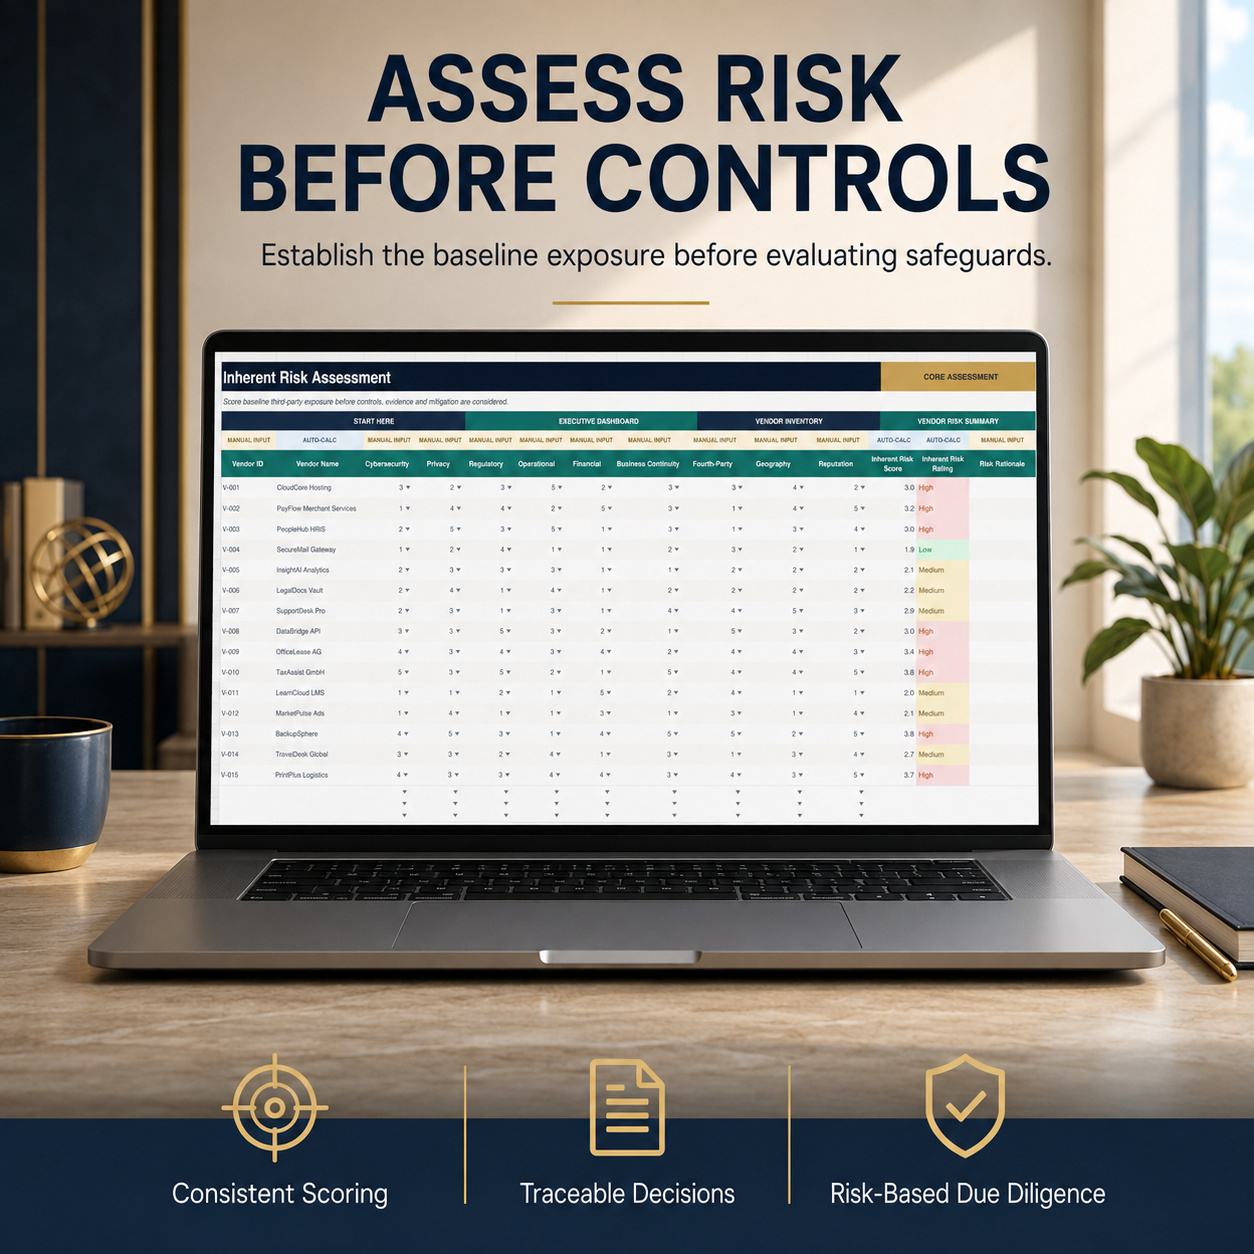
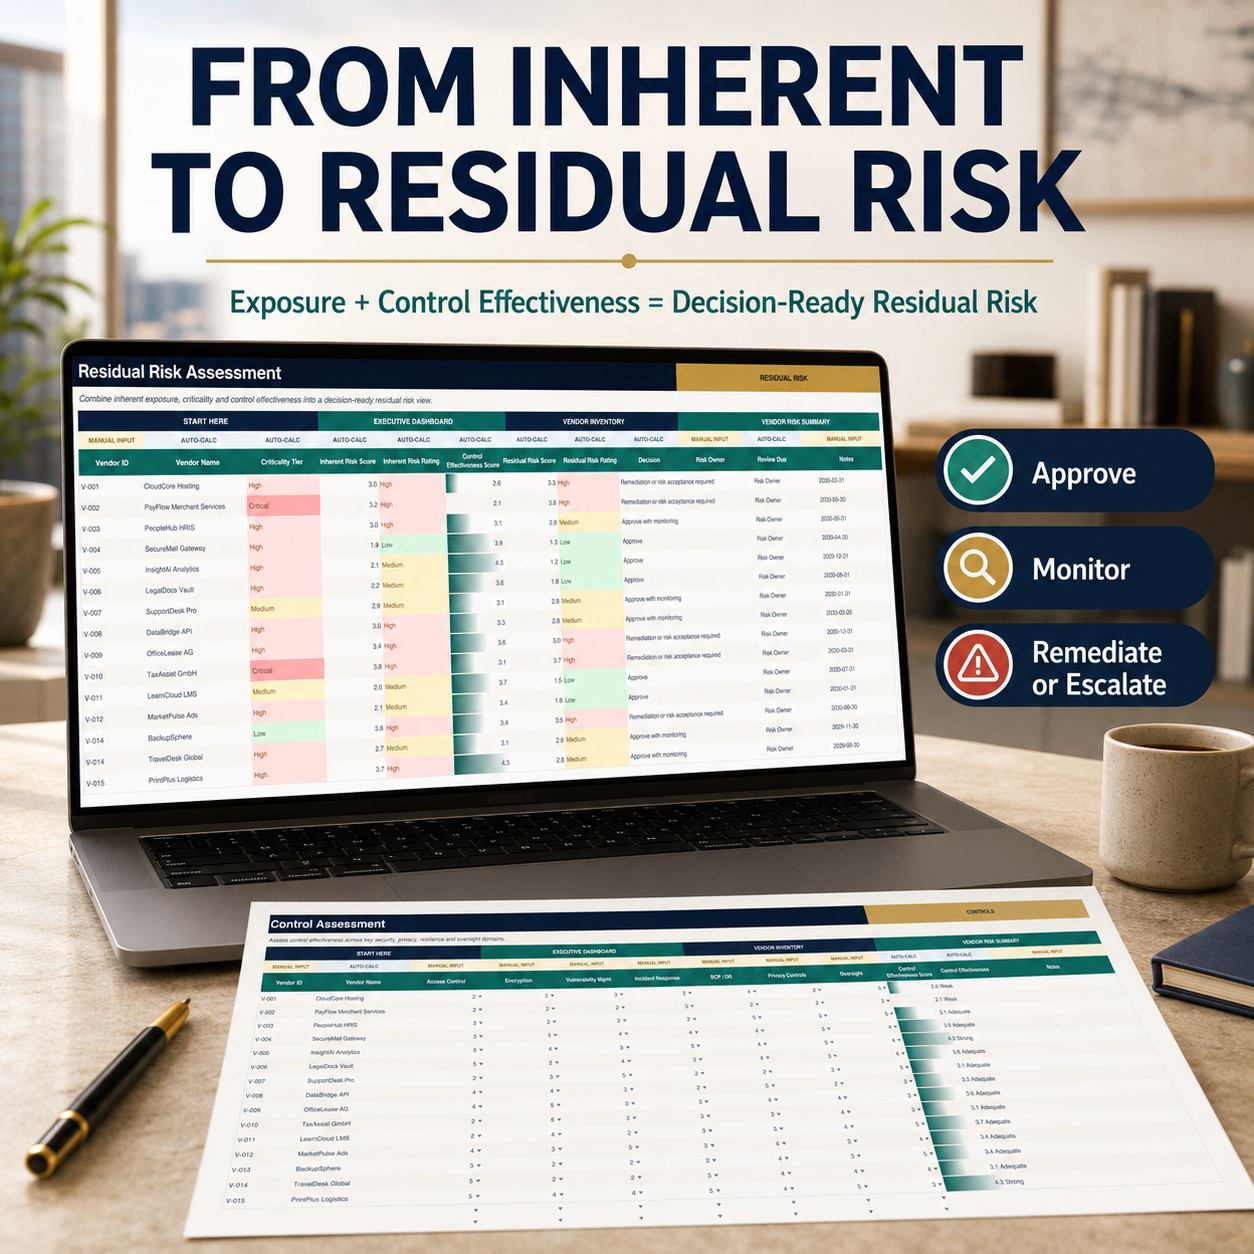
• Assess vendor criticality, inherent risk, controls and residual risk separately
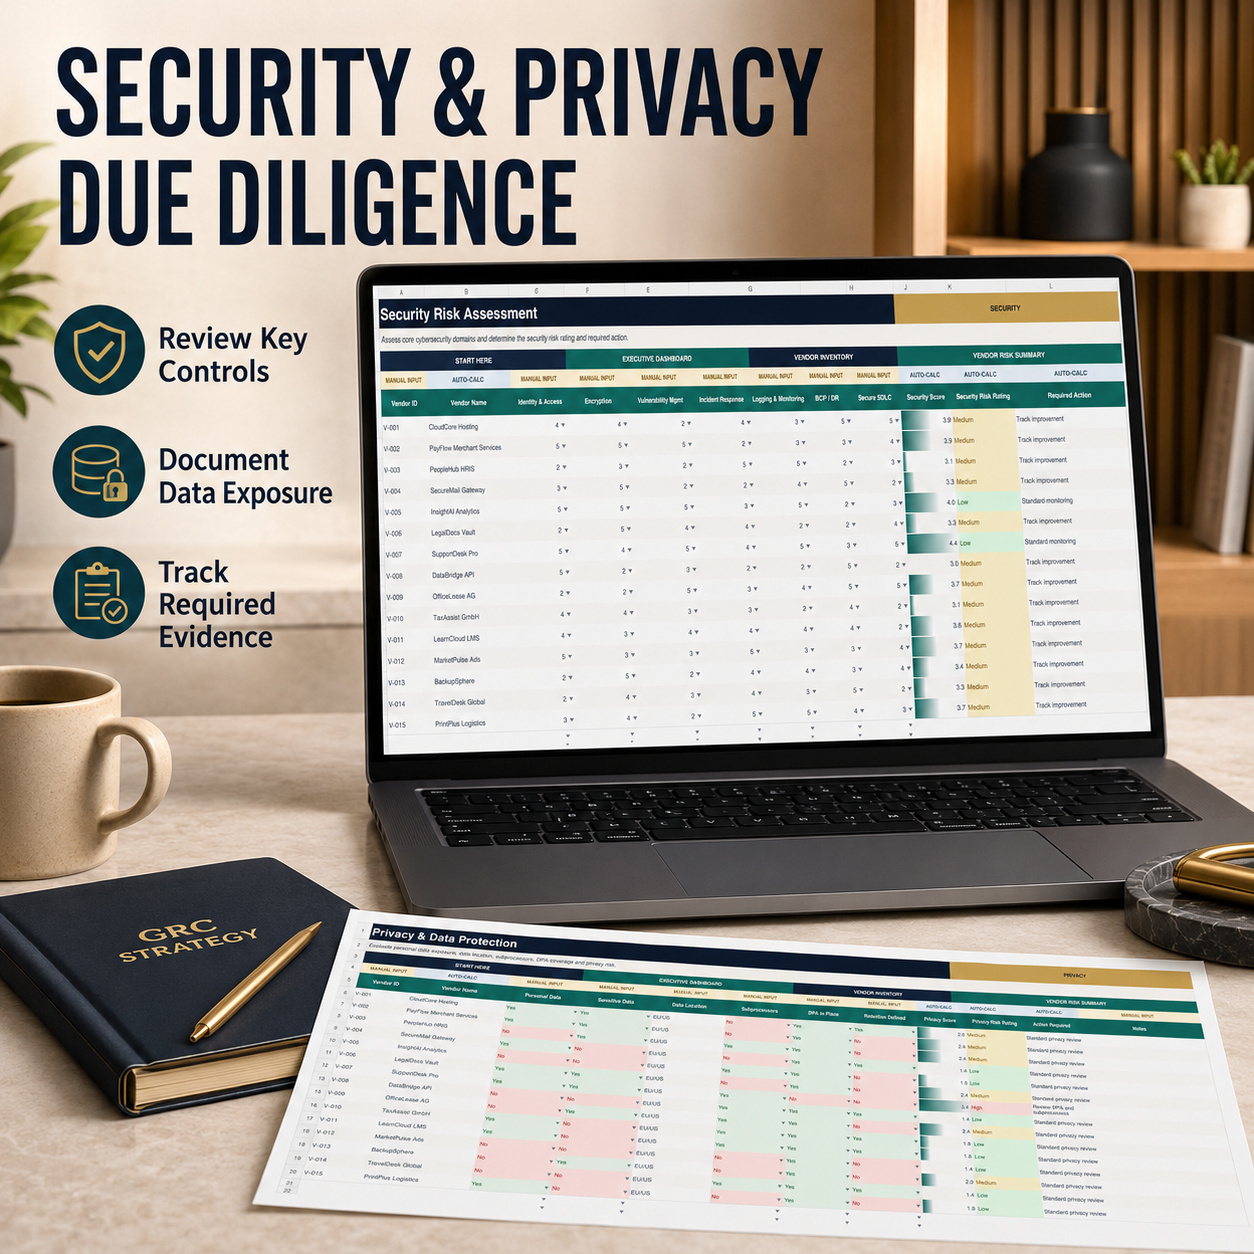
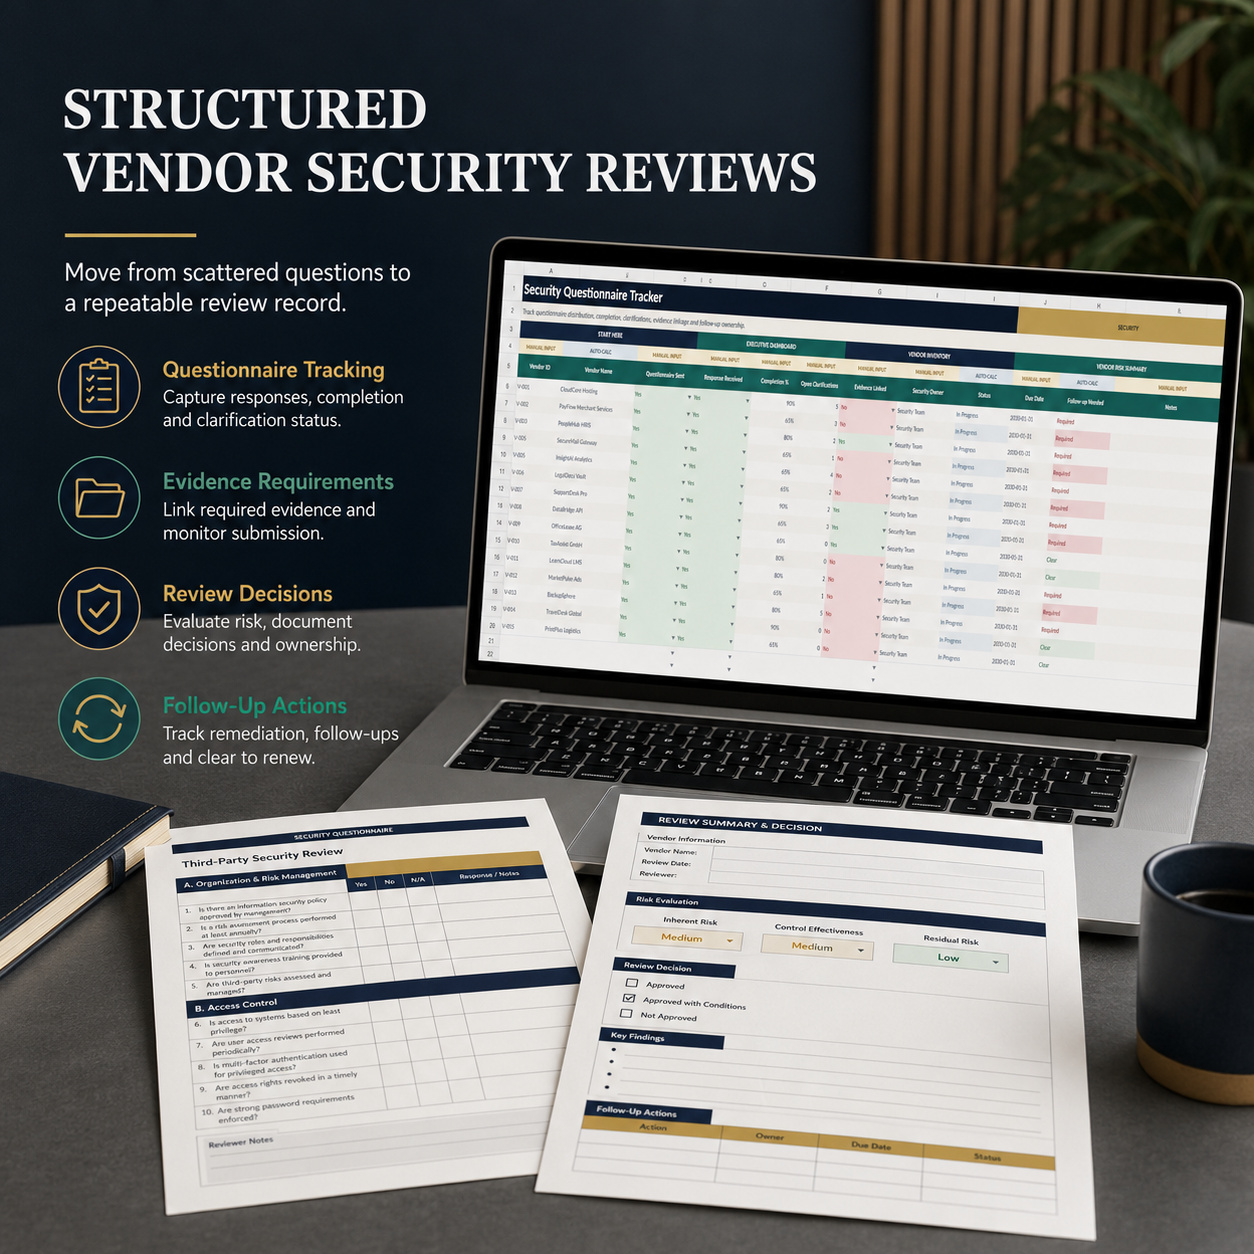
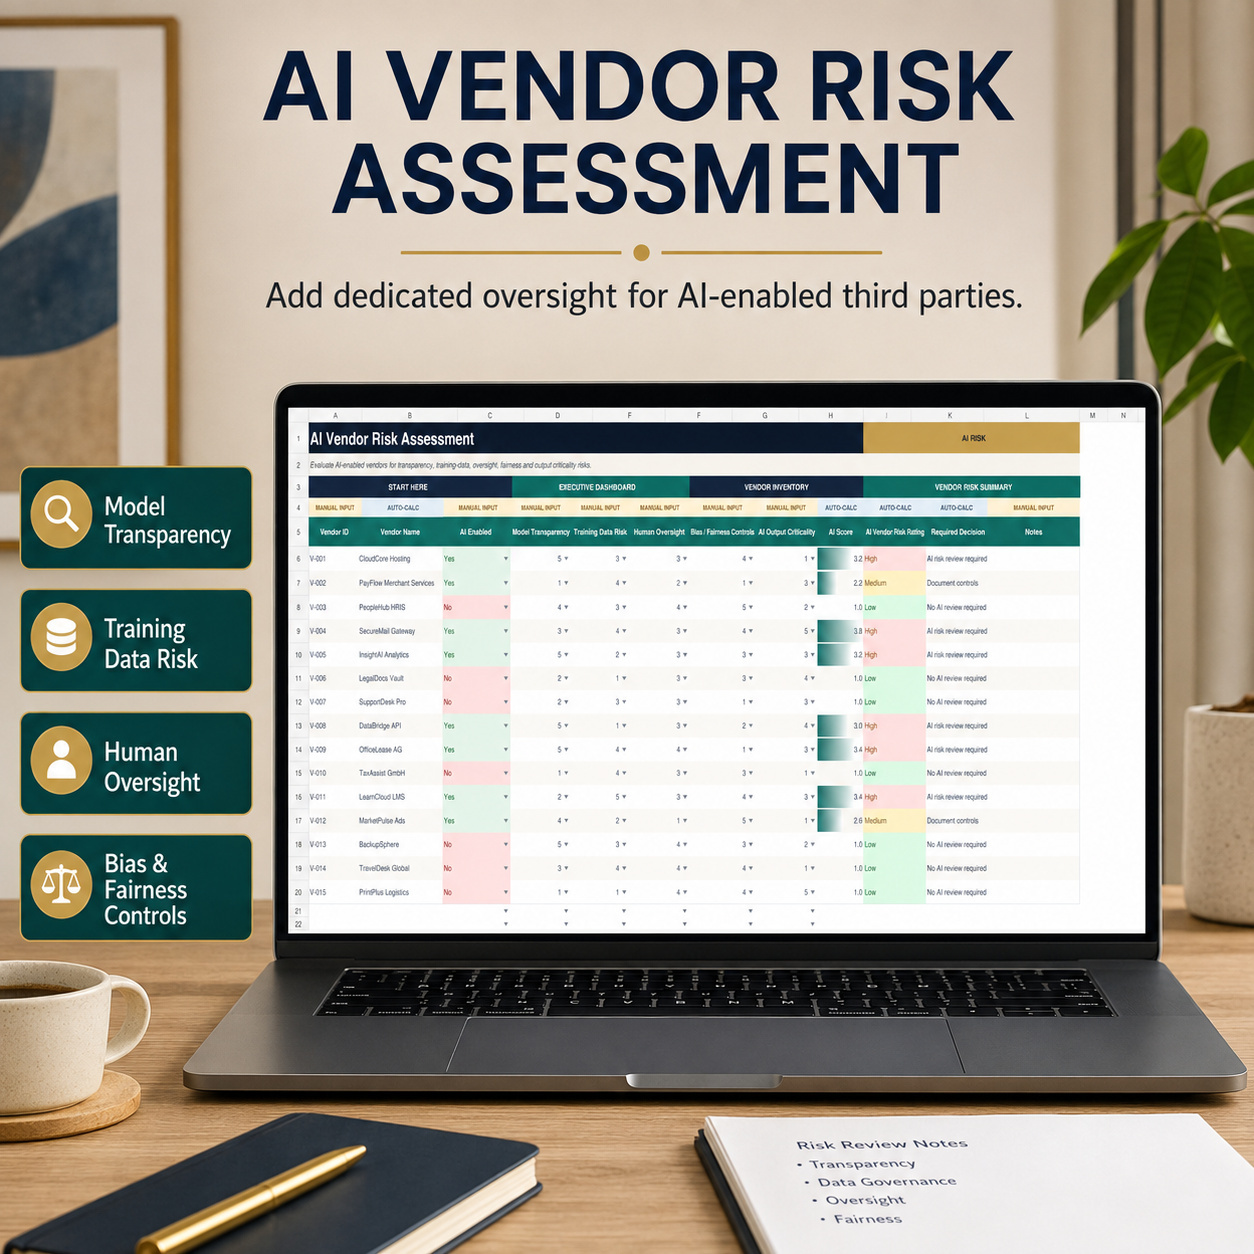
• Standardize vendor security, privacy, AI and operational due diligence
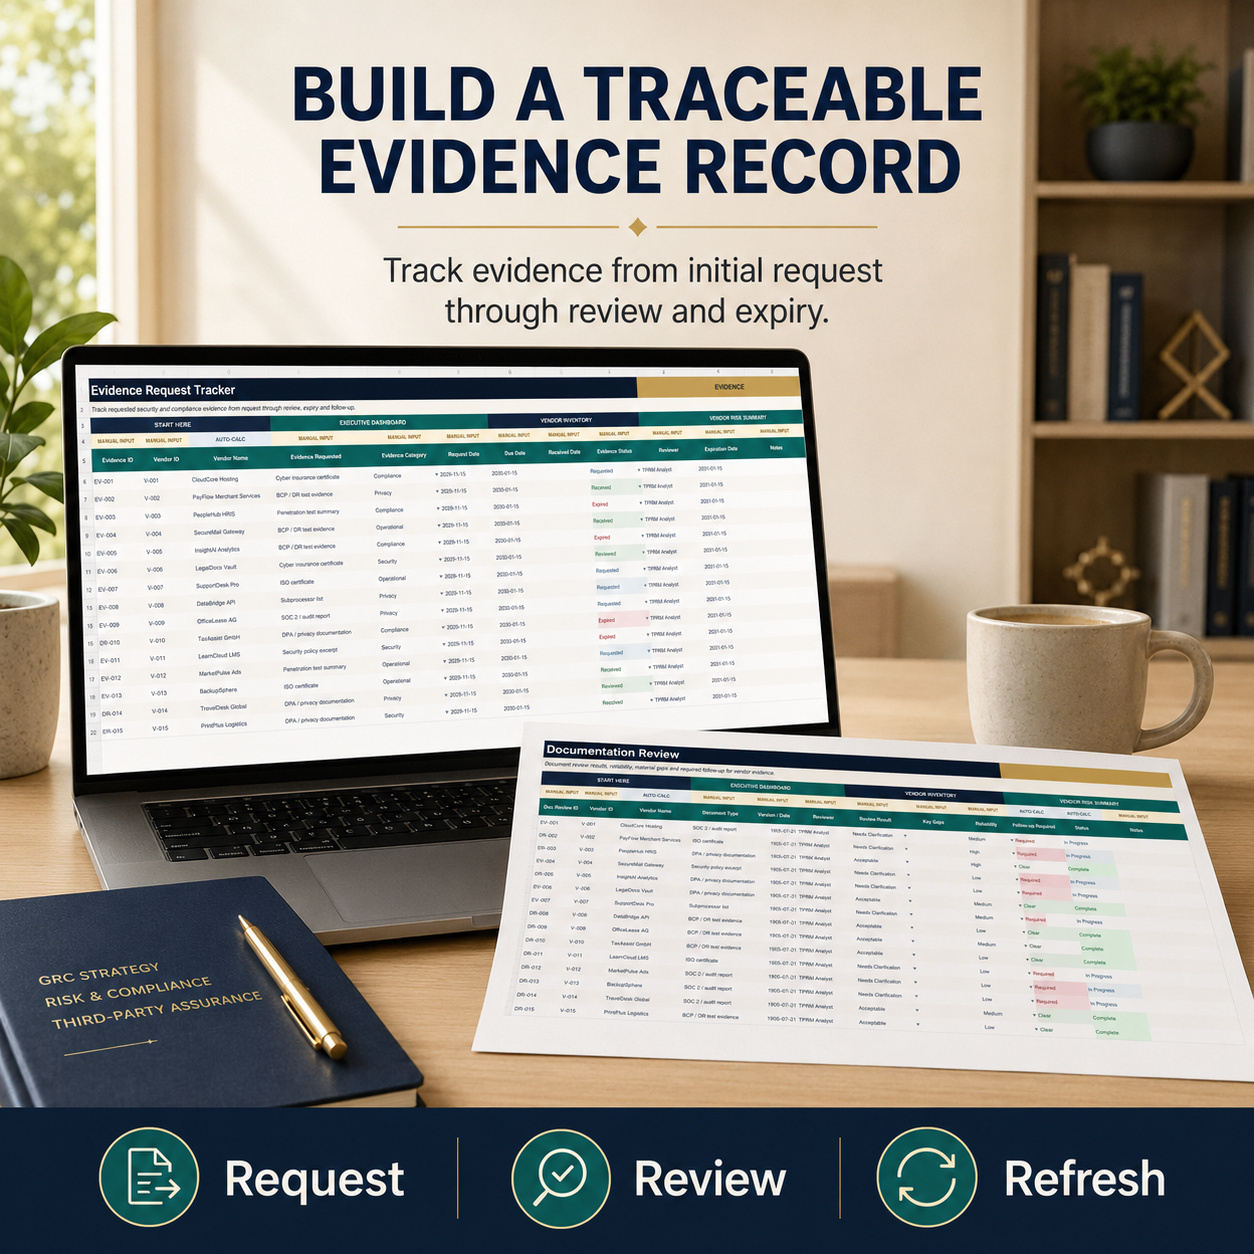
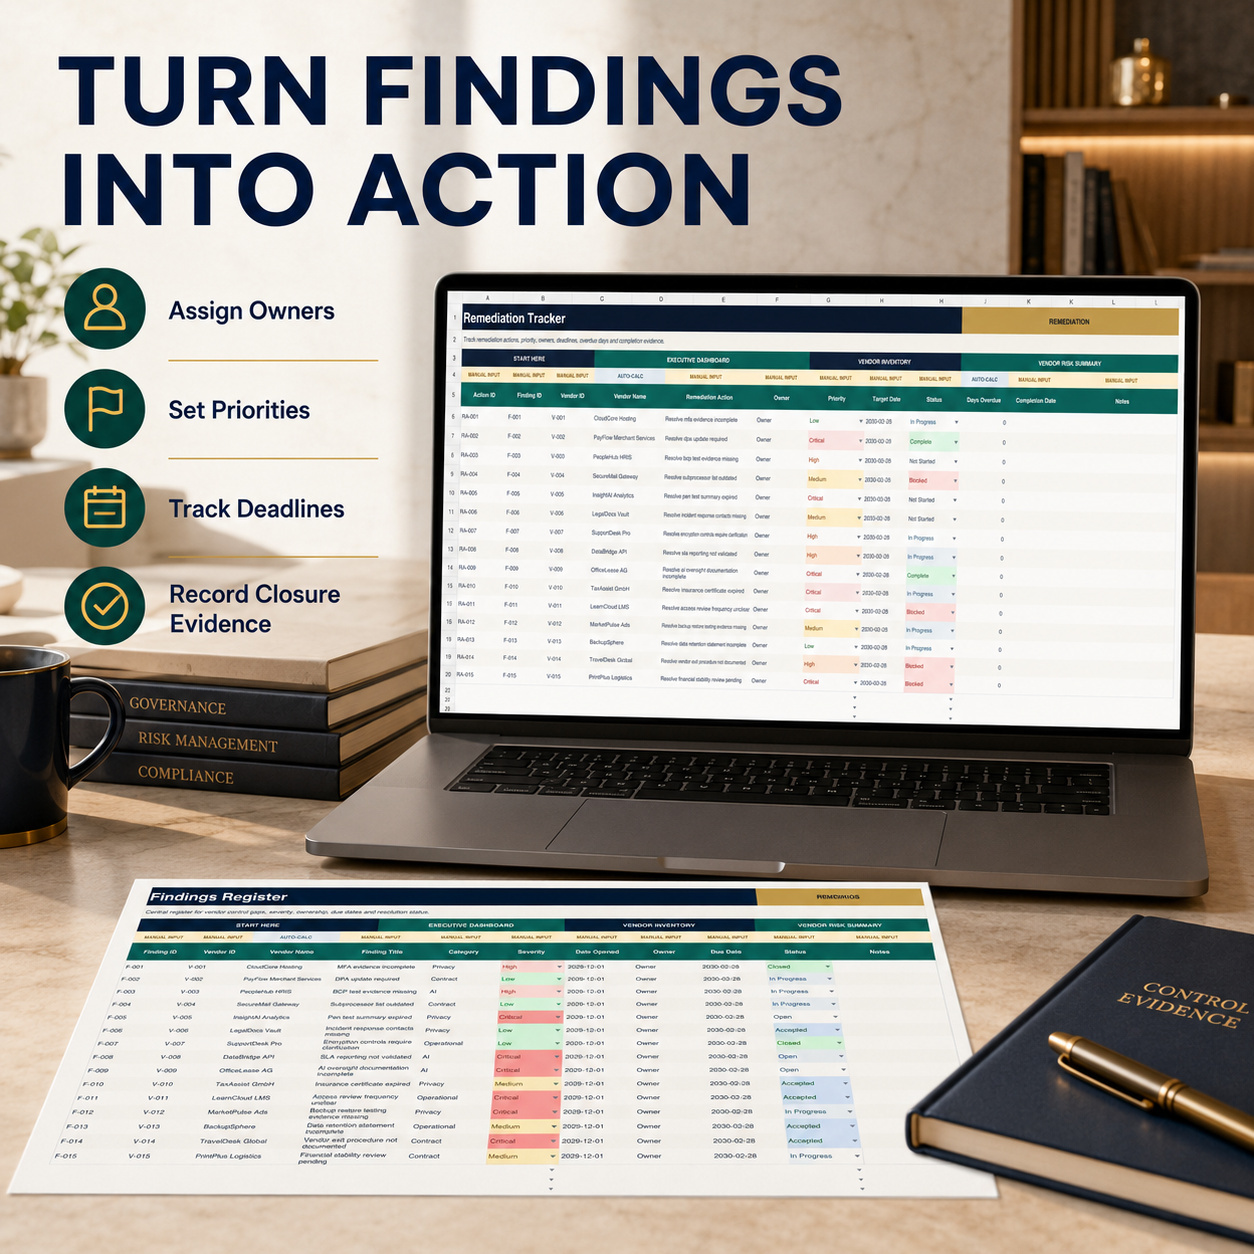
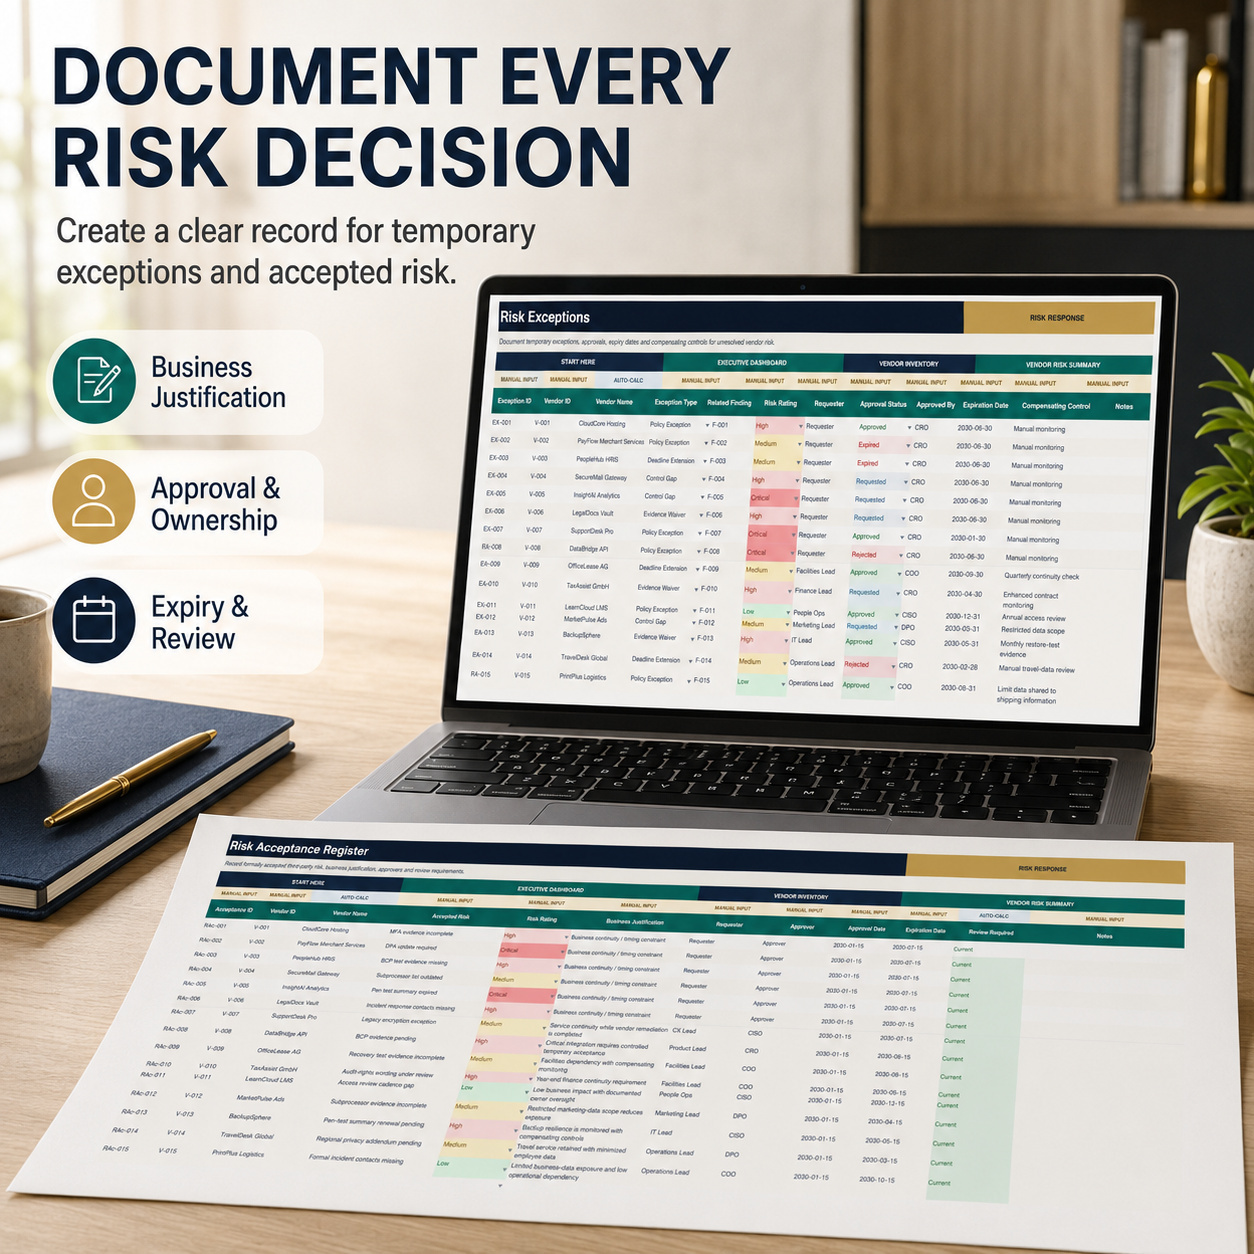
• Maintain traceable evidence, findings, remediation and risk acceptance records
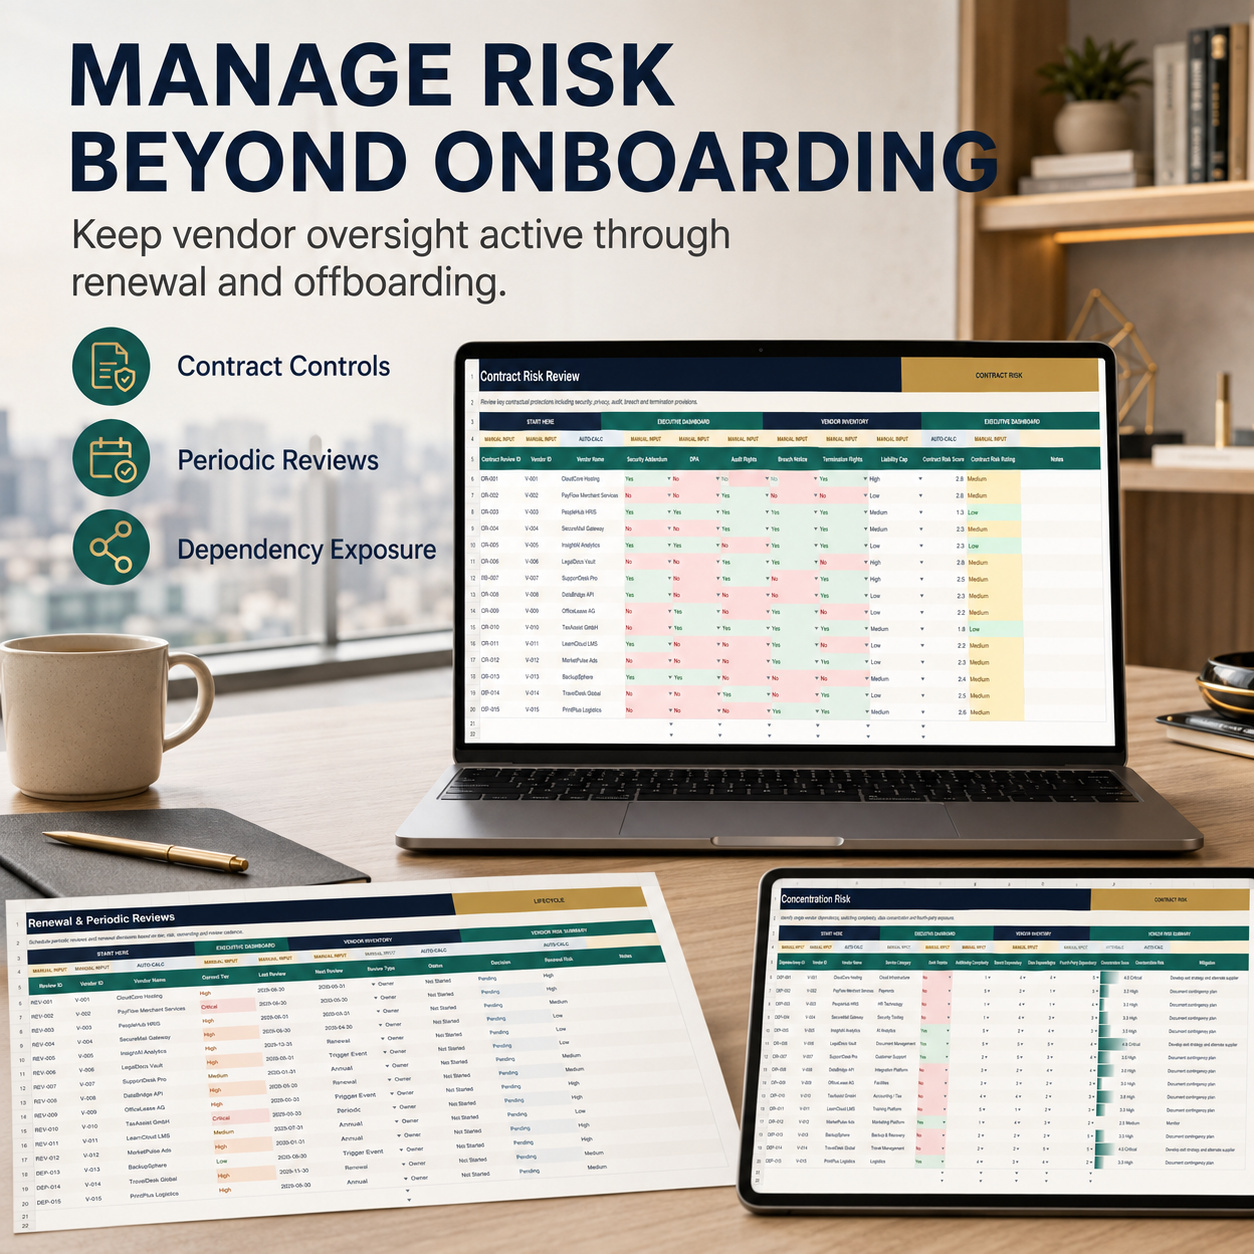
• Improve recurring vendor reviews and renewal decisions
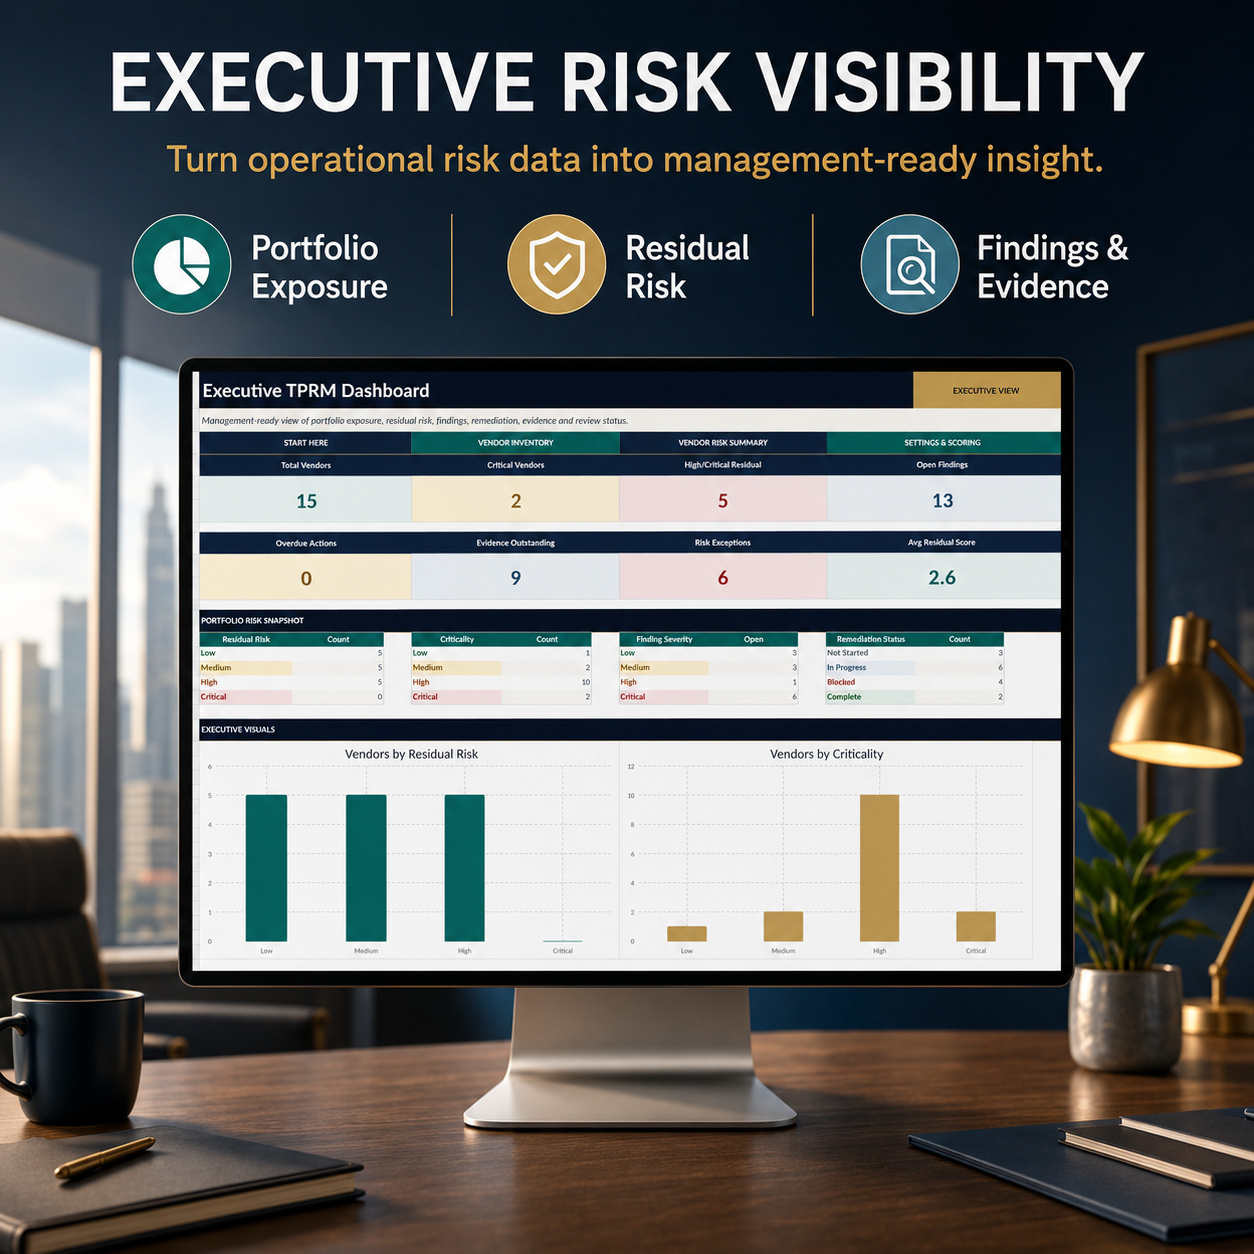
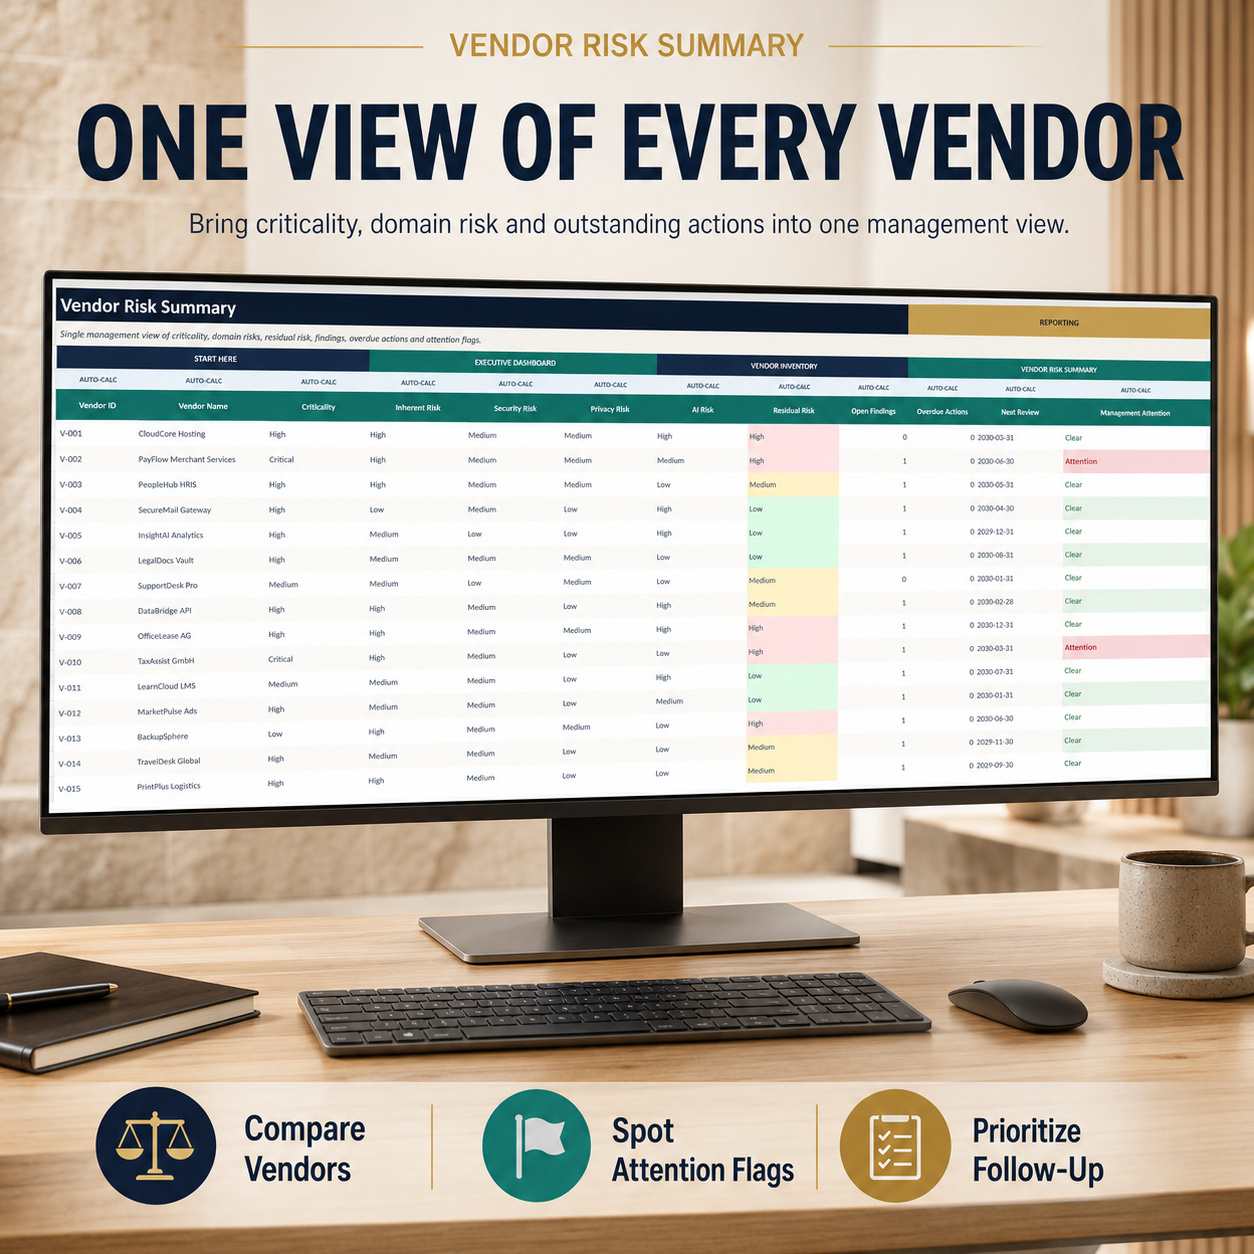
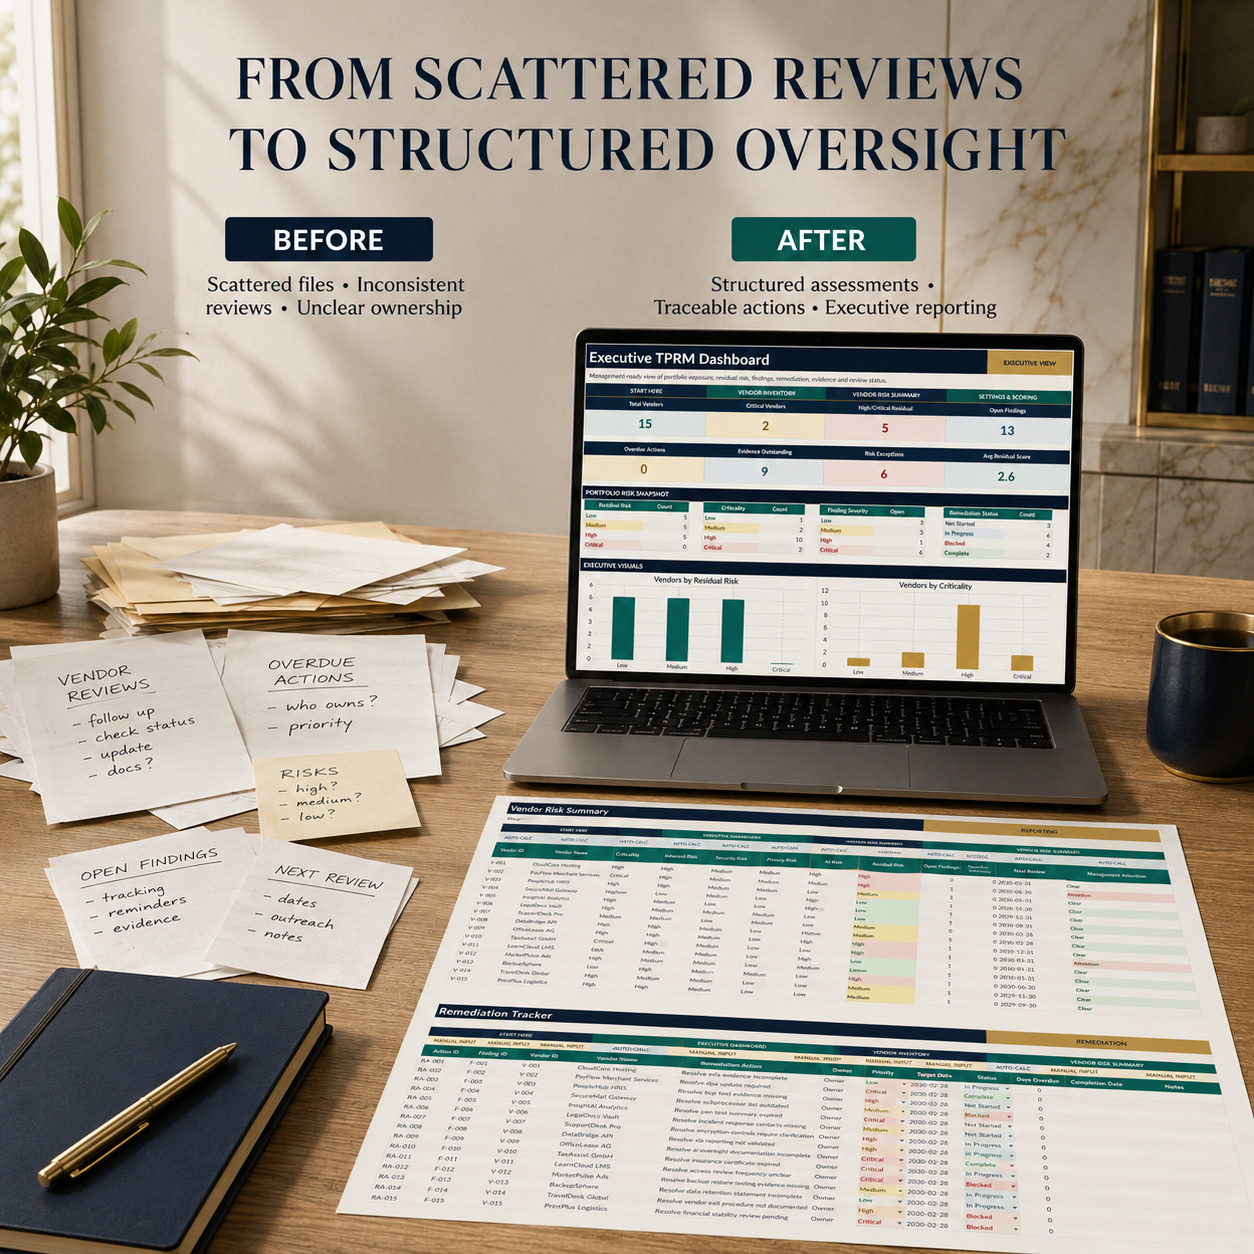
• Create clear executive-level TPRM reporting and management visibility
Best suited for organizations that:
• Manage multiple suppliers, vendors, SaaS providers or other third parties
• Need a structured but practical TPRM operating model
• Want to centralize vendor assessments, due diligence and evidence
• Require security, privacy, AI, financial and operational risk reviews
• Need documented findings, remediation, exceptions and risk acceptance
• Want management-ready reporting without implementing specialist GRC software
• Prefer editable Microsoft Office templates that can be adapted internally
This toolkit is not intended to:
• Replace dedicated enterprise GRC or continuous-monitoring platforms
• Provide automated API integrations or live external vendor intelligence
• Guarantee regulatory compliance, audit results or certification
• Replace organization-specific legal, regulatory or cybersecurity advice
• Serve as a fully automated vendor onboarding platform