NIS2 Readiness & Evidence Tracker | Excel Compliance Dashboard

NIS2 readiness toolkit with gap assessment, evidence library, actions, supplier risk, asset register, dashboard and 15-question Pulse Check.

Description
๐Ÿ›ก๏ธ NIS2 READINESS & EVIDENCE TRACKER OS


Bring greater structure, visibility and accountability to internal NIS2 readiness work with a professional Excel-based management system.


Designed for GRC, cybersecurity, IT, risk, audit and compliance teams, the toolkit connects controls, maturity assessments, remediation actions, evidence, incidents, supplier risk and critical assets within one coordinated workflow.


Instead of maintaining disconnected spreadsheets and evidence lists, teams can work from a structured readiness system with automated calculations, validated inputs, visual indicators and executive reporting.


IDEAL FOR
๐Ÿ›ก๏ธ GRC & Compliance Teams
๐Ÿ” Information Security Teams
๐Ÿ’ป IT & Security Leadership
๐Ÿ‘ค CISOs
โš ๏ธ Risk Management Teams
๐Ÿค Supplier & Third-Party Risk Owners
๐Ÿ“‹ Internal Audit
๐Ÿ—‚๏ธ Evidence Owners
๐Ÿ’ผ Cybersecurity & GRC Consultants
๐Ÿข Organizations structuring internal NIS2 readiness


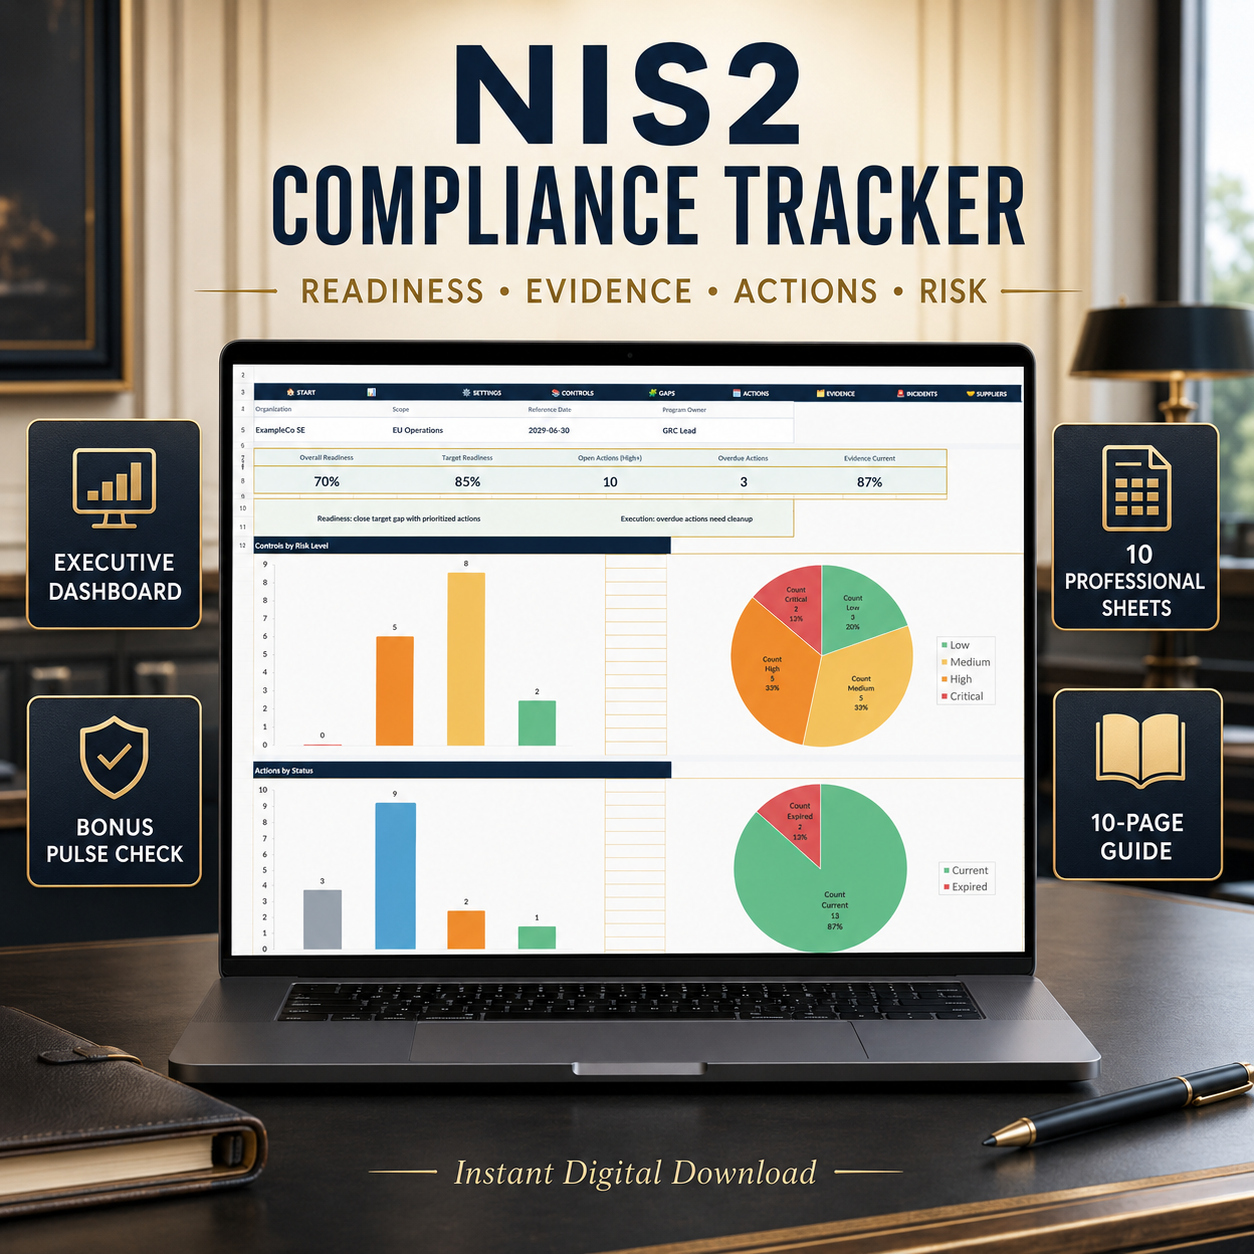
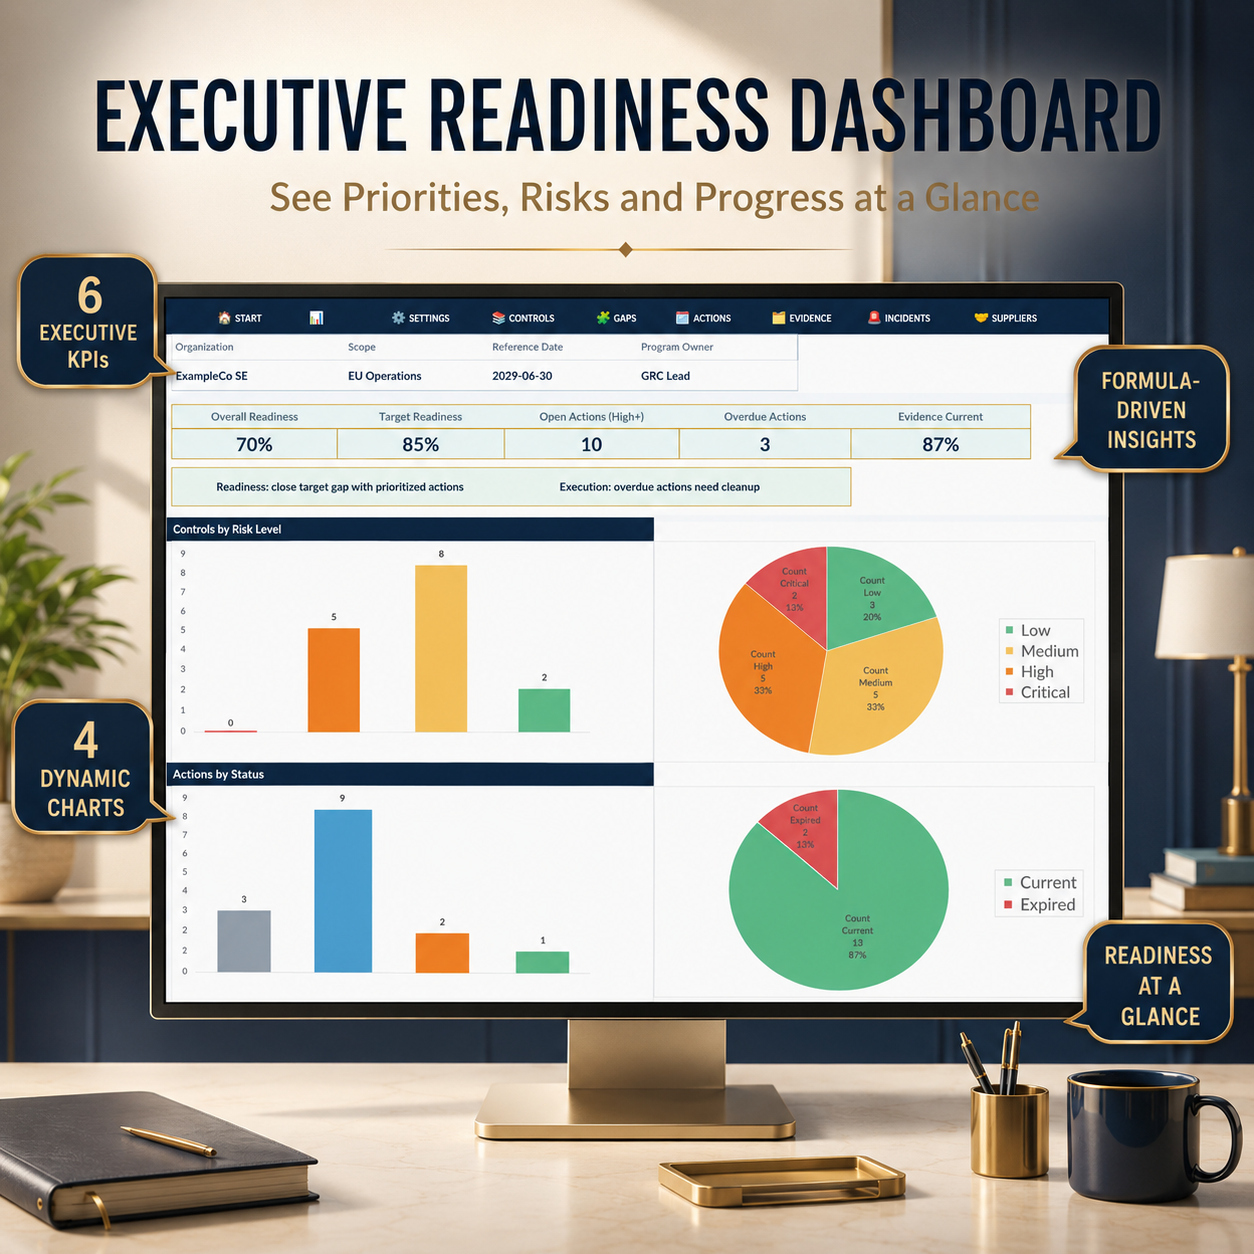
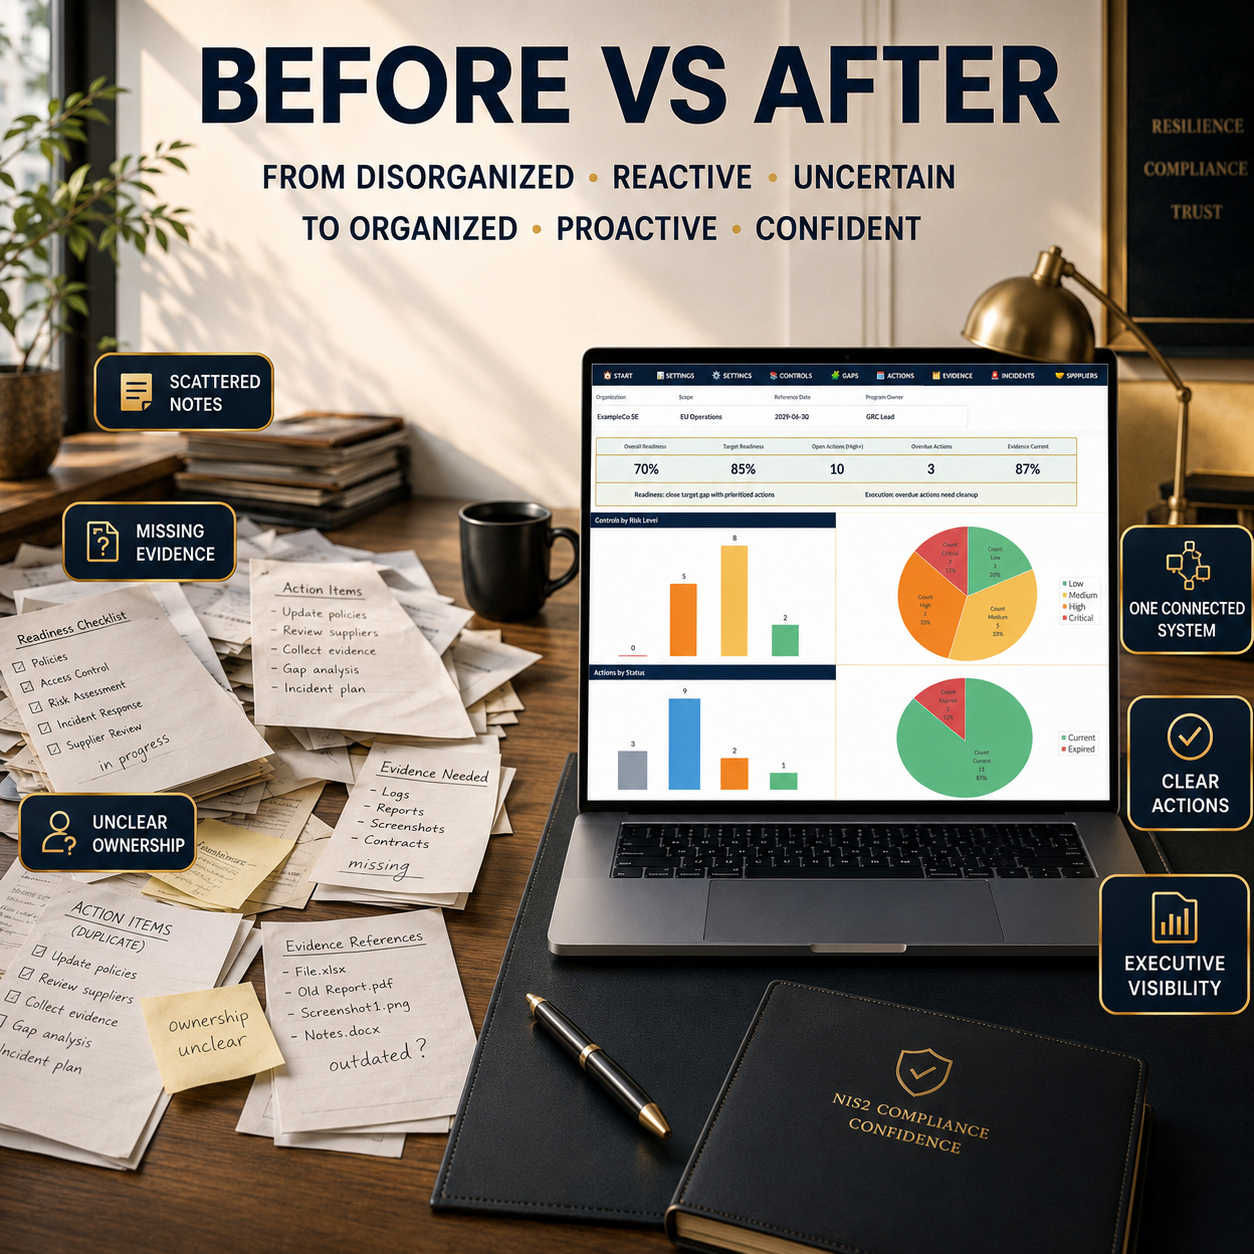
๐Ÿ“Š EXECUTIVE READINESS DASHBOARD
The formula-driven Dashboard provides 6 management KPIs:
โœ… Overall Readiness
๐ŸŽฏ Target Readiness
โš ๏ธ Open High & Critical Actions
โฐ Overdue Actions
๐Ÿ—‚๏ธ Evidence Current
๐Ÿค High-Risk Suppliers


Four dynamic charts provide additional management visibility:
๐Ÿ“Š Controls by Risk Level
๐Ÿšจ Incidents by Severity
๐Ÿ—“๏ธ Actions by Status
๐Ÿ—‚๏ธ Evidence Current vs Expired


The Dashboard updates from the operational tracker sheets and supports recurring management and stakeholder reviews.


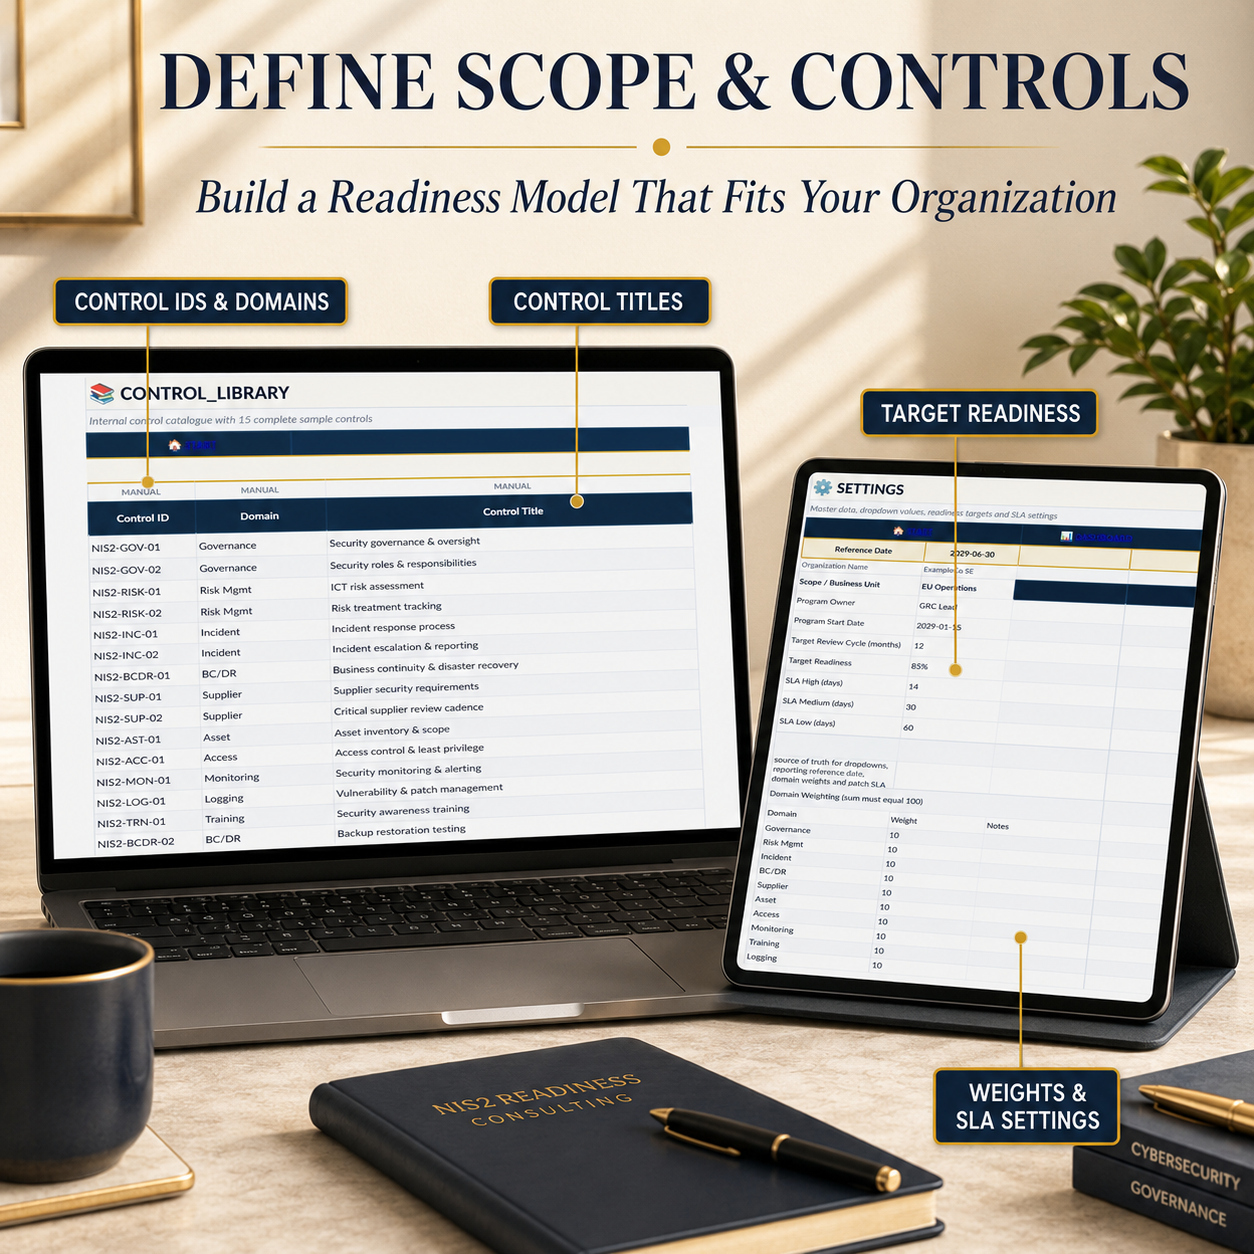
๐Ÿ“š CONTROL LIBRARY
Maintain a structured internal control catalogue with:
โ€ข Control ID
โ€ข Domain
โ€ข Control Title
โ€ข Control Objective
โ€ข Responsible Role
โ€ข Target Maturity
โ€ข Evidence Requirement
โ€ข Suggested Evidence Types
โ€ข Weighting


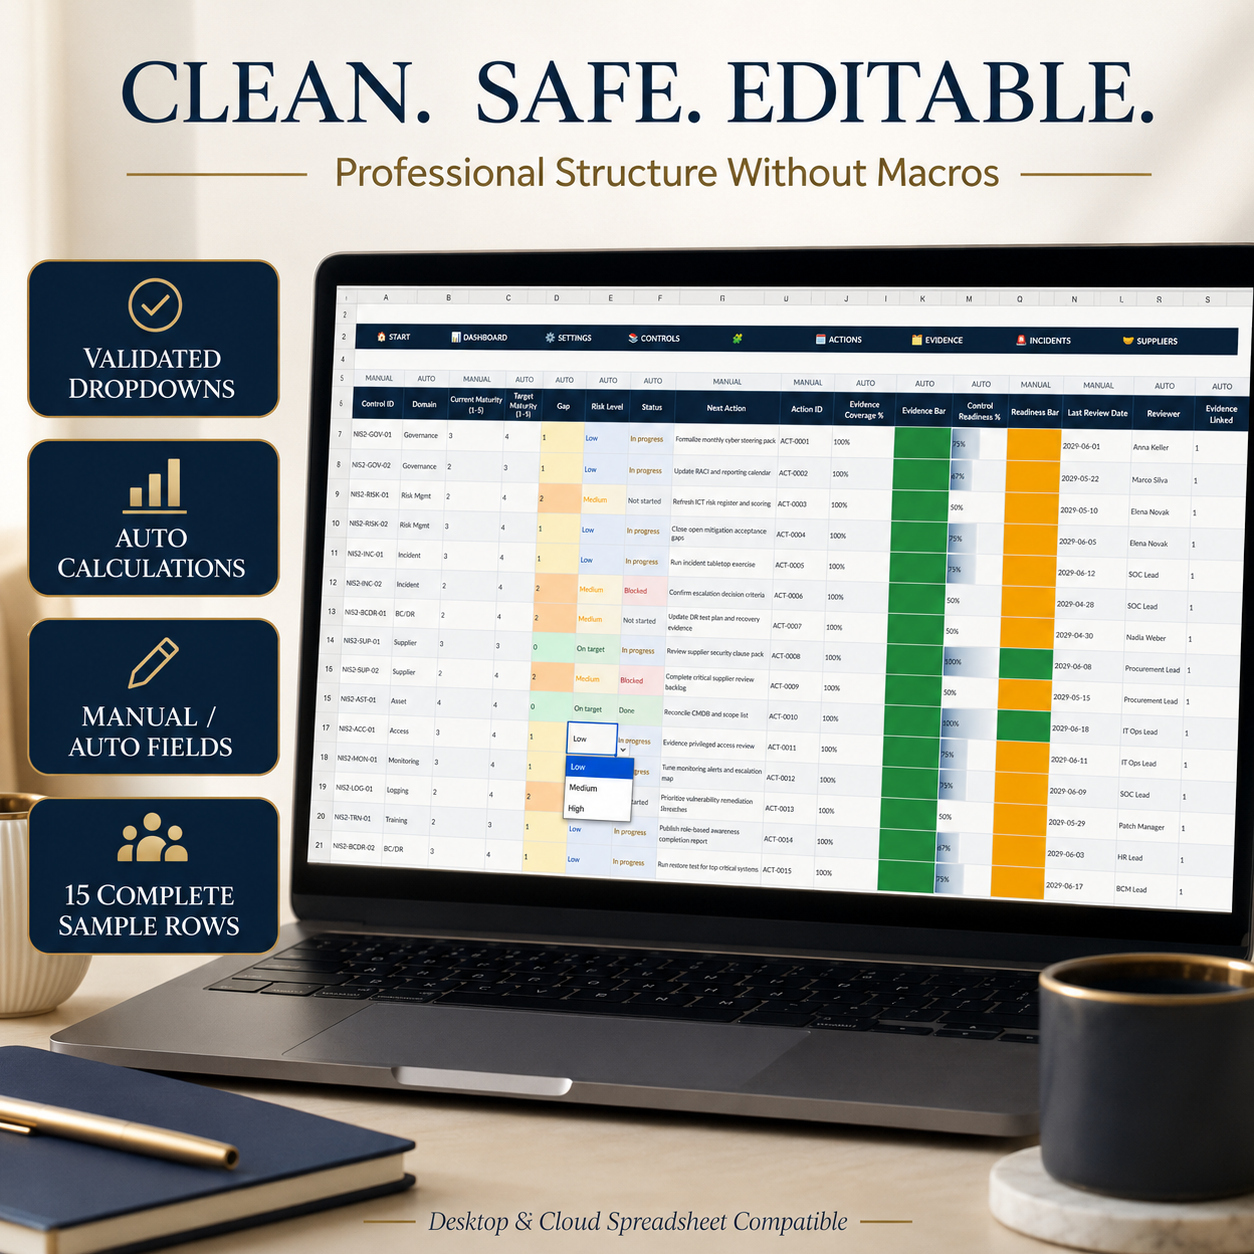
The included demonstration library contains 15 complete sample controls across key readiness areas.


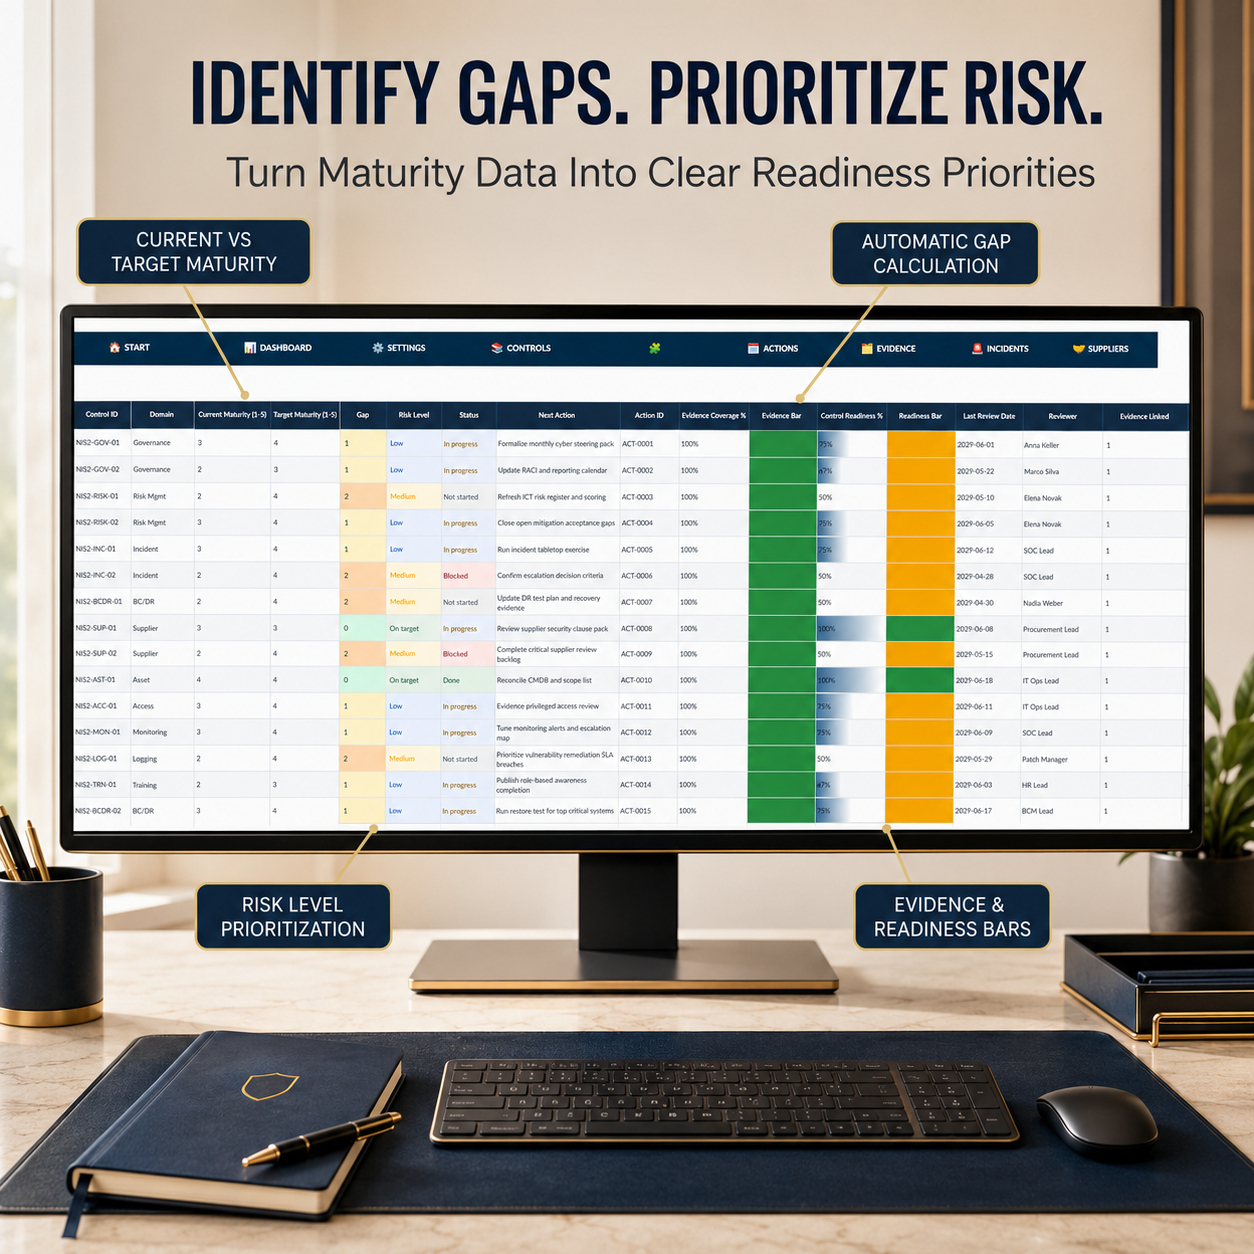
๐Ÿงฉ GAP & MATURITY ASSESSMENT
Compare current maturity against target maturity using validated 1โ€“5 maturity scores.
Automatic calculations provide:
โœ… Maturity Gap
โœ… Risk Level
โœ… Evidence Coverage %
โœ… Control Readiness %
โœ… Visual Progress Indicators


The assessment links controls, actions and evidence through consistent IDs for improved traceability.


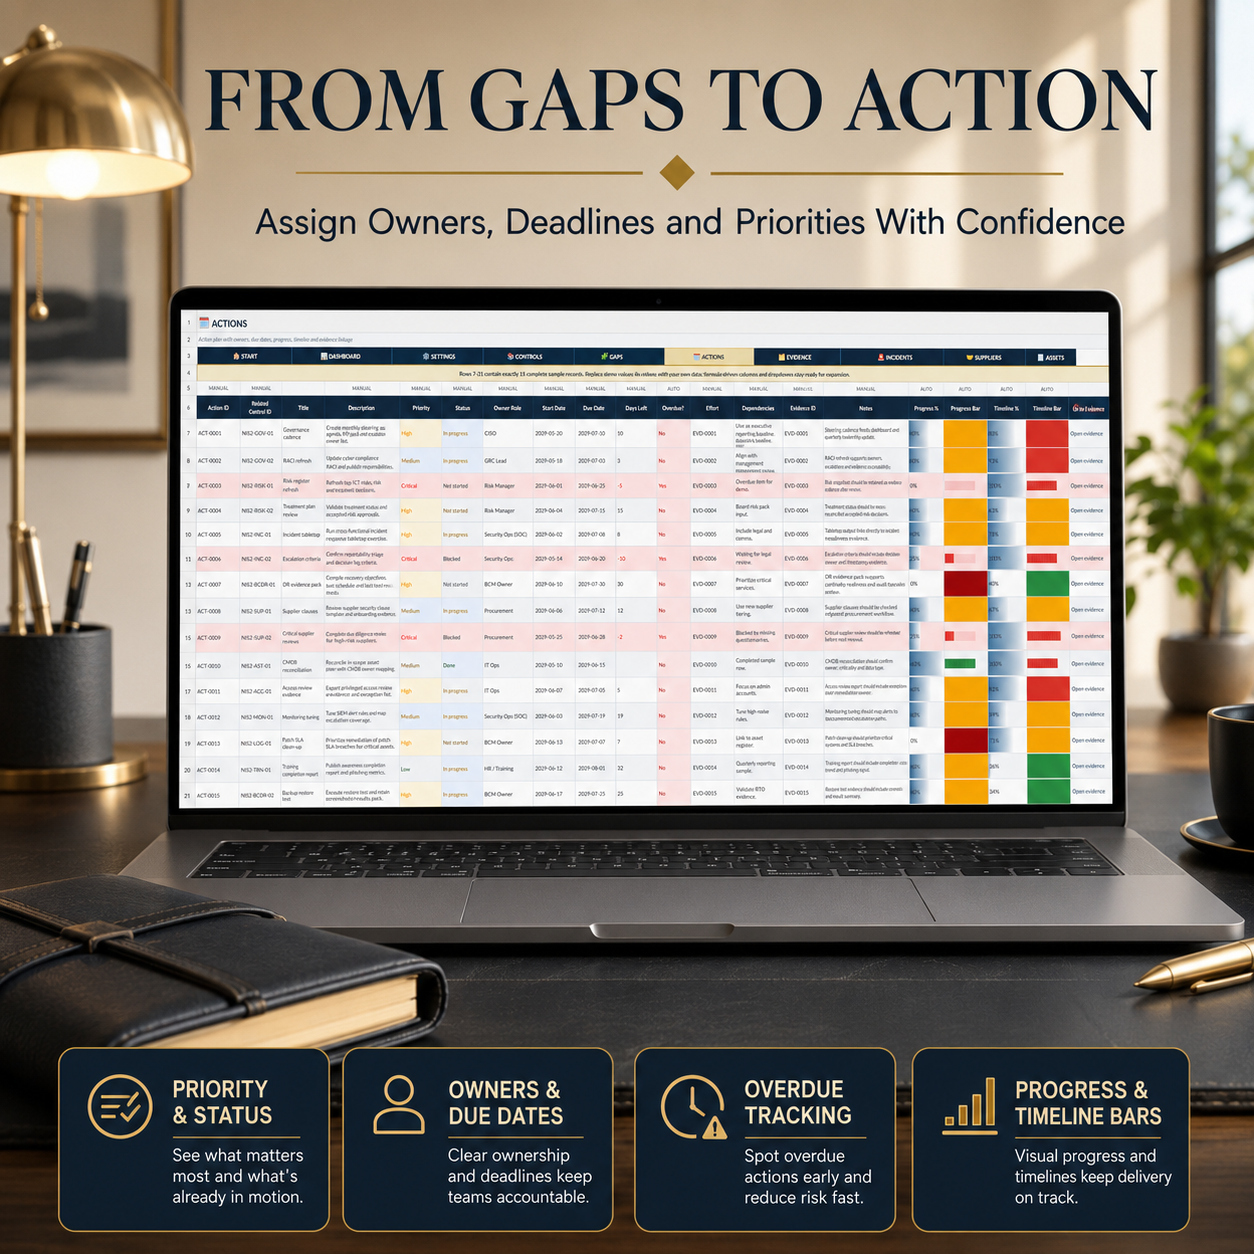
๐Ÿ—“๏ธ REMEDIATION ACTION PLAN
Turn identified gaps into owned actions.
Track:
๐Ÿ“Œ Priority
๐Ÿ“Œ Status
๐Ÿ‘ค Owner Role
๐Ÿ“… Start Date
๐Ÿ“… Due Date
โณ Days Remaining
โš ๏ธ Overdue Status
๐Ÿ“Š Progress %
๐Ÿ•’ Timeline Progress
๐Ÿ”— Dependencies
๐Ÿ—‚๏ธ Evidence References


This provides a structured way to move from assessment findings into practical remediation work.


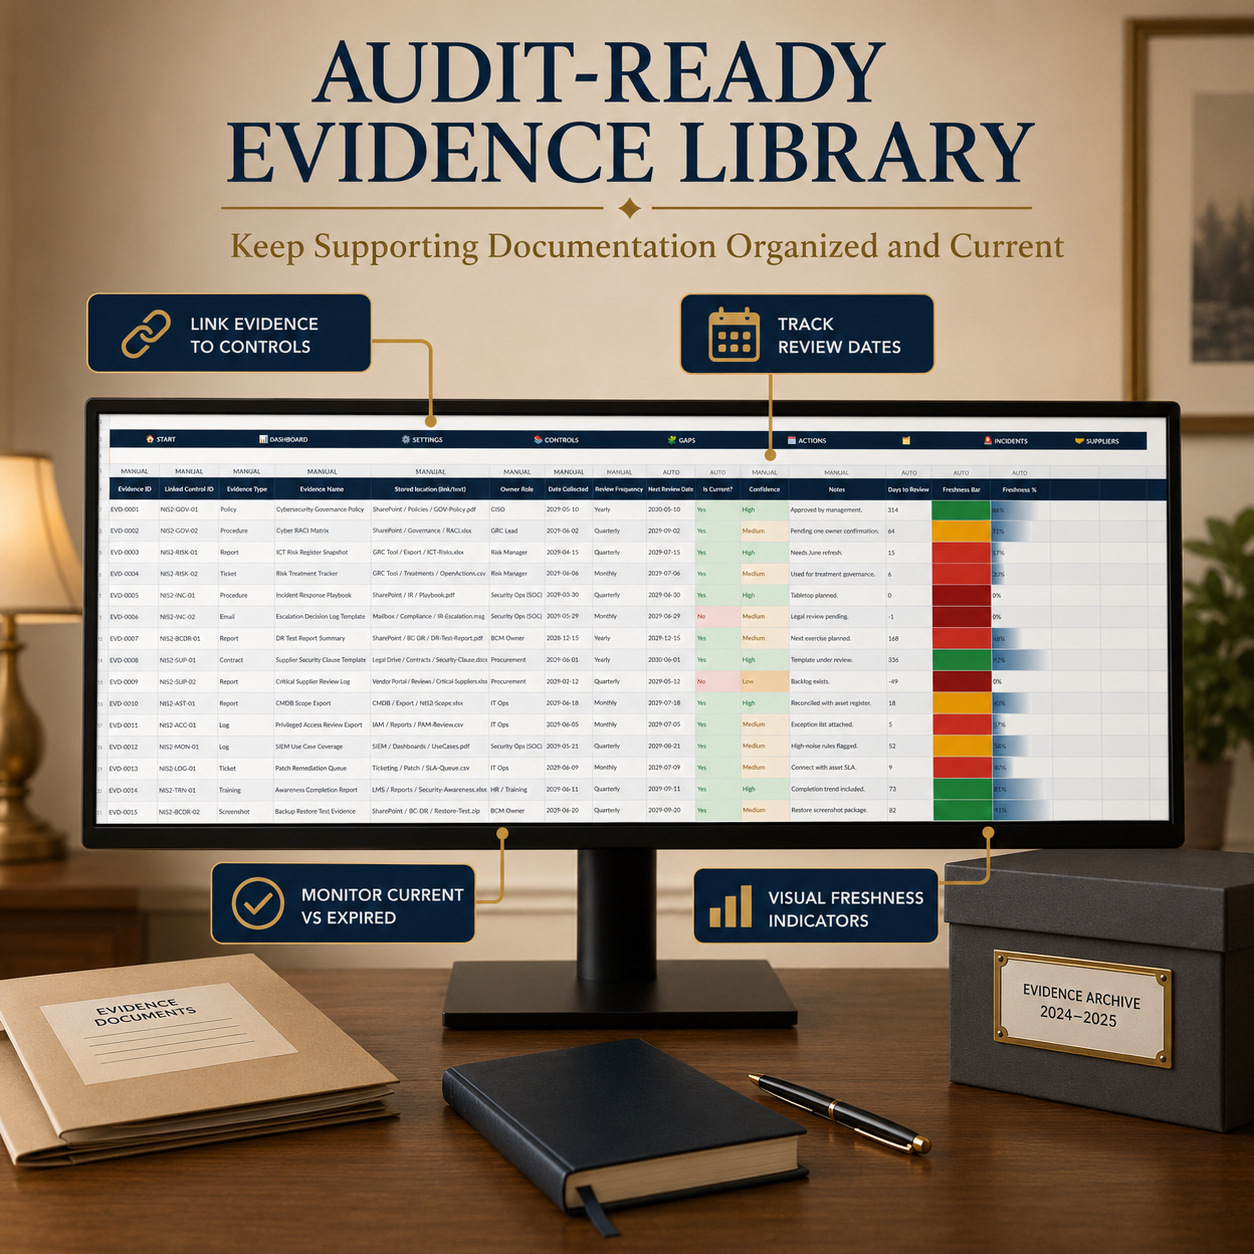
๐Ÿ—‚๏ธ EVIDENCE LIBRARY
Maintain a central index for supporting governance and security evidence such as:
๐Ÿ“„ Policies
๐Ÿ“‹ Procedures
๐Ÿ“Š Reports
๐ŸŽซ Tickets
๐Ÿ“ง Emails
๐Ÿ“š Training Records
๐Ÿ“ท Screenshots
๐Ÿ“œ Contracts
๐Ÿ–ฅ๏ธ Logs


Track collection dates, review frequency, ownership, confidence, next review dates and automatic evidence freshness.


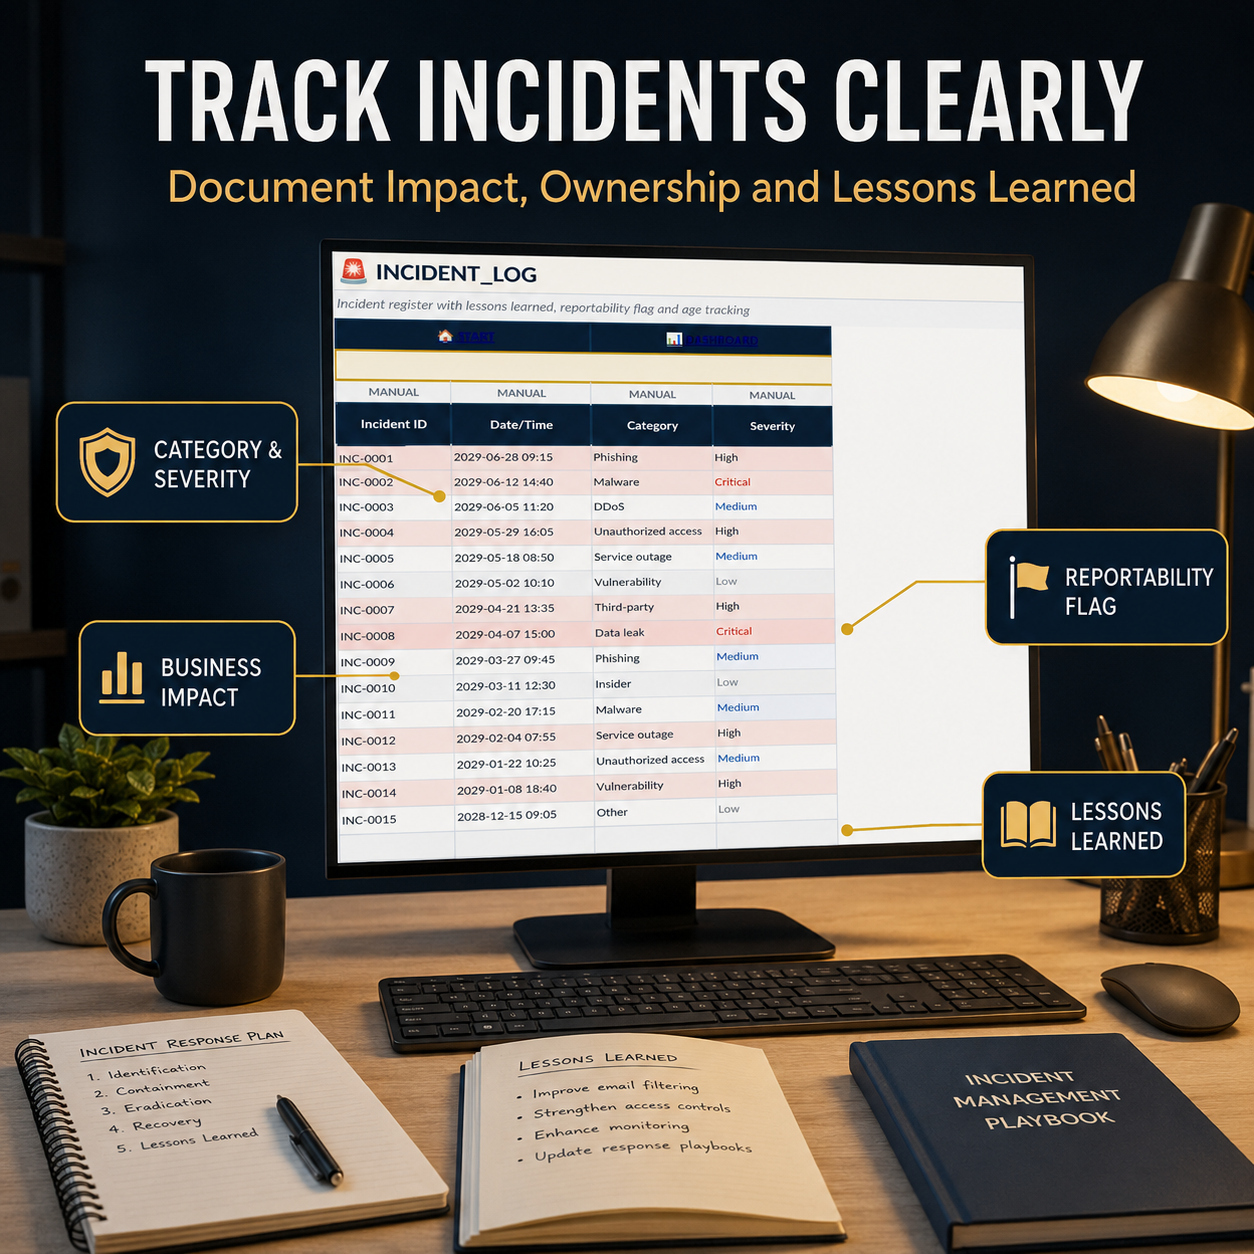
๐Ÿšจ INCIDENT REGISTER
Document internal security incidents with:
โ€ข Category
โ€ข Severity
โ€ข Description
โ€ข Business Impact
โ€ข Lessons Learned
โ€ข Status
โ€ข Owner
โ€ข Evidence Reference
โ€ข Reportability Flag
โ€ข Automatic Incident Age


This allows incidents and lessons learned to remain connected to the wider readiness program.


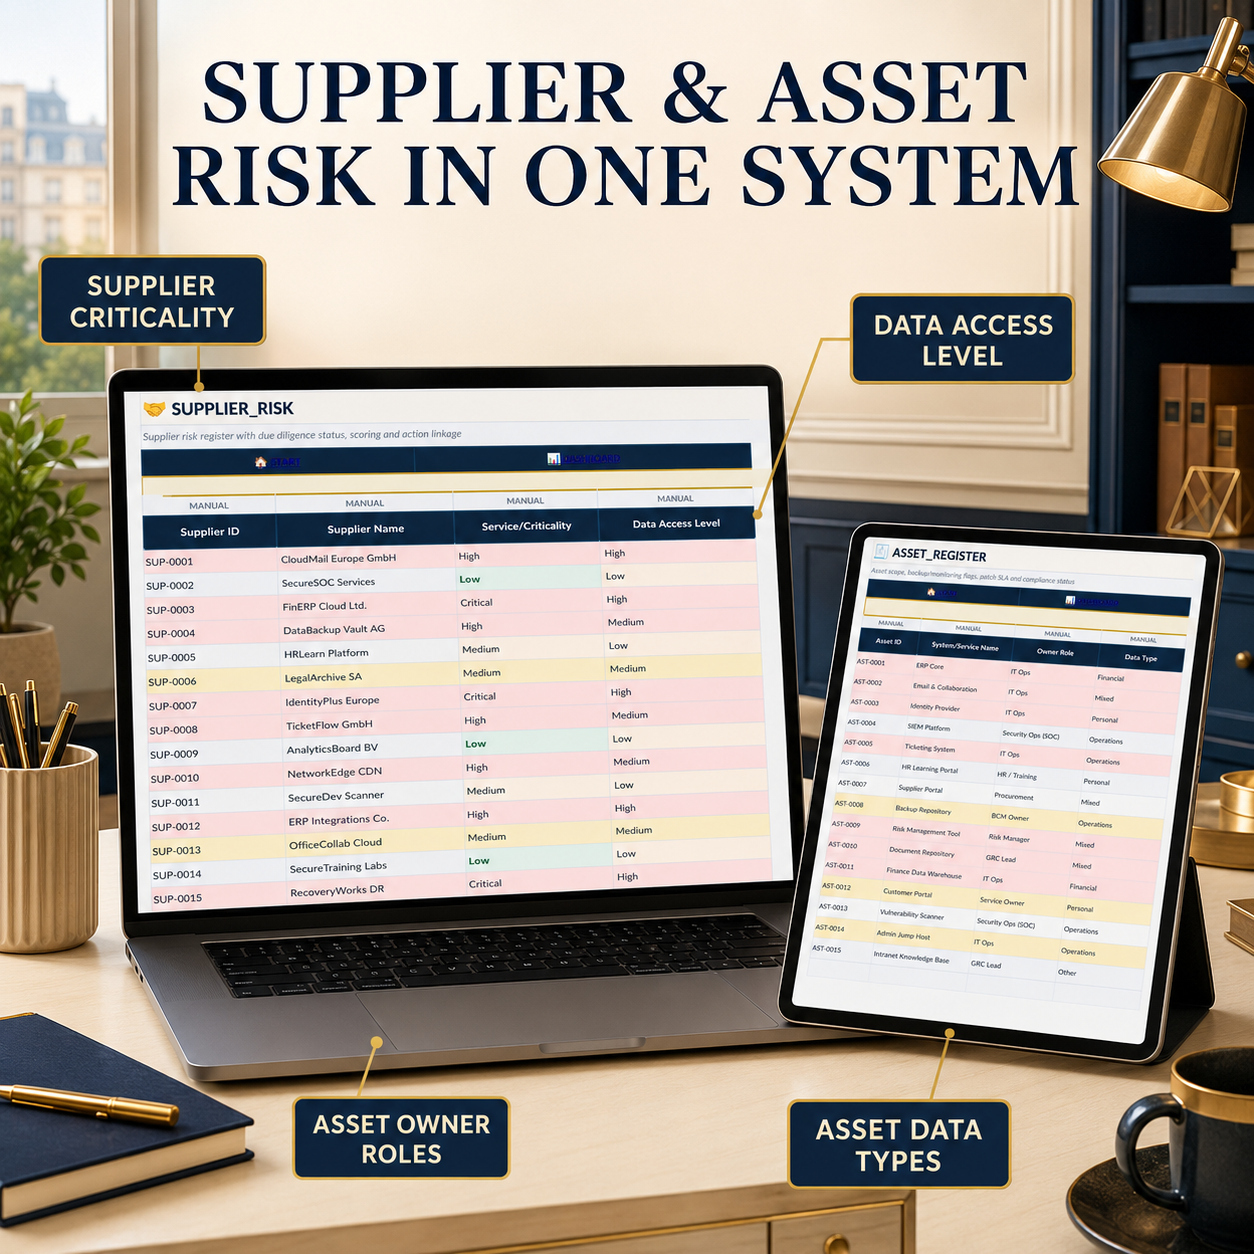
๐Ÿค SUPPLIER RISK REGISTER
Review third-party and supplier risk with:
โœ… Criticality
โœ… Data Access Level
โœ… Contract Renewal Date
โœ… Review Dates
โœ… Due Diligence Status
โœ… Linked Remediation Action
โœ… Automatic Risk Score
โœ… Automatic Risk Level


The tracker helps teams maintain visibility over higher-risk suppliers and pending review activity.


๐Ÿงพ ASSET & SERVICE REGISTER
Maintain visibility over in-scope systems and services.
Track:
โ€ข Owner
โ€ข Data Type
โ€ข Criticality
โ€ข Backup Status
โ€ข Monitoring Status
โ€ข Last Patch Date
โ€ข Patch SLA
โ€ข Patch Due Date
โ€ข Days to Due
โ€ข Patch Status
โ€ข SLA Usage %


Patch SLA values are automatically derived from asset criticality and the assumptions defined in Settings.


โš™๏ธ CENTRAL SETTINGS
The Settings sheet provides a central control area for:
๐Ÿข Organization and Scope
๐Ÿ‘ค Program Owner
๐Ÿ“… Reference Date
๐ŸŽฏ Target Readiness
๐Ÿ“‹ Dropdown Lists
โš–๏ธ Domain Weighting
๐Ÿ“Š Maturity Values
โฑ๏ธ Patch SLA Assumptions


This keeps key assumptions consistent across the workbook.


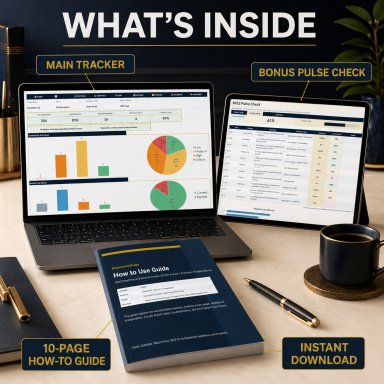
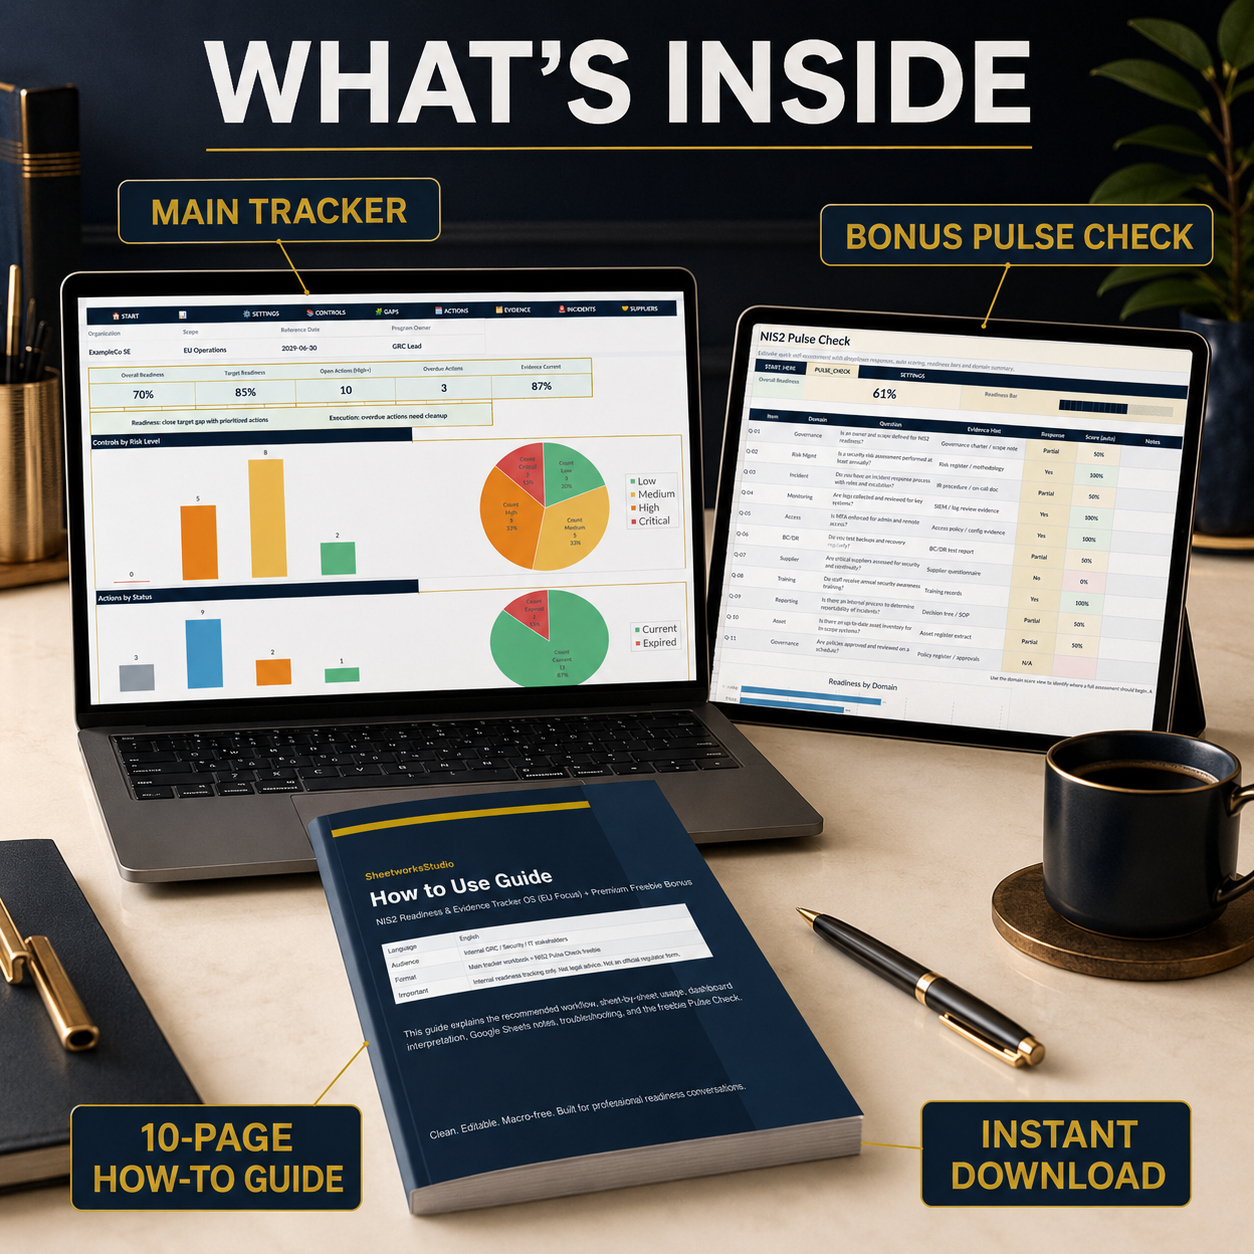
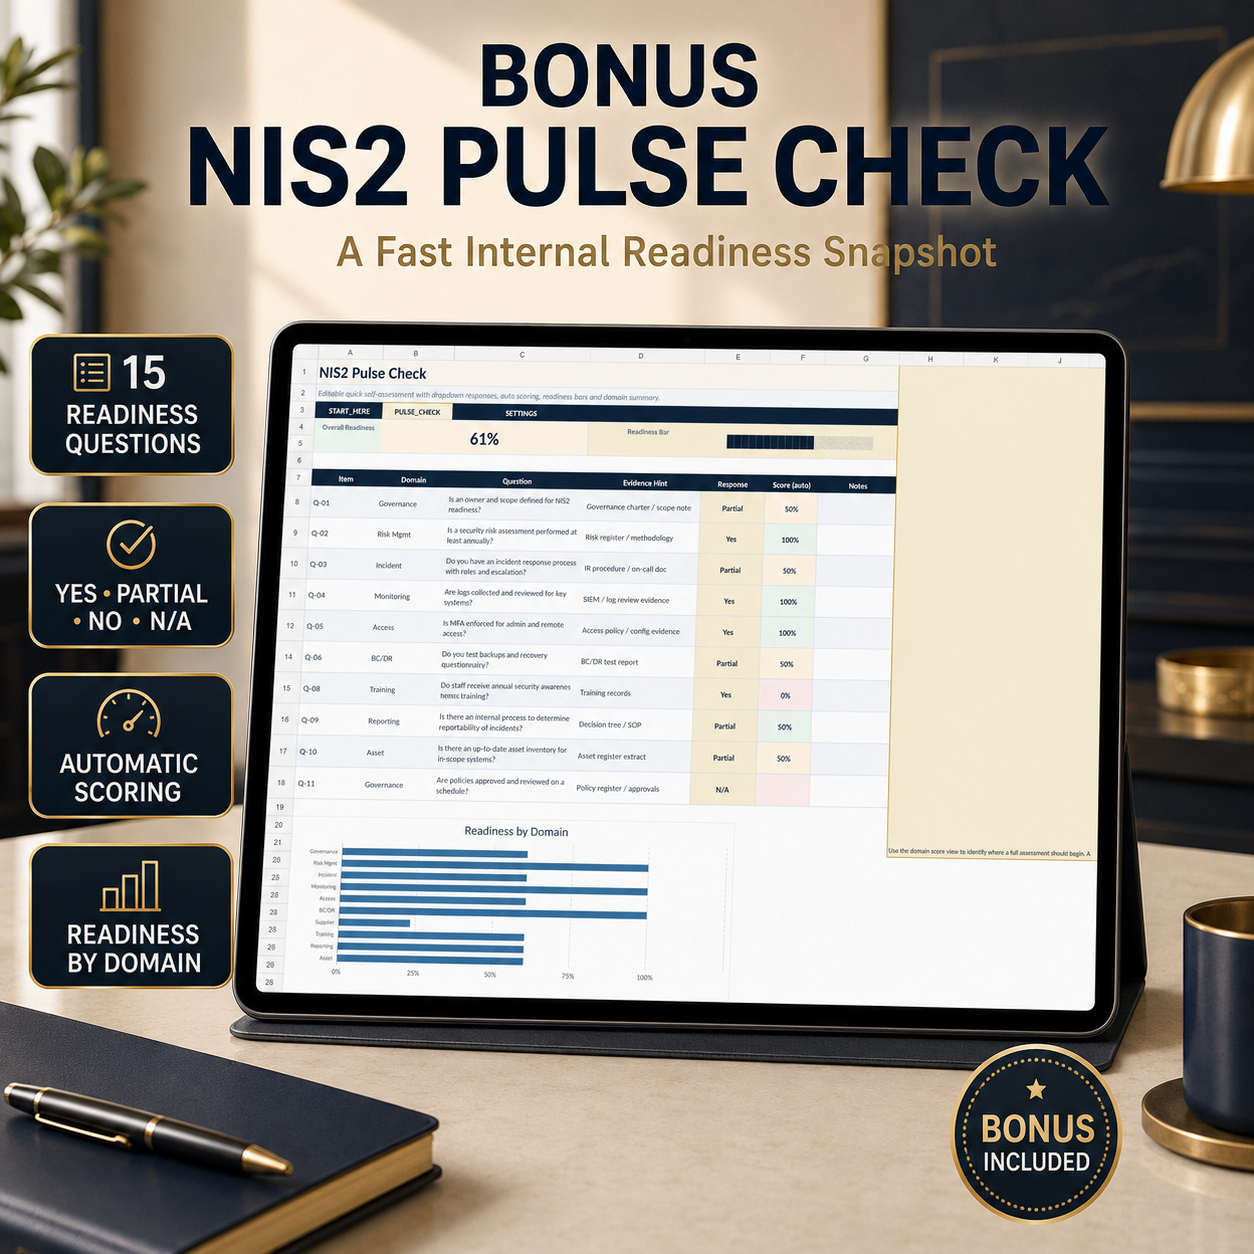
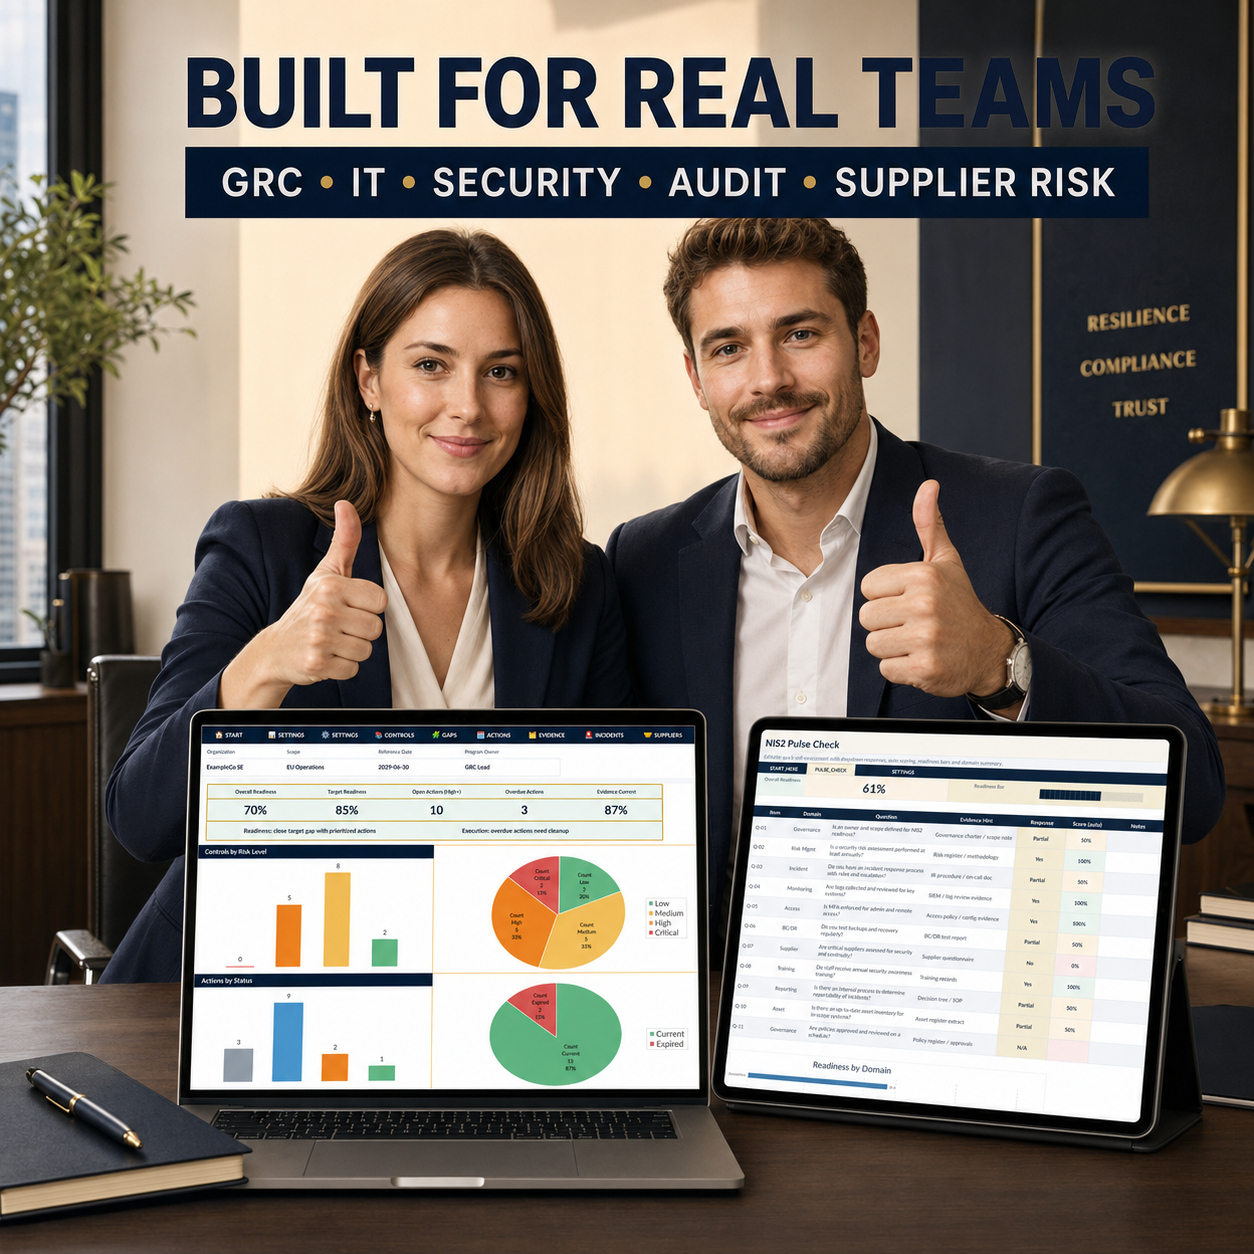
๐ŸŽ BONUS: NIS2 PULSE CHECK
The separate Pulse Check workbook provides a compact first-level readiness assessment.


It contains 15 structured questions across 10 readiness domains, with validated responses:
โœ… Yes
๐ŸŸก Partial
โŒ No
โž– N/A


Automatic scoring provides:
๐Ÿ“Š Weighted Overall Readiness
๐Ÿ“ˆ Domain-Level Analysis
๐ŸŽฏ Automatic Recommendation
๐ŸŸข Strong
๐ŸŸ  Attention
๐Ÿ”ด Priority
N/A responses are counted as answered but correctly excluded from both domain and overall readiness calculations.


A dynamic domain chart makes weak and strong areas easier to identify before moving into the full tracker.


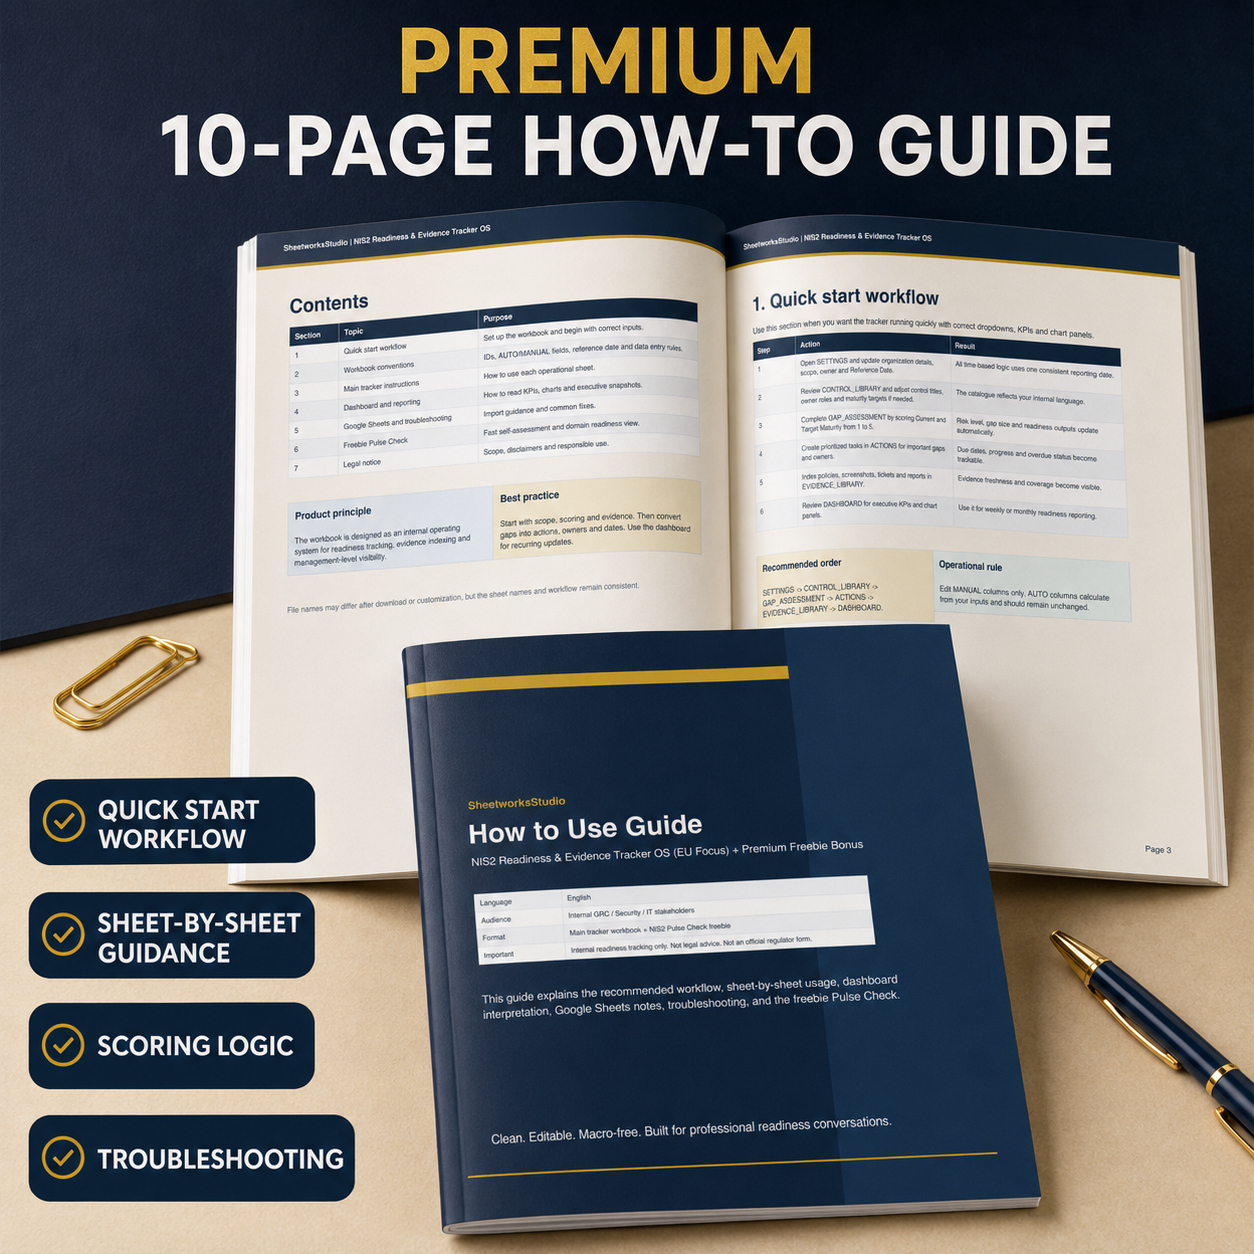
๐Ÿ“˜ 10-PAGE HOW-TO GUIDE
The included PDF guide explains:
๐Ÿš€ Quick Start Workflow
๐Ÿงญ Workbook Conventions
โœ๏ธ MANUAL vs AUTO Fields
๐Ÿ”— Control, Action, Evidence, Incident, Supplier & Asset IDs
๐Ÿ“š Control & Gap Workflow
๐Ÿ—“๏ธ Remediation Actions
๐Ÿ—‚๏ธ Evidence Management
๐Ÿšจ Incidents
๐Ÿค Supplier Risk
๐Ÿงพ Asset & Patch Readiness
๐Ÿ“Š Dashboard Reporting
๐ŸŽ NIS2 Pulse Check
โž– N/A-Safe Scoring
โ˜๏ธ Google Sheets Usage
๐Ÿ› ๏ธ Troubleshooting
โš–๏ธ Legal & Release Checklist


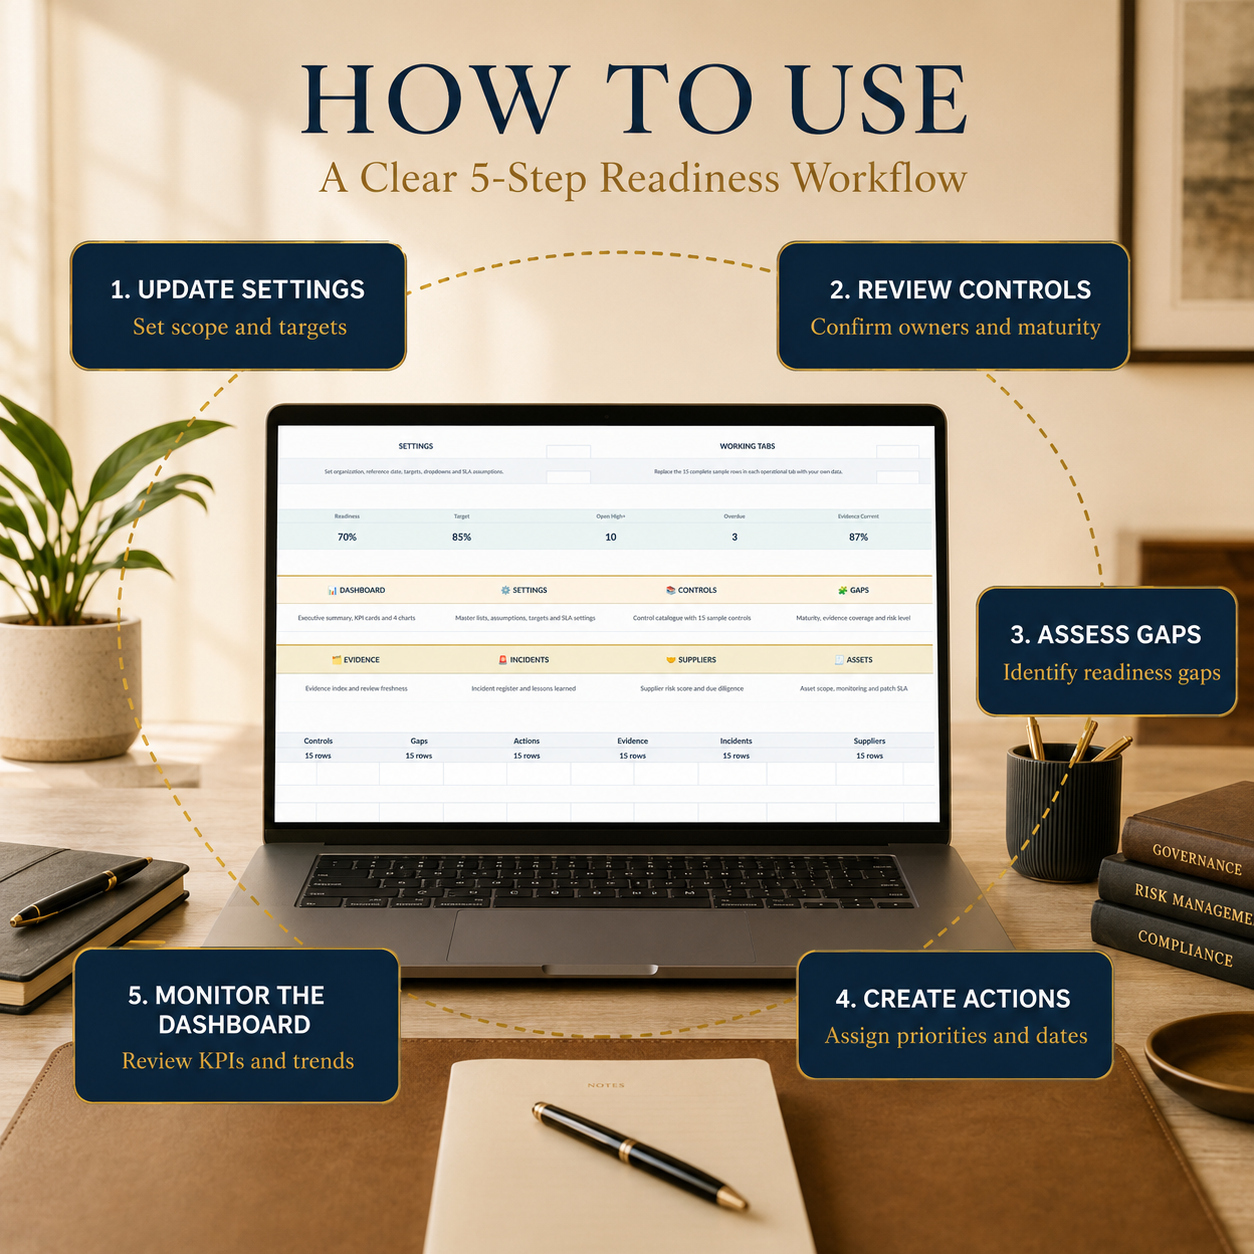
๐Ÿ’Ž ONE CONNECTED READINESS WORKFLOW
The system connects:
Configure โ†’ Controls โ†’ Assess Gaps โ†’ Create Actions โ†’ Maintain Evidence โ†’ Monitor Operations โ†’ Review Dashboard


This creates a repeatable internal readiness process while leaving regulatory interpretation, legal obligations and final compliance decisions with the organization and its qualified advisers.


P. DISCLAIMER
โš–๏ธ NIS2, CYBERSECURITY & COMPLIANCE DISCLAIMER
This product is an independent editable management, documentation and internal-readiness template intended for general organizational use.


It is not an official form or product issued by the European Union, a national competent authority, supervisory body or regulator.


The toolkit does not constitute legal, regulatory, cybersecurity, audit, certification or professional advice and does not guarantee compliance with NIS2 or any other law, regulation or framework.


Readiness percentages, maturity scores, risk classifications, SLA indicators and Pulse Check results are internal planning aids only and should not be interpreted as formal compliance determinations.


Users remain responsible for determining applicable legal obligations, adapting the toolkit to their organization and obtaining qualified professional advice where necessary.

This Best Practice includes
1 ร— NIS2 Readiness & Evidence Tracker OS (.xlsx), 1 ร— NIS2 Pulse Check (.xlsx), 1 ร— How-to-Use Guide (.pdf)

Acquire business license for $39.90

Add to cart

Add to bookmarks

Discuss

Further information

โ€ข Centralize internal readiness information
โ€ข Establish a structured control catalogue
โ€ข Assess current vs target maturity
โ€ข Prioritize control gaps and remediation work
โ€ข Maintain evidence ownership and freshness
โ€ข Track incidents, suppliers and critical assets
โ€ข Provide recurring management-level readiness reporting

This toolkit works particularly well for organizations that:
โ€ข currently use several separate readiness spreadsheets
โ€ข need structured control and evidence tracking
โ€ข want clearer ownership of remediation activities
โ€ข require recurring internal readiness reviews
โ€ข need visibility over suppliers and critical assets
โ€ข prefer an editable Excel framework
โ€ข want a practical starting point before implementing specialist GRC software

This toolkit is not intended to:
โ€ข provide an official NIS2 compliance determination
โ€ข replace legal or regulatory advice
โ€ข automatically determine whether an organization is in scope
โ€ข submit regulatory notifications
โ€ข monitor infrastructure in real time
โ€ข generate security evidence automatically
โ€ข replace cybersecurity platforms
โ€ข replace a full enterprise GRC solution
โ€ข guarantee compliance with NIS2 or any other regulation

0.0 / 5 (0 votes)

please wait...