ISO 27001 ISMS Readiness & Risk Management Excel Toolkit | Audit, Controls, CAPA, Word Templates & PPT
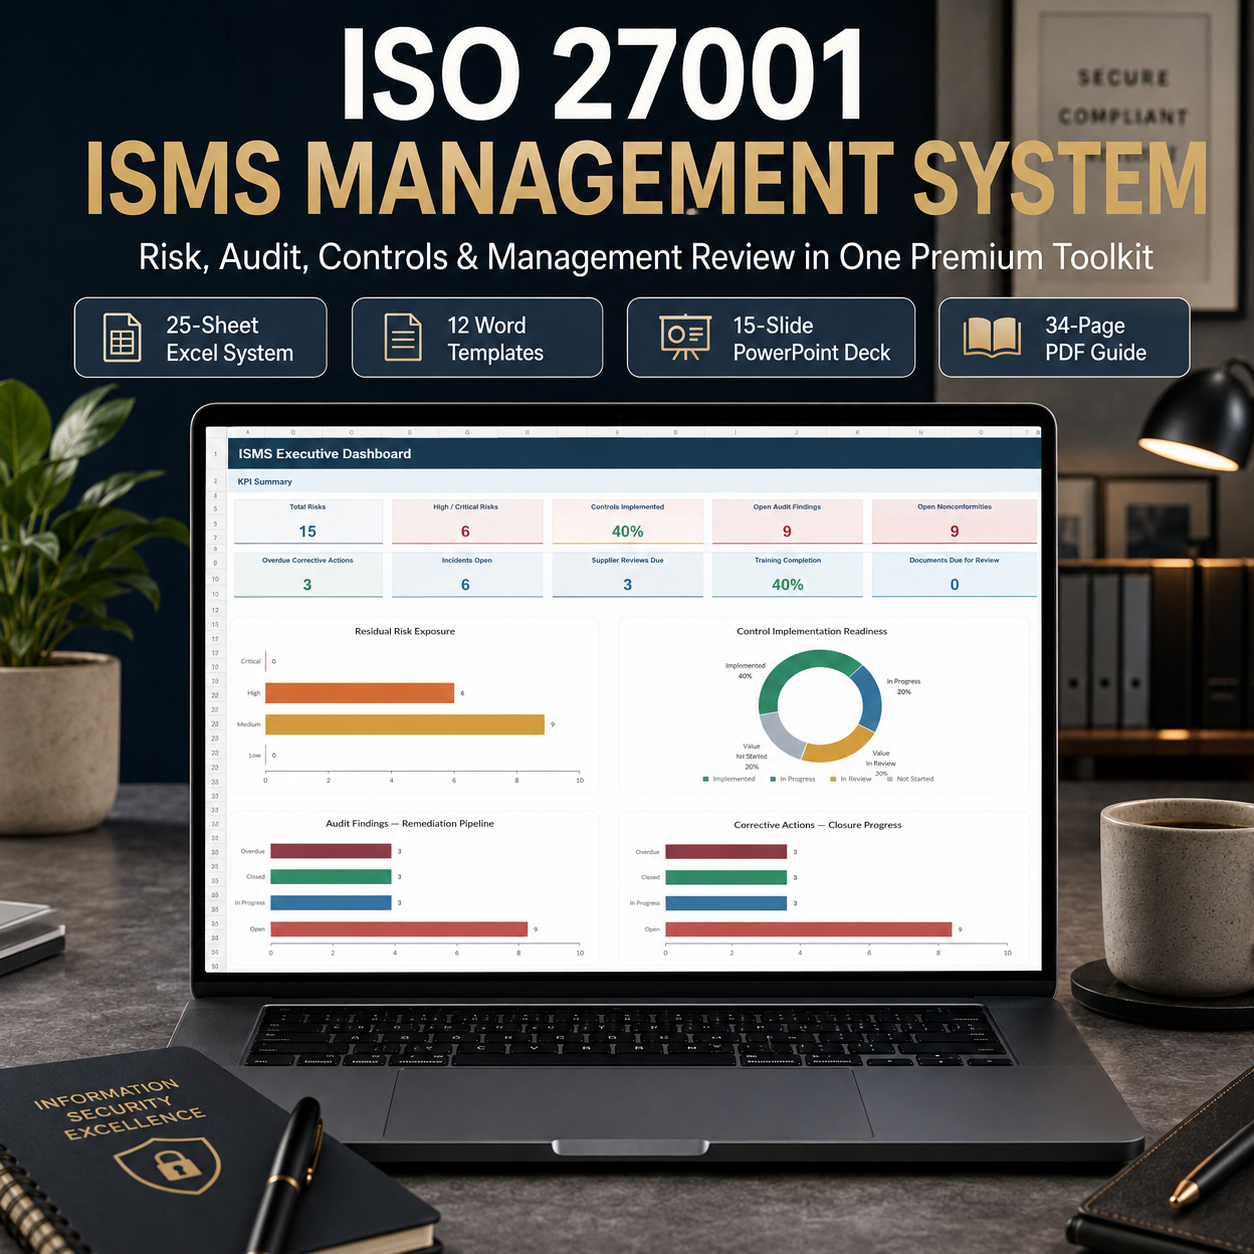
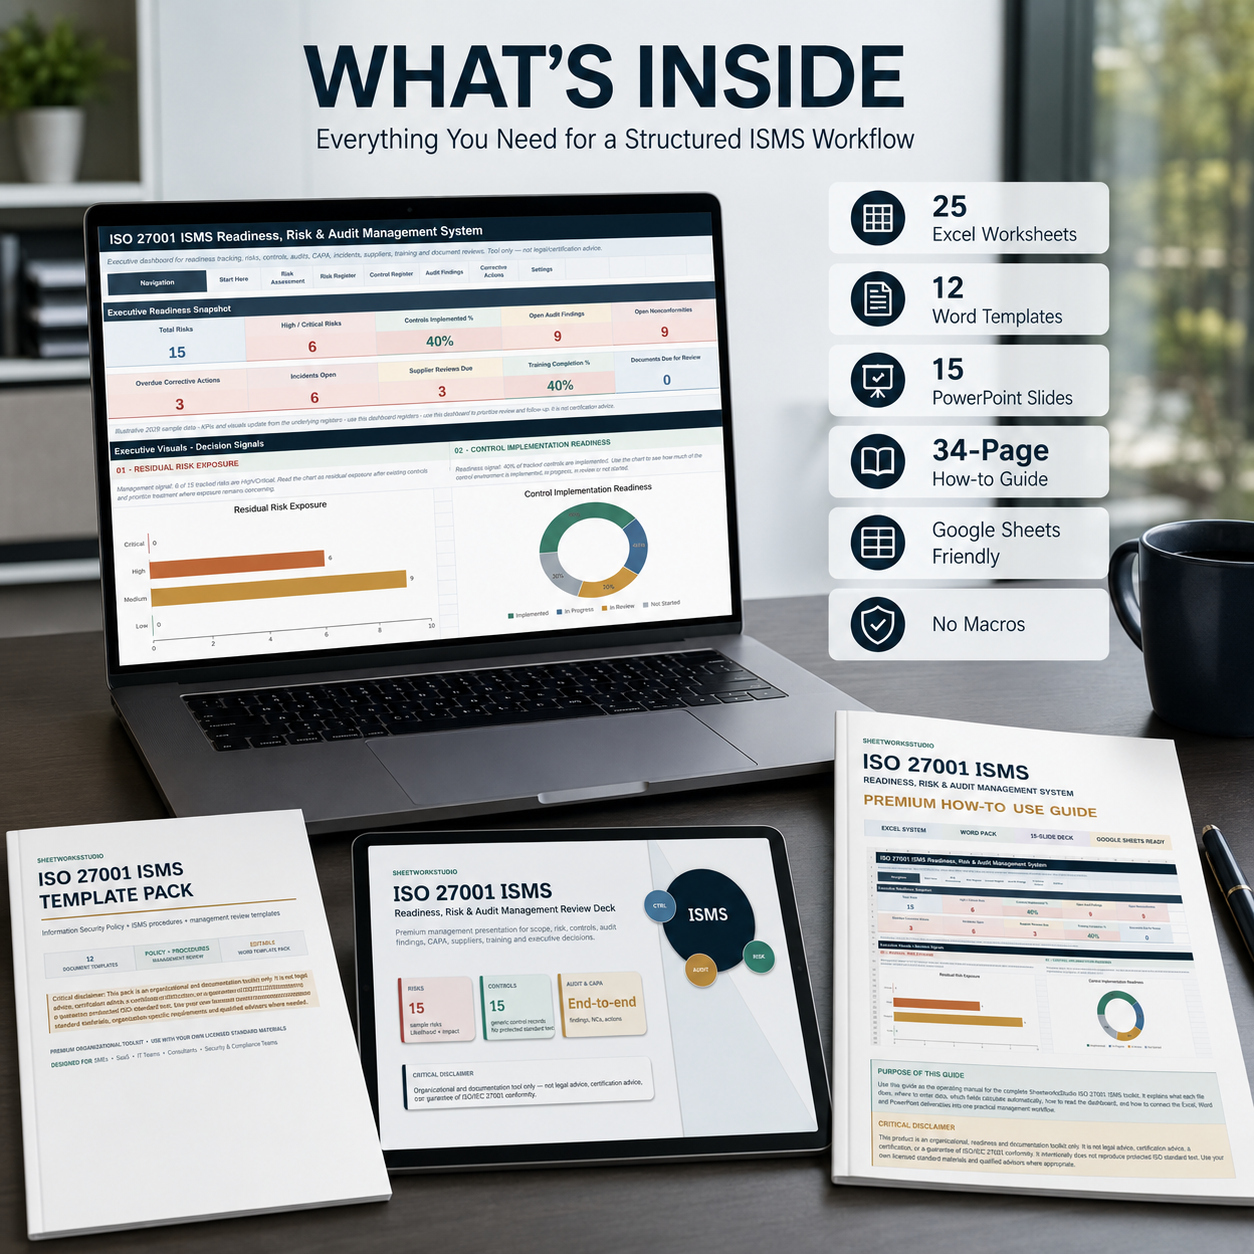
ISO 27001 ISMS readiness toolkit with risk, controls, audits, CAPA, suppliers, evidence, dashboard, 12 Word templates, PPT deck and PDF guide.
Further information
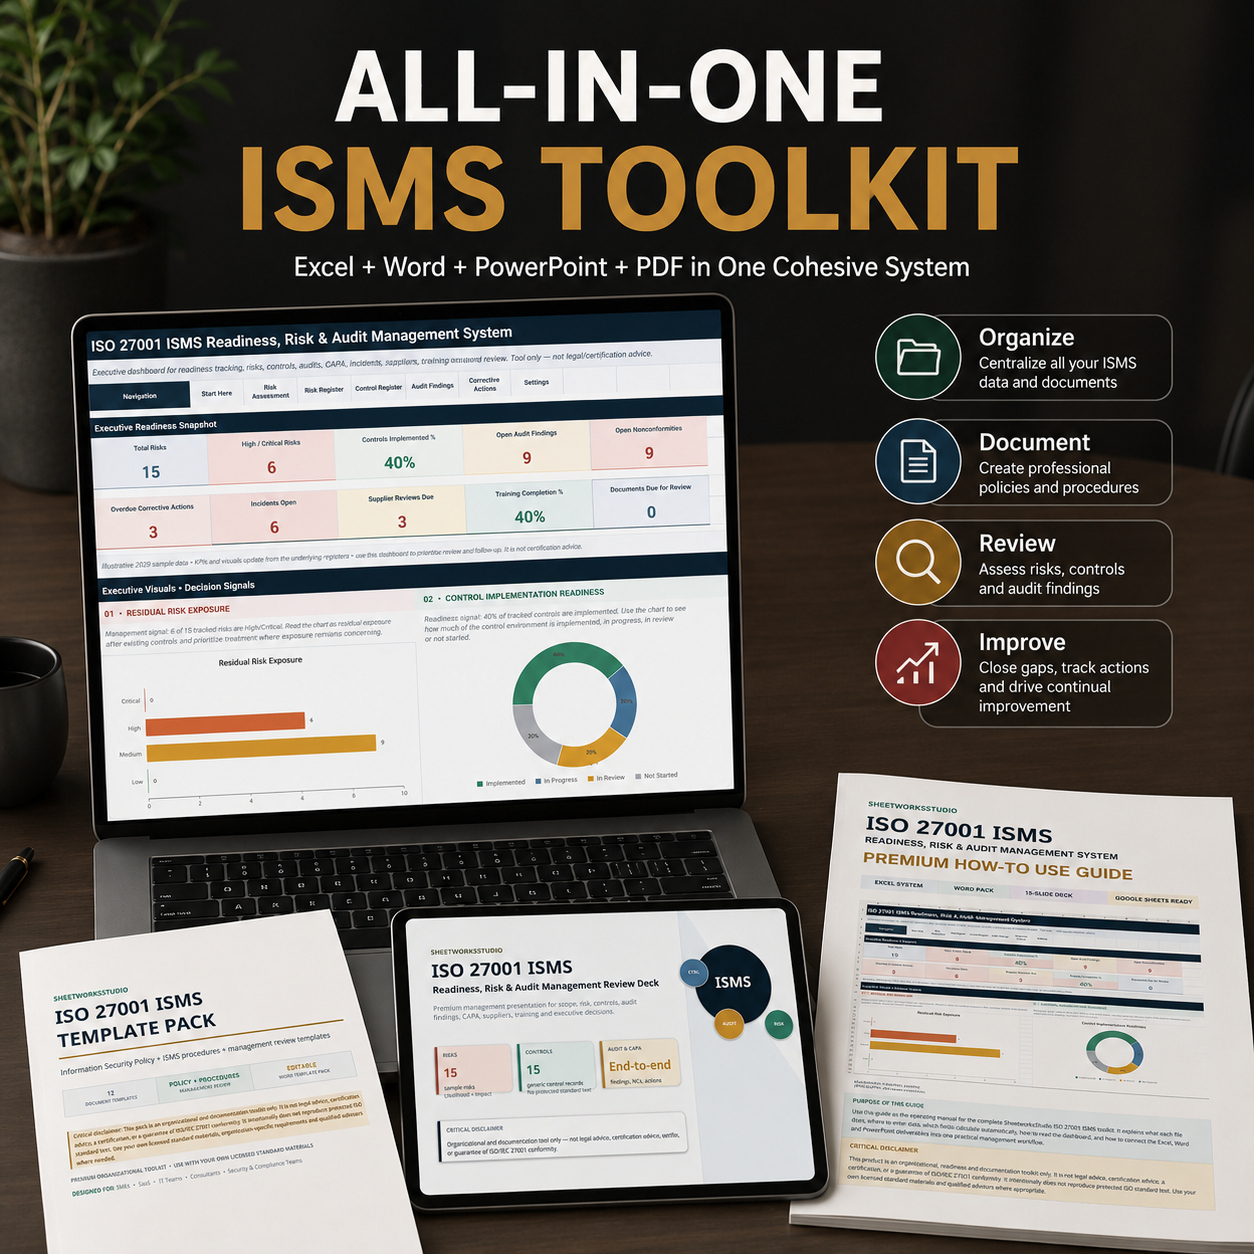
The objective of this toolkit is to provide organizations, ISMS managers, security teams, consultants, and internal audit professionals with a structured framework for organizing information-security governance and recurring ISMS management activities.
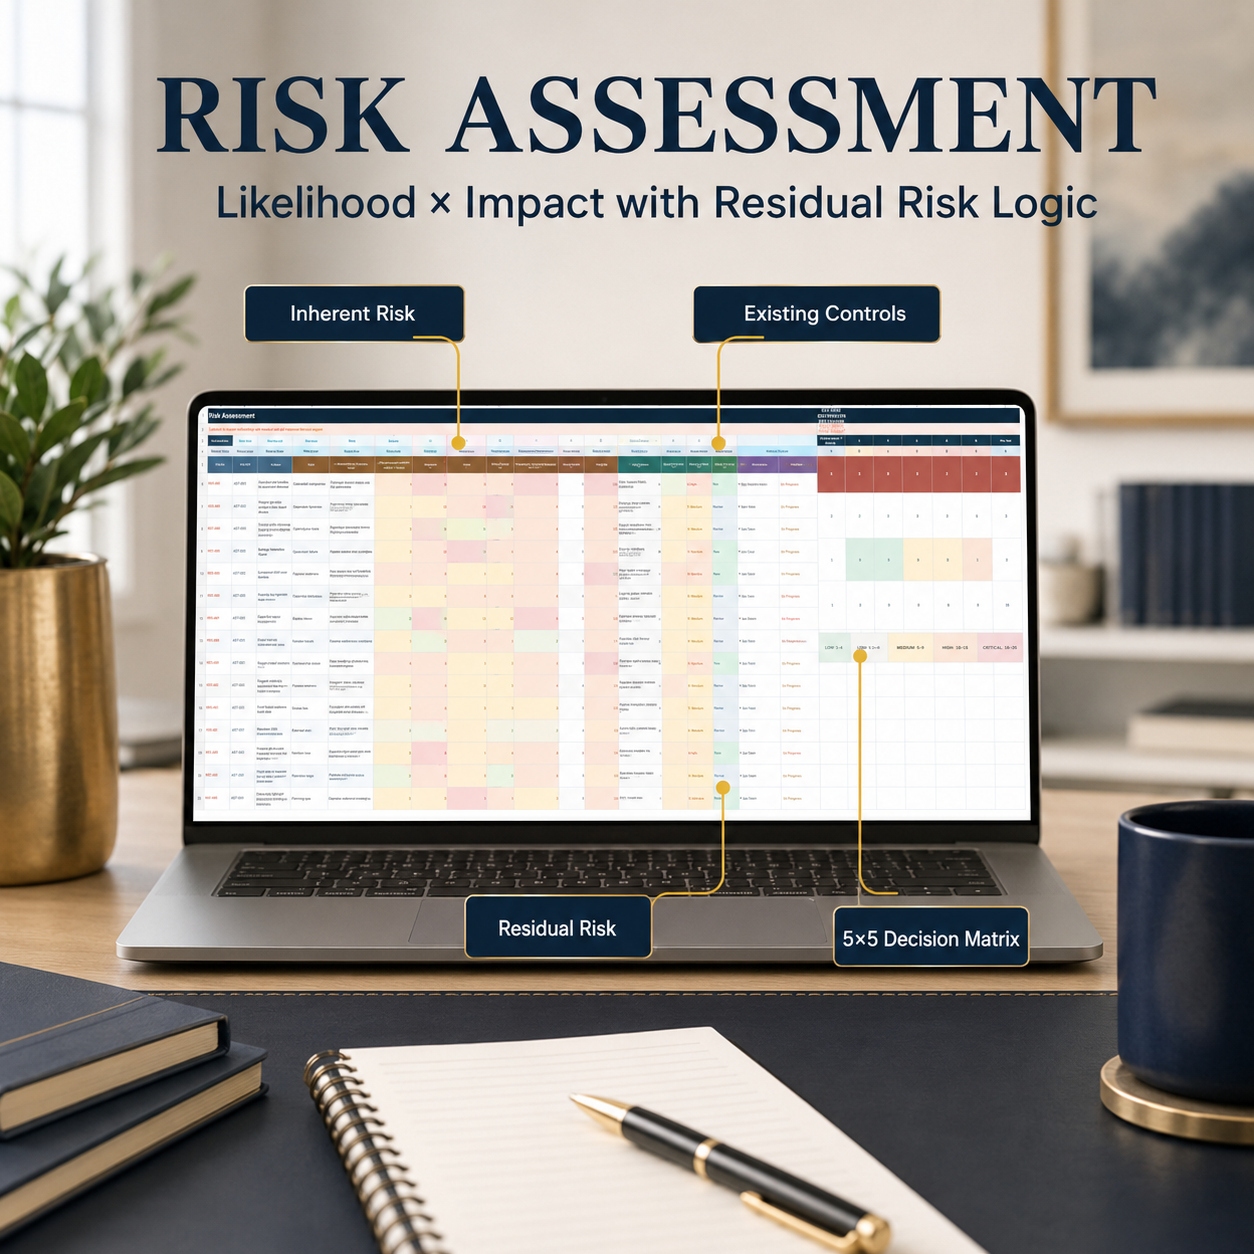
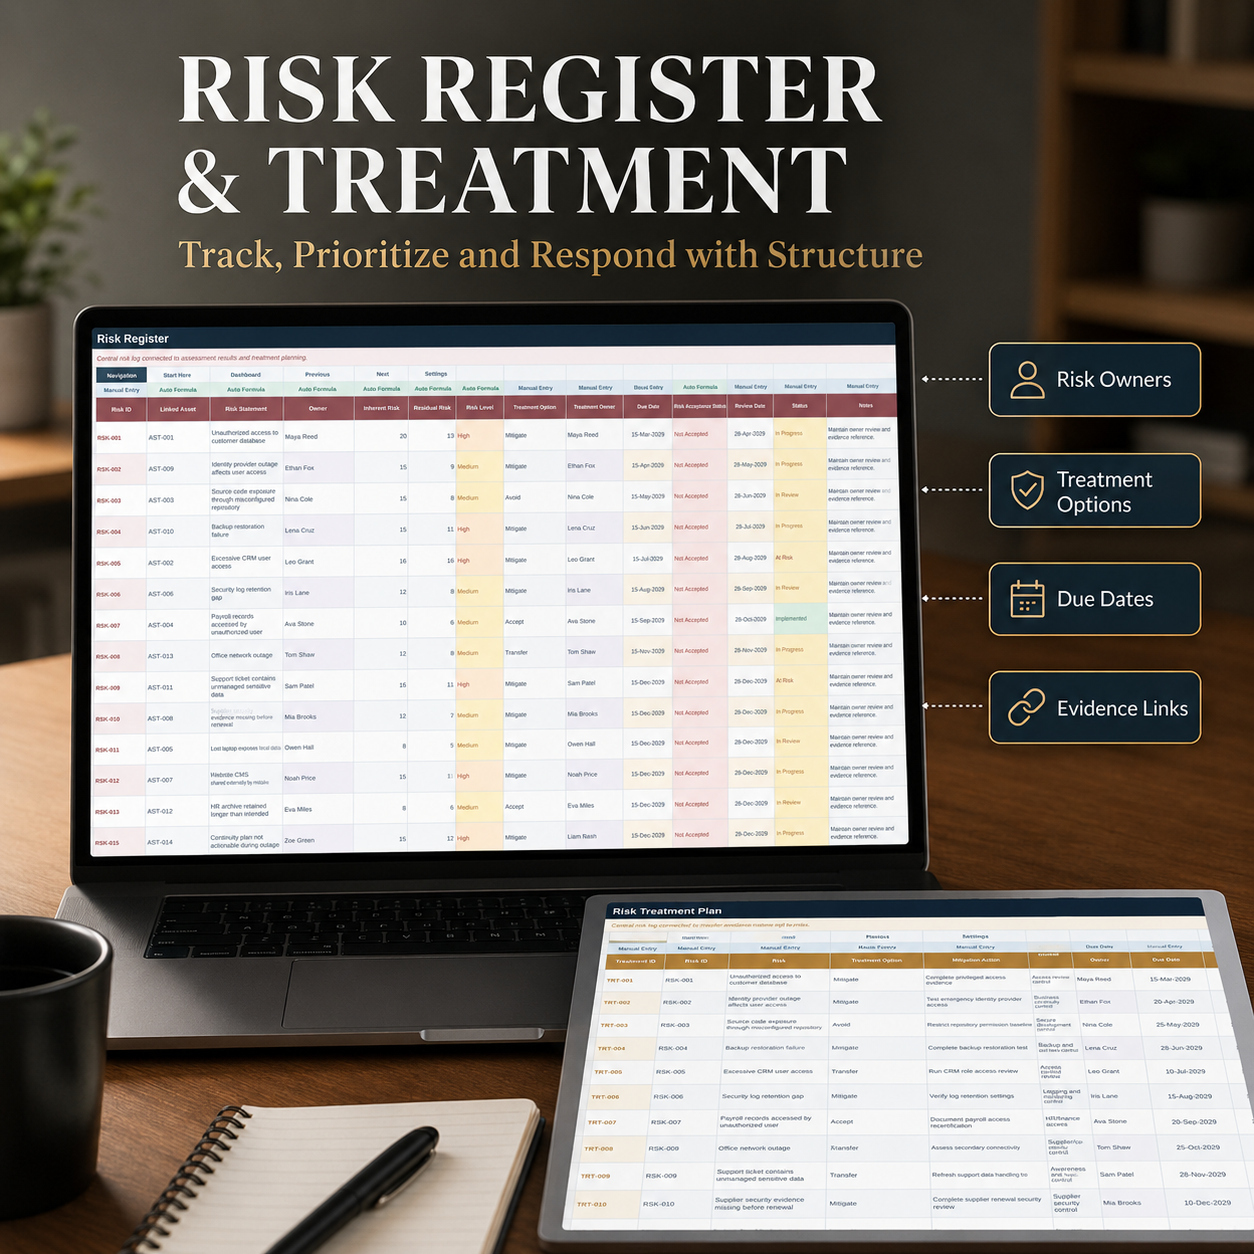
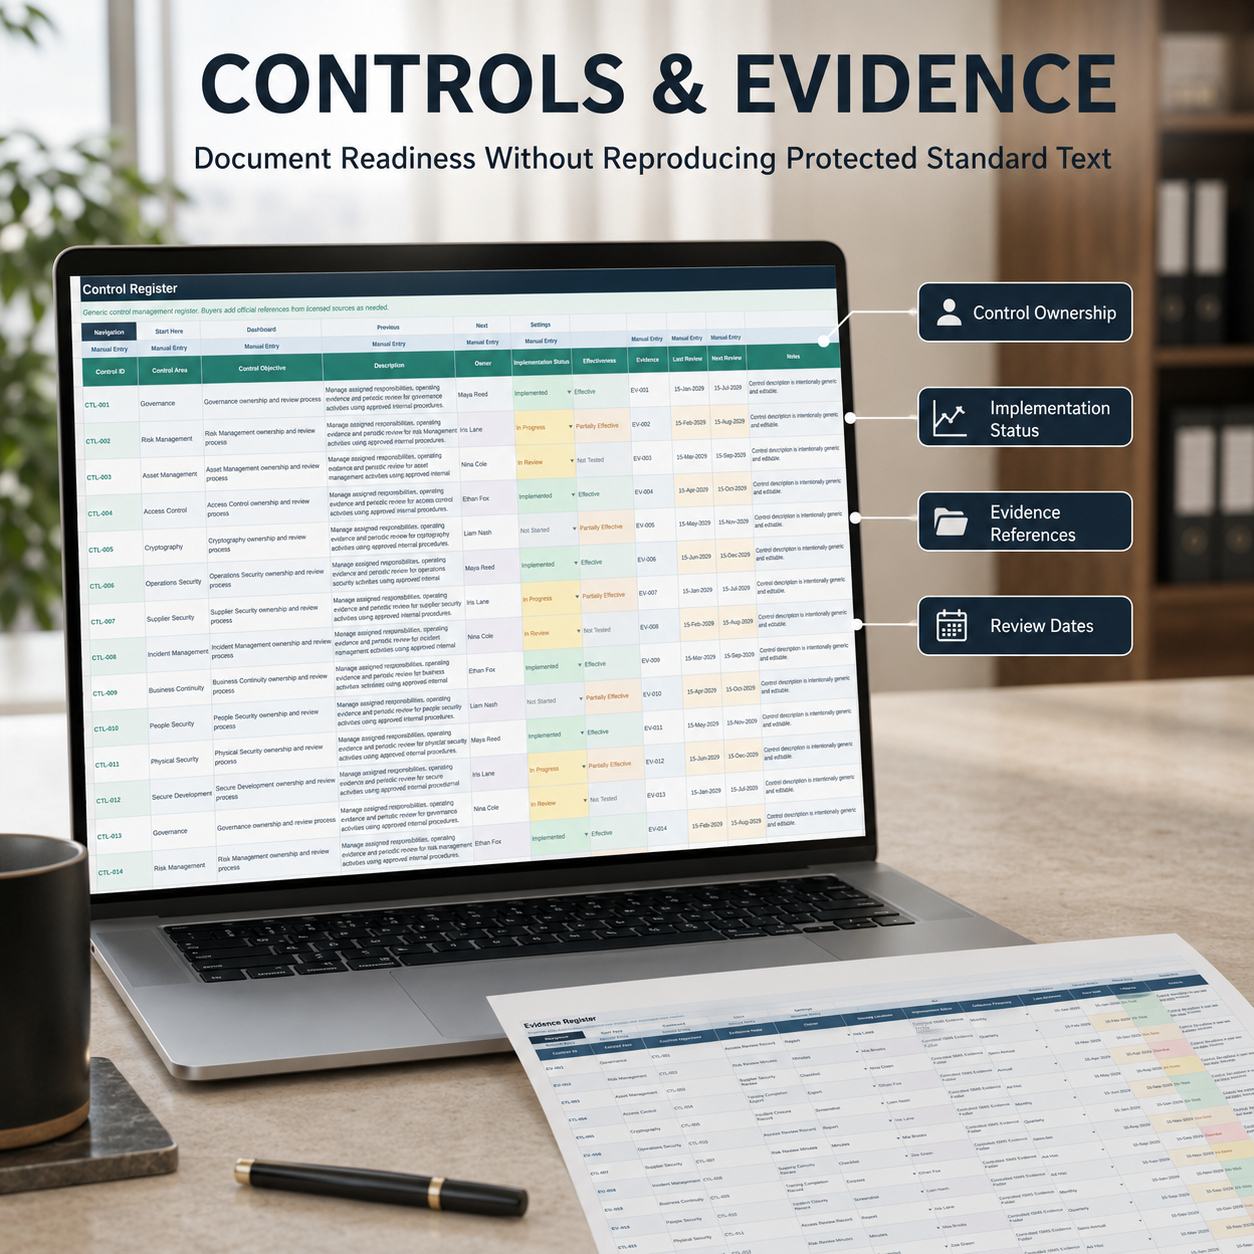
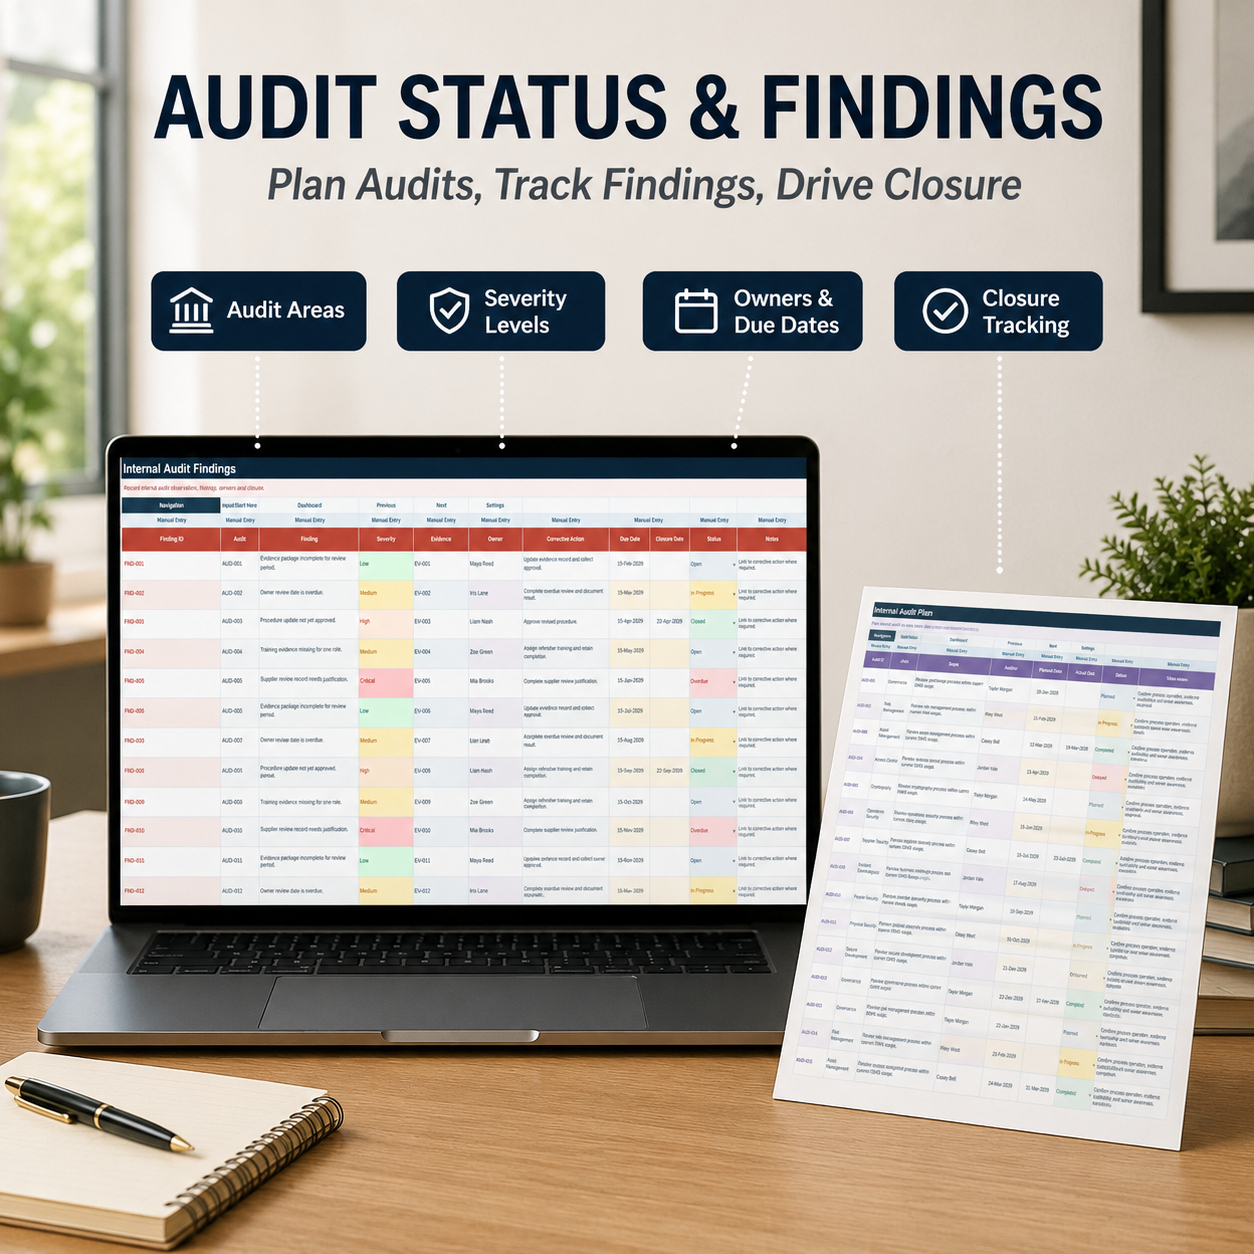
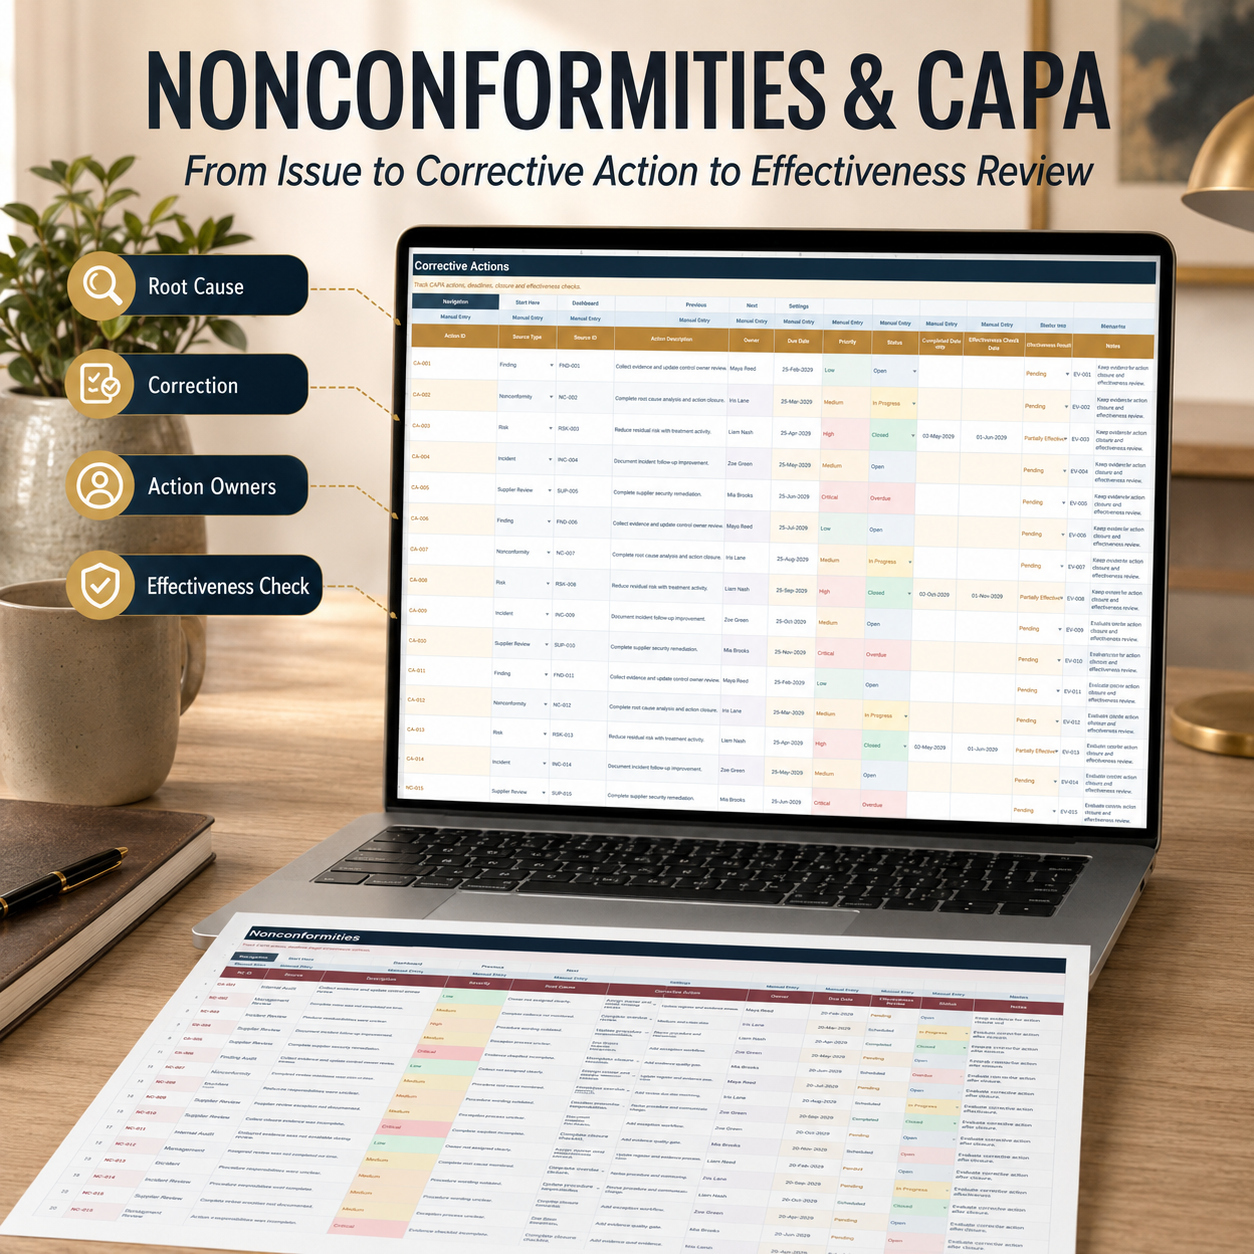
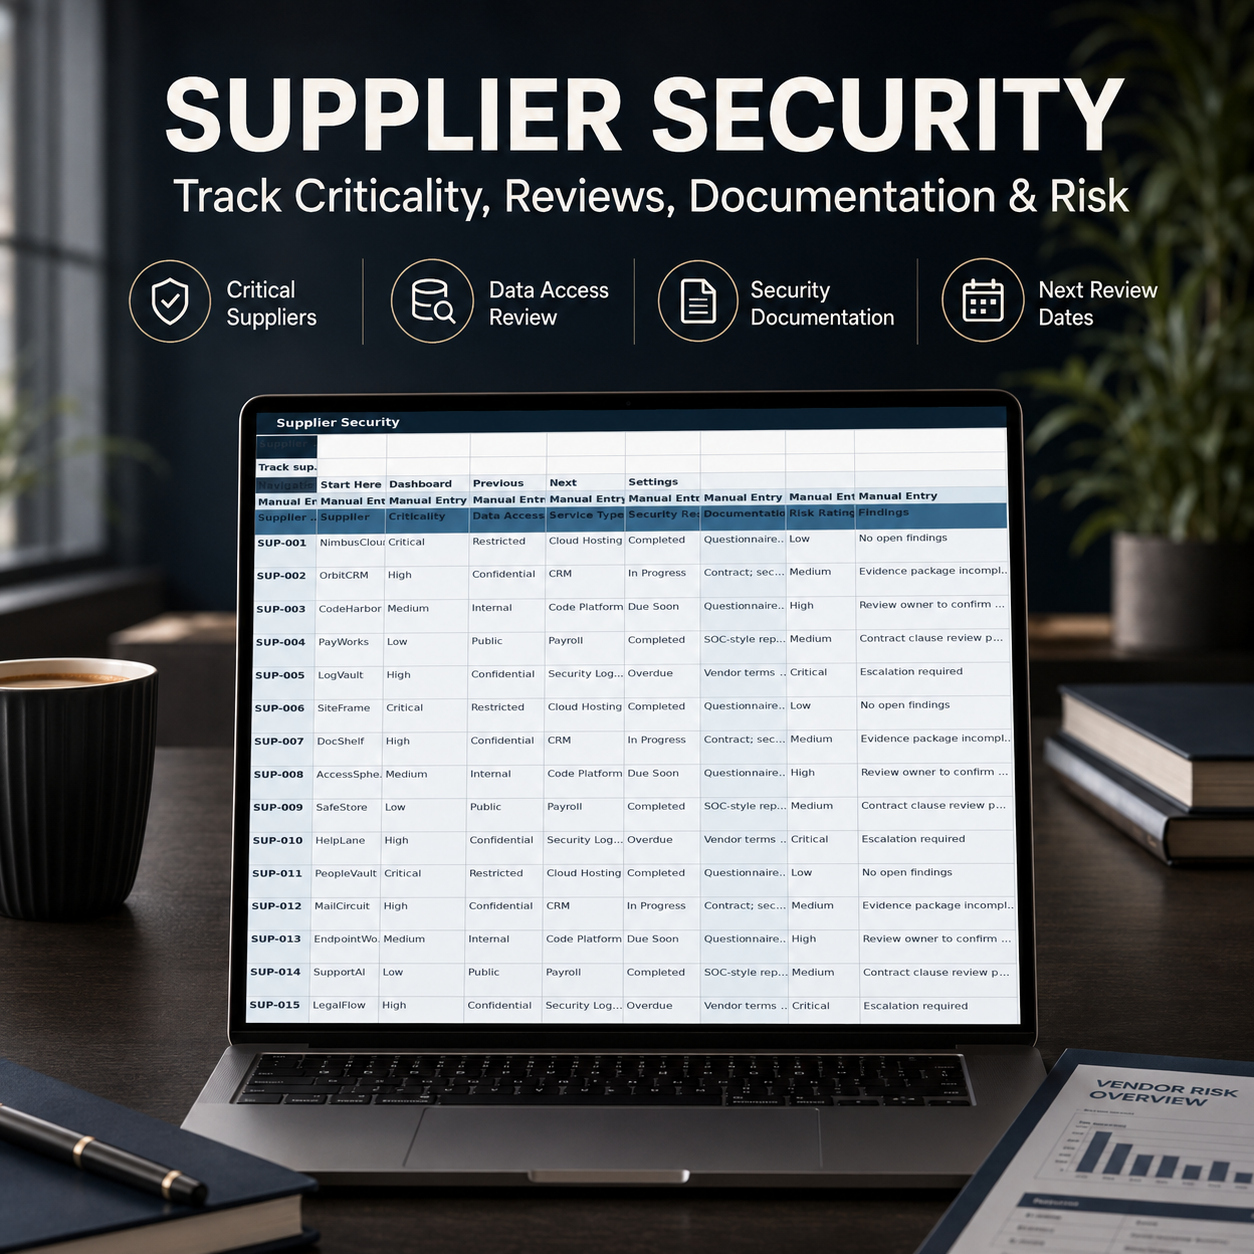
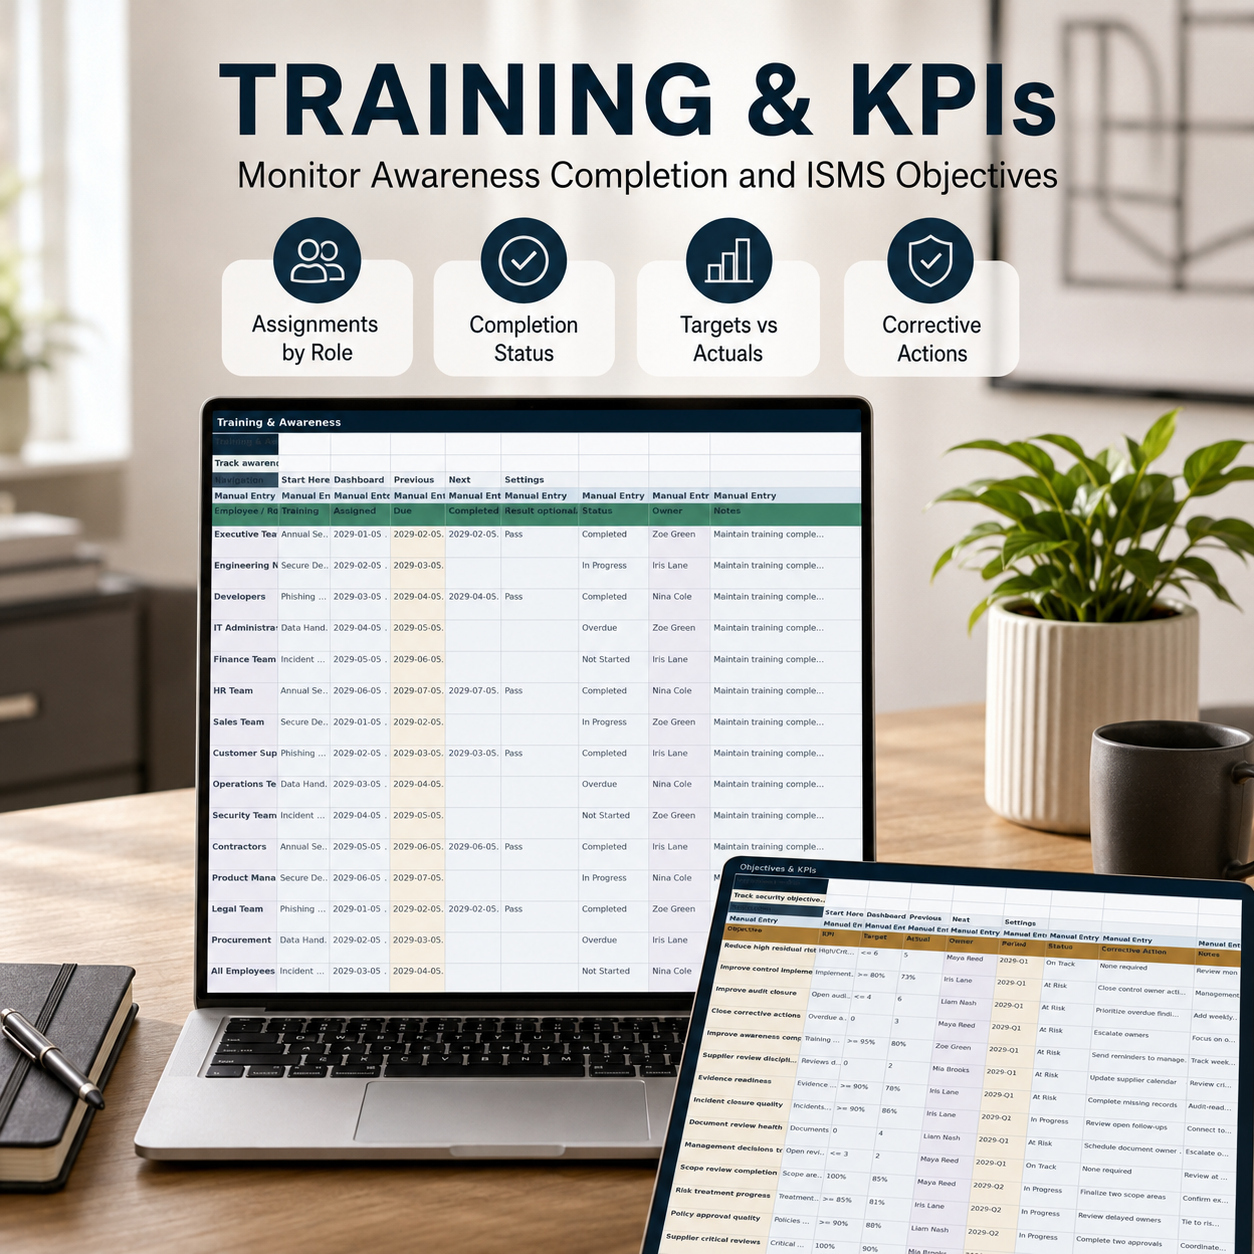
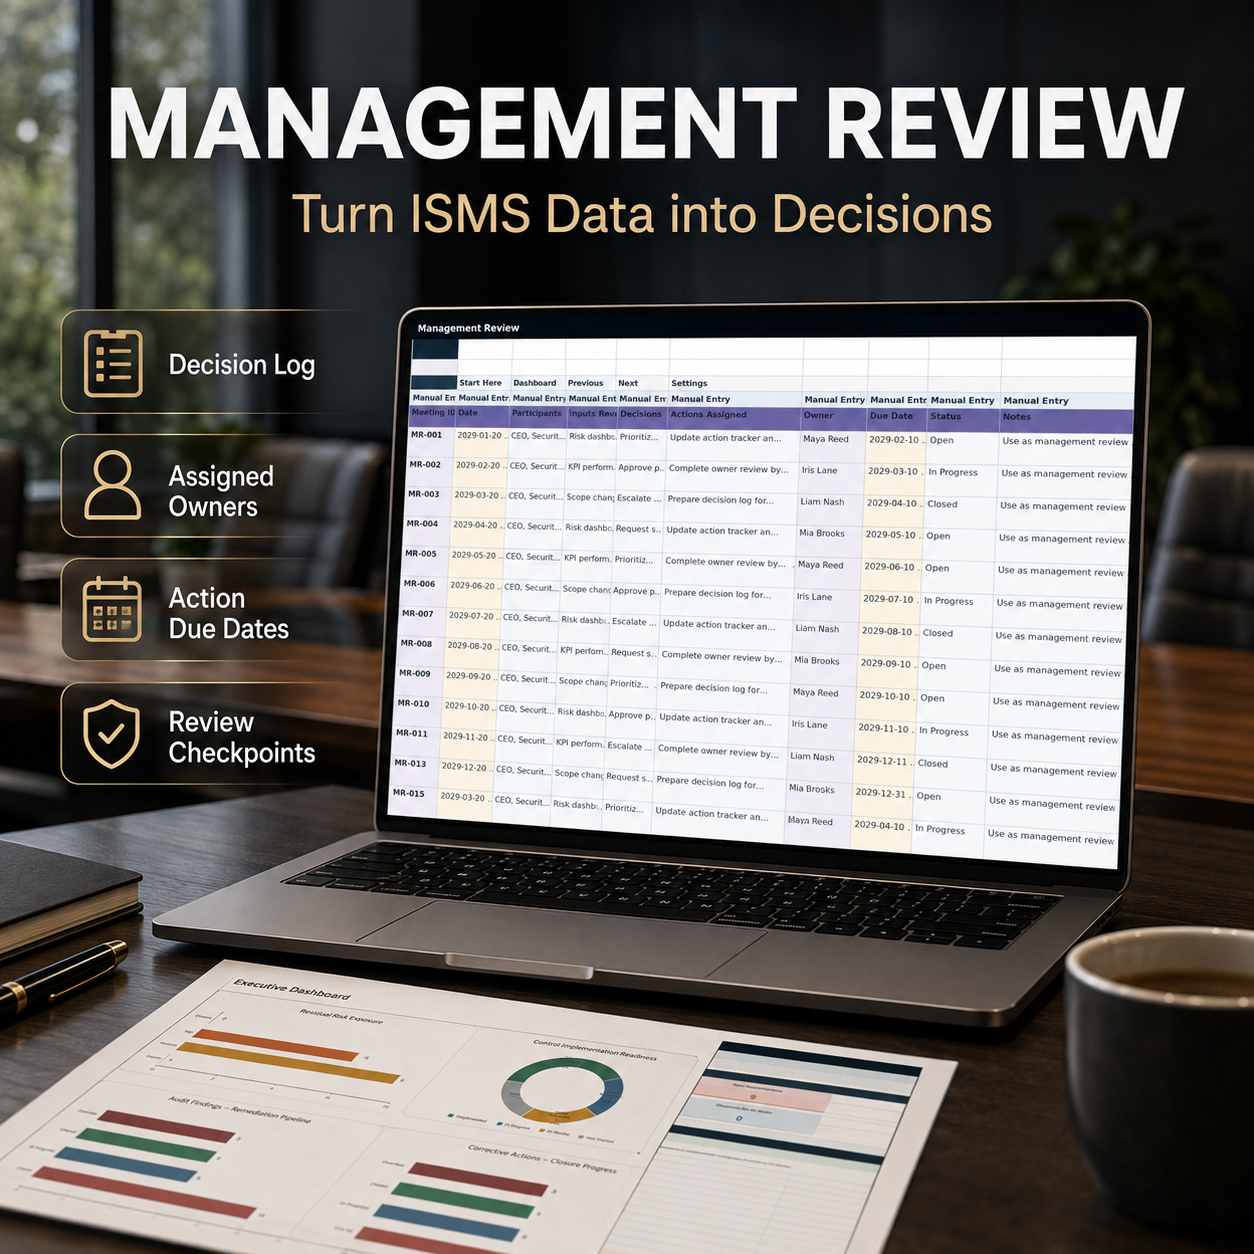
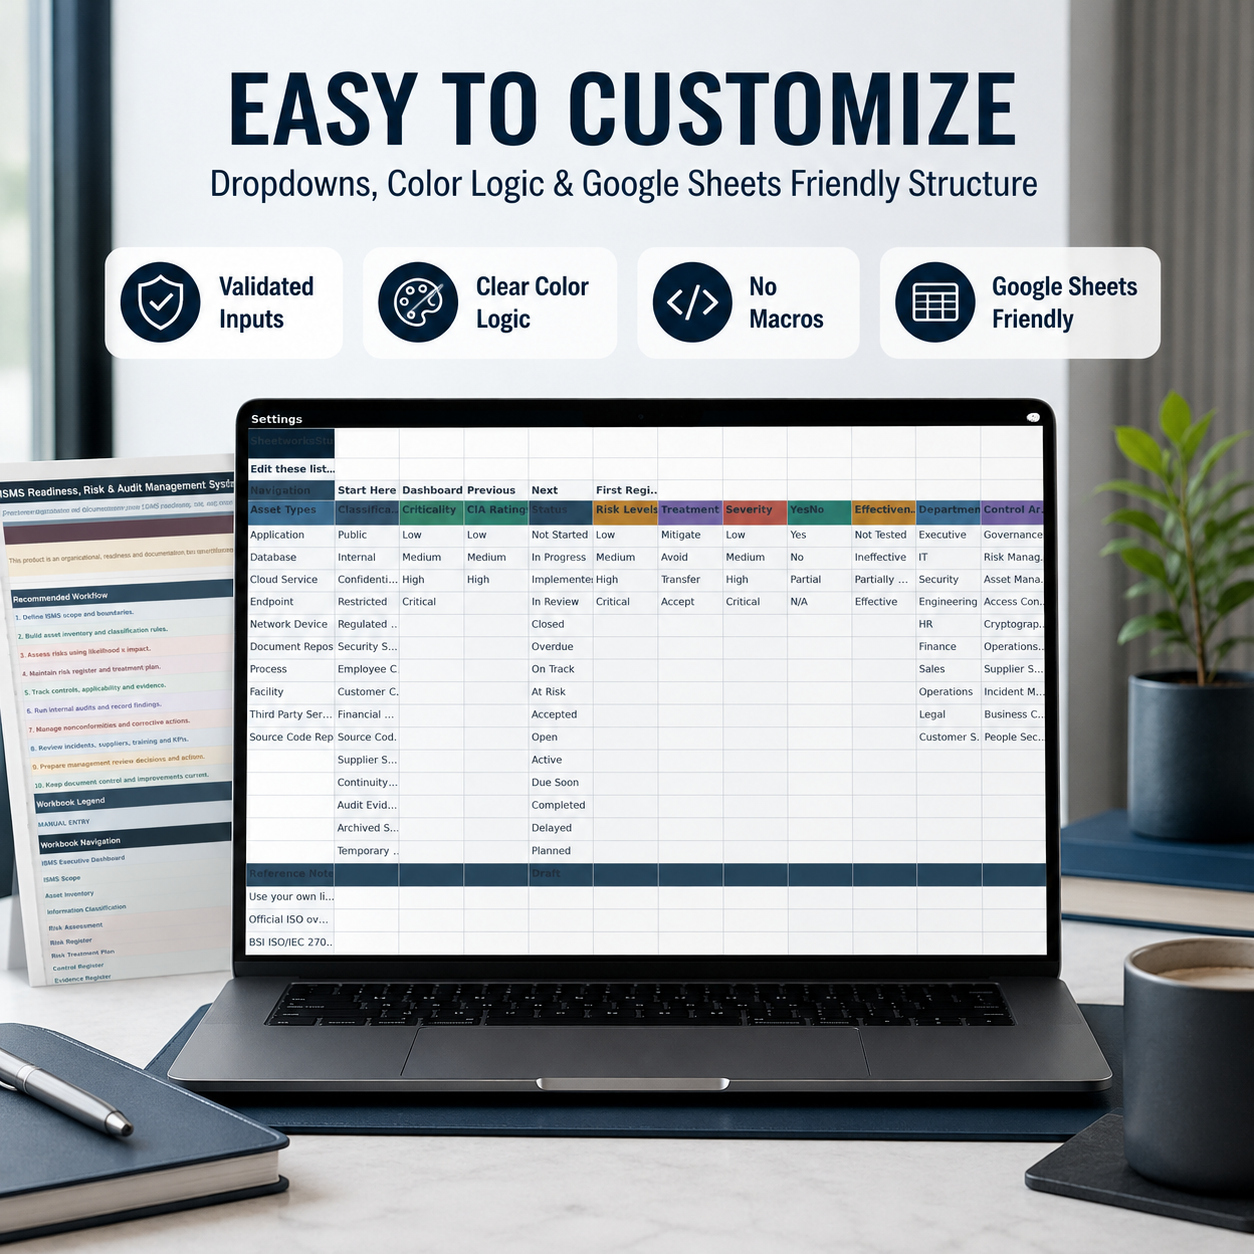
Users can define ISMS scope, maintain information assets and classifications, assess inherent and residual risk, plan risk treatment, manage controls and evidence, document applicability decisions, coordinate internal audits, manage findings and nonconformities, track corrective actions, monitor suppliers and incidents, record training, manage security objectives, and prepare management reviews.
The overall objective is to improve traceability, ownership, documentation consistency, management visibility, and readiness discipline while keeping official ISO control references separate from the template and under the organization’s own licensed standard materials.
This toolkit is particularly suitable for:
Small and medium-sized businesses
SaaS companies
IT organizations
Information-security teams
ISMS managers and coordinators
Risk and compliance teams
Internal audit teams
Security managers
Operations leaders
ISO 27001 consultants
GRC consultants
Management consultants
Organizations structuring an ISMS readiness program
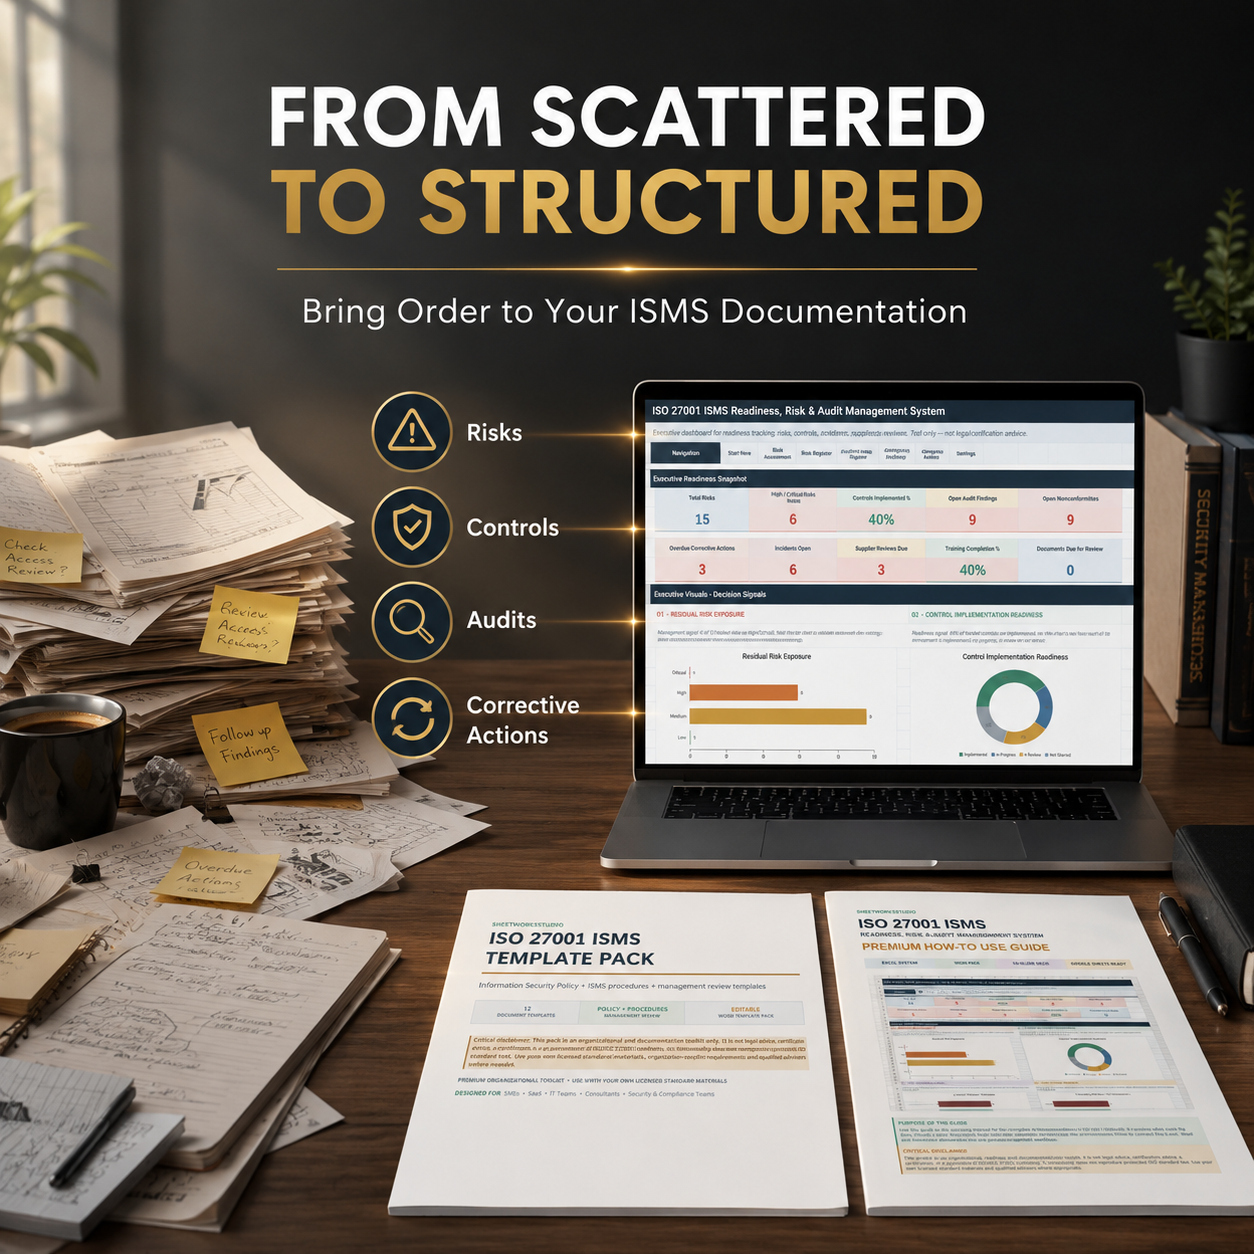
It is especially useful when risks, controls, evidence, audits, corrective actions, supplier reviews, training, objectives, and management-review records are currently distributed across disconnected files and a more consistent management framework is required.
This toolkit does not replace specialist GRC platforms, SIEM systems, security-monitoring tools, ticketing systems, document-management systems, enterprise audit software, or professional certification services.
It does not contain protected ISO/IEC 27001 standard text, official control descriptions, certification decisions, legal interpretations, automatic compliance determinations, live security feeds, APIs, vulnerability scanning, or external system integrations.
It does not constitute legal advice, certification advice, regulatory advice, security assurance, or a guarantee of ISO/IEC 27001 conformity or certification.
Official requirements and control references should be obtained from appropriately licensed ISO materials and interpreted for the organization’s circumstances with qualified professionals where appropriate.